 Do Son
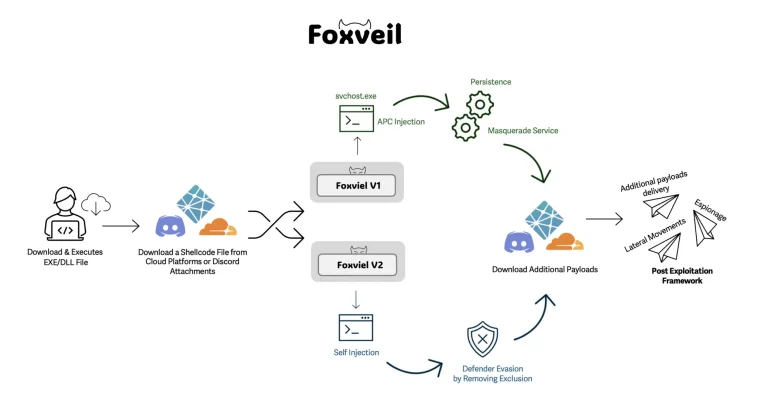
Cato CTRL discovers Foxveil, a new malware loader abusing Cloudflare, Netlify & Discord to bypass defenses. Active since Aug 2025. Learn the signs.
Netlify

Trellix warns: "Browser-in-the-Browser" phishing creates perfect fake Facebook login pop-ups. Learn how this invisible trap steals credentials.

APT SideWinder launched Operation SouthNet, targeting South Asia with over 50 malicious phishing portals hosted on Netlify and pages.dev to steal government and military credentials.