
 Do Son
Node.js patched 11 vulnerabilities in its July 2026 release. The high-severity bugs include a HTTP/2 use-after-free (CVE-2026-56848). Update now.
Node.js Security
A decompress npm vulnerability (CVE-2026-53486, CVSS 9.1) lets crafted archives write files outside the target folder via path traversal. Patch now.

CVE-2026-48713 exposes i18next prototype pollution in i18next-fs-backend, a CVSS 9.1 flaw threatening 1M+ weekly downloads. Update to 2.6.6 now.
Critical 9.8 CVSS flaws trigger Vitest remote code execution risks. Discover how to protect your testing environments and patch these bugs immediately.

CVE-2026-9277 (CVSS 9.2) lets attackers inject commands via the shell-quote npm package. Check your dependencies and upgrade now.
A critical 9.4 CVSS vulnerability in protobuf.js puts 220 million monthly downloads at risk of RCE. Patch your Node.js and browser apps to version 8.0.1+.

Fastify (25M+ downloads) reveals CVE-2026-33806. A public PoC exploit shows how a single space bypasses schema validation. Upgrade to v5.8.5 now to stay safe.

Axios CVE-2025-62718 allows a critical NO_PROXY bypass via hostname normalization errors. Protect your internal network from SSRF—patch or normalize today!
Node-convict (CVE-2026-33864) faces a 9.4 CVSS Prototype Pollution flaw. Bypass filters and hijack Node.js apps. Update to version 6.2.5 now to stay secure.
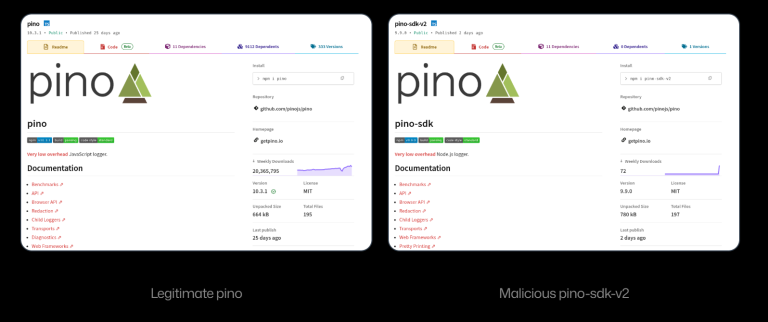
SafeDep uncovers pino-sdk-v2, a malicious npm package impersonating the pino logger to silently steal .env secrets and exfiltrate them via Discord.

Parse Server patches a critical 9.1 CVSS vulnerability (CVE-2026-27804). Attackers can forge Google tokens using "alg: none" to hijack any linked user account.

Node.js DoS flaw CVE-2026-26278 in fast-xml-parser freezes event loops via XML entity expansion. 46M weekly downloads affected. Update to version 5.3.6.