 Do Son
Patch now. Details and PoC exploit code are public for this critical CVSS 9.1 Vite Dev Server RCE flaw in exposed dev hosts.
nodejs
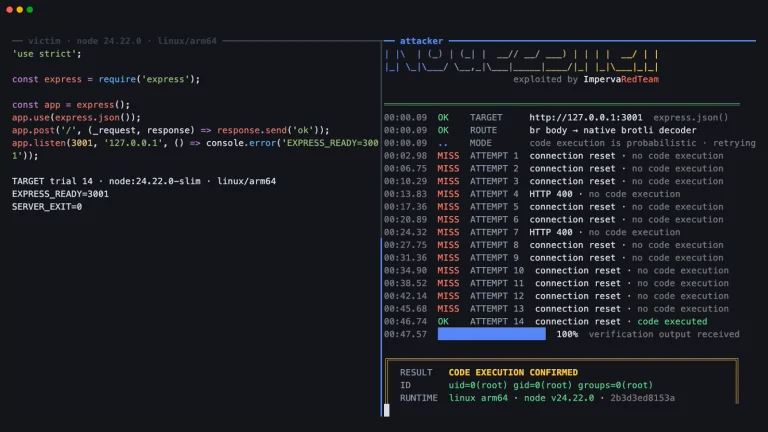
The HTTP2Shell vulnerability expands Node2Shell risks across HTTP stacks, enabling remote code execution via flawed Brotli decompression engines.
Node.js 26.12.1, 24.22.1 and 22.23.4 fix 10 flaws, including Brotli RCE CVE-2026-111497 and TLS hostname check bypasses. See which versions to install.

A vm2 sandbox escape (CVE-2026-47686, CVSS 9.9) with public PoC lets attackers hijack the host. Two more critical flaws patched in 3.11.6.

Node.js patched 11 vulnerabilities in its July 2026 release. The high-severity bugs include a HTTP/2 use-after-free (CVE-2026-56848). Update now.
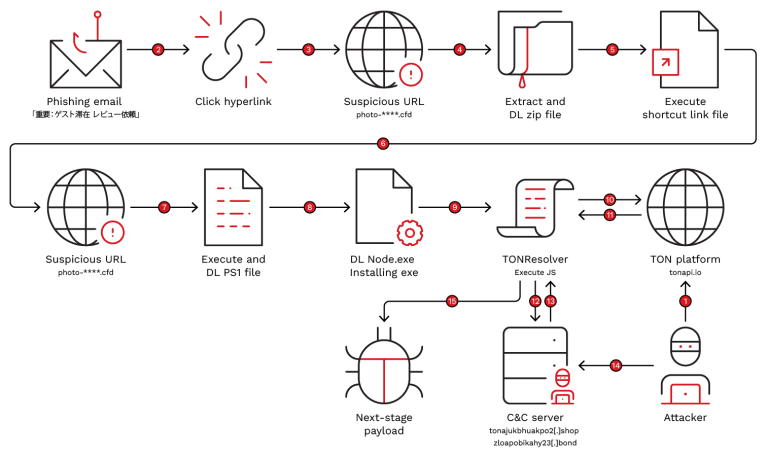
Trend Micro found TONResolver malware hitting Booking.com hotel partners in Japan. It hides its C2 in a TON blockchain smart contract. Details inside.
An active hospitality malware campaign uses photo lures and authentication laundering to infect hotel networks with a persistent Node.js implant.
Four undici vulnerabilities (CVE-2026-6734, CVE-2026-9697) affect the Node.js HTTP client, which sees 133M weekly downloads. Update undici now.

Protect your servers with the latest Node.js security updates. Patch critical vulnerabilities like CVE-2026-48933 to secure your infrastructure today.

Elastic Security Labs exposes NOVABLIGHT, a NodeJS-based infostealer-botnet MaaS disguised as an "educational tool," actively distributed via Telegram and targeting victims with fake game installers.

Red Canary uncovers Mocha Manakin, a new threat group using "paste and run" social engineering to deploy NodeInitRAT, a custom NodeJS RAT with potential ransomware links.

CVE-2024-27980: Successful exploitation could give attackers the ability to remotely run arbitrary commands on a vulnerable system.

Coyote represents a paradigm shift in the realm of Brazilian banking Trojans, embracing modern technologies like Node.js, .NET