 Do Son
Akamai uncovers CVE-2026-32202: A zero-click LNK flaw used by APT28 to steal Windows NTLM hashes silently. No user interaction required. Patch alert!
NTLM Relay

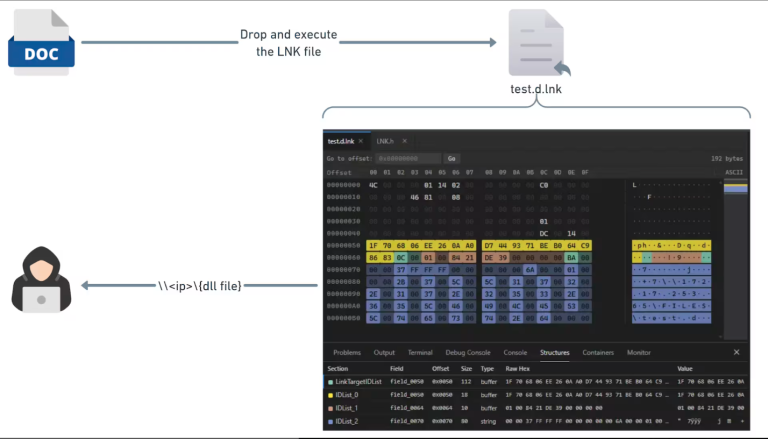
A new Zero-Click NTLM leak bypasses Microsoft's LNK patch, allowing unauthenticated NTLM hash theft on patched systems. The PoC works by exploiting UNC paths and the default shell32.dll icon reference.

A spoofing flaw (CVE-2025-26685) in Microsoft Defender for Identity, combined with other vulnerabilities, enables unauthenticated privilege escalation to Active Directory.

A vulnerability in Microsoft Access that allows cybercriminals to exploit the "linking to remote SQL Server tables" feature