 Do Son
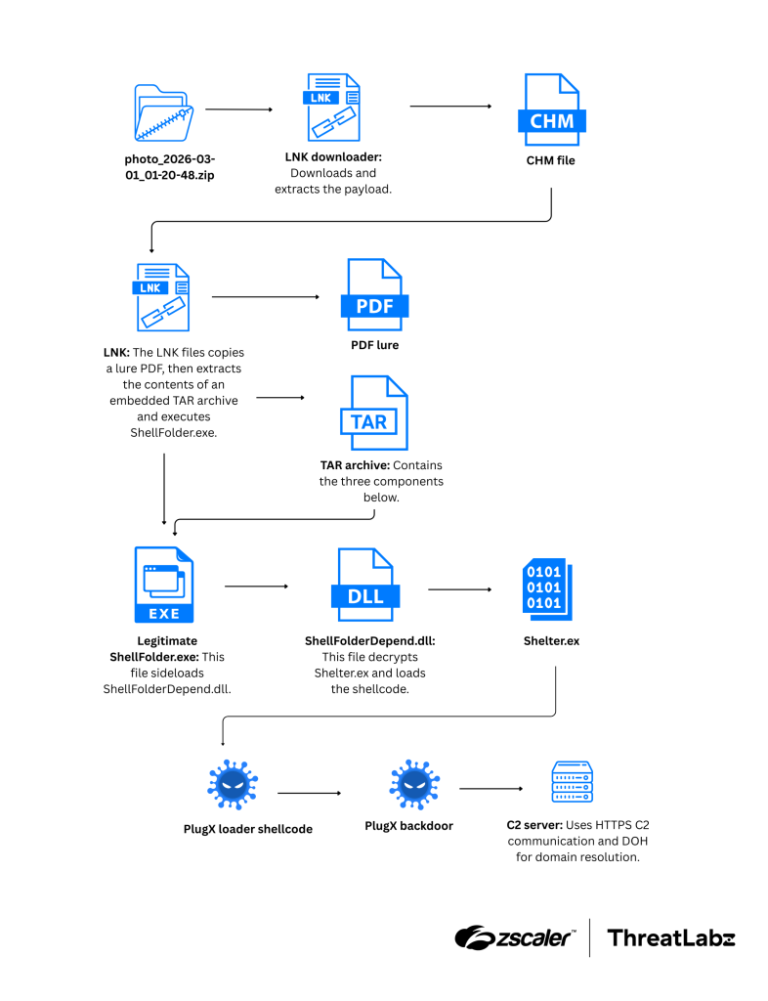
ThreatLabz reveals how China-nexus actor Mustang Panda weaponized Middle East conflict lures to deploy a stealthy PlugX backdoor within 24 hours.
Obfuscation

Cyfirma uncovers the RuTaxi Android banking Trojan, a highly persistent malware using VNC capabilities to hijack Russian bank accounts and crypto wallets.

New LTX Stealer malware abuses Node.js & Inno Setup to bypass antivirus. This $10 tool steals browser passwords & crypto wallets. Stay alert.

Zscaler analyzes GuLoader's evolution. The malware uses Google Drive, polymorphic code, and exception-based obfuscation to evade detection.

Unit 42 unmasks VVS Stealer, a Python-based threat using Pyarmor obfuscation to bypass AV, hijack Discord sessions, and steal browser credentials.

WithSecure exposed TangleCrypt, a new ransomware packer that uses LZ78/XOR and embedded PE resources to hide the STONESTOP EDR killer. However, coding flaws cause unexpected crashes.

K7 Labs exposed a Python malware using multi-layer encoding (Base64/BZ2/Zlib) and a PNG-disguised RAR archive. The payload executes in memory and achieves stealth by injecting into cvtres.exe.

CRIL exposed fileless phishing using malicious HTML attachments. Credentials are stolen via a fake Adobe login and instantly exfiltrated to Telegram bots, bypassing traditional domain filters.
Cleafy uncovers Klopatra, a new Android RAT using commercial Virbox obfuscation and native code to target banks in Spain/Italy, allowing invisible remote device control.Export to Sheets

A new DarkCloud infostealer variant uses VB6 obfuscation and anti-analysis techniques to steal credentials and crypto wallets from MetaMask, Exodus, and more.

Microsoft blocked a credential phishing campaign that used AI to generate complex, verbose code in an SVG file to obfuscate its payload and evade defenses.

Unit 42 uncovers DarkCloud Stealer's new evasion tactics, including heavily obfuscated JavaScript/WSF loaders and a final VB6 payload that injects into RegAsm.exe to bypass detection.

ThreatLabz reveals the evolution of Raspberry Robin malware, now featuring stronger encryption, complex obfuscation, and a new privilege escalation exploit to bypass detection.

Unit 42 exposes SLOW#TEMPEST, a new malware variant using advanced CFG obfuscation and indirect function calls to evade static analysis, making it nearly impossible to detect.

Sucuri uncovers a stealthy WordPress malware plugin that mimics your domain to inject SEO spam for bots while remaining invisible to users, evading detection.

Banana Squad has compromised over 60 GitHub repos with malicious Python files, using UI quirks to hide malware and steal data from developers via a sophisticated supply chain attack.

Censys uncovers "sostener.vbs," an obfuscated VBScript launching a multi-stage RAT delivery pipeline, affecting dozens and potentially linked to Blind Eagle APT.

A new global malware campaign delivers PureHVNC RAT via fake job offers and complex, multi-stage obfuscation, making detection extremely difficult.

A new malware family, DOUBLELOADER, leverages the ALCATRAZ obfuscator to deploy RHADAMANTHYS infostealer with advanced evasion techniques.

A technical analysis of the More_Eggs malware, detailing its use of ieuinit.exe abuse, DLL side-loading, and polymorphic JavaScript.

Attackers used Google Calendar invites and Unicode PUAs to deliver obfuscated malware via NPM. Aikido uncovers this novel supply chain attack.

Sophisticated malware hides inside image files within .NET apps to secretly infect systems, targeting finance in Türkiye and logistics in Asia.