
 Do Son
Weekly Triage: 1,134 new vulnerabilities found, including a 9.8 critical bypass in cPanel/WHM and active Express.js logic flaws. Patch your systems now.
patch management

Critical Remote Command Injection flaws in PHP Composer's Perforce integration (CVE-2026-40176 & CVE-2026-40261) could lead to full system compromise. Patch now.
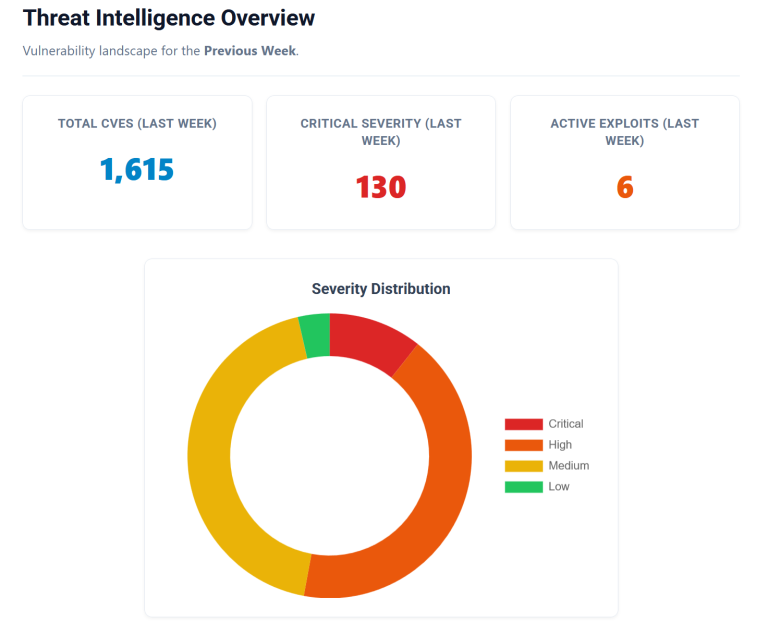
Weekly vulnerability digest (April 6-12, 2026): 1,615 new flaws, CISA KEV alerts for Ivanti and Fortinet, and critical RCE in AI tools like Flowise.

CISA adds critical Ivanti EPMM flaw (CVE-2026-1340) to KEV catalog. The 9.8 CVSS code injection allows unauthenticated RCE. Patch mandated by April 11!
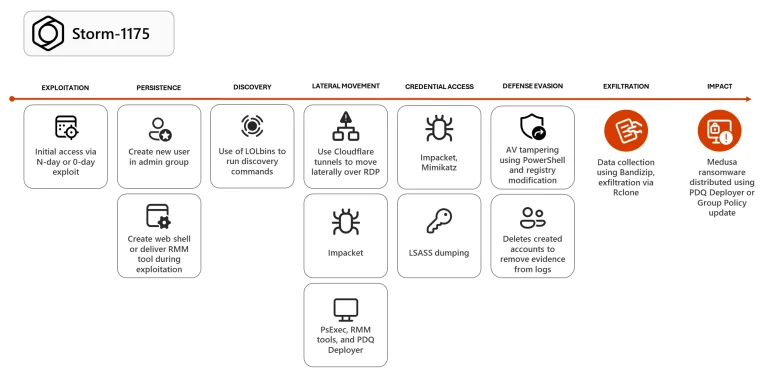
Microsoft exposes Storm-1175: a high-speed threat actor deploying Medusa ransomware in under 24 hours via zero-day exploits. Learn how to stop the blitz.

1,361 vulnerabilities found this week: 129 are critical. Prioritize Chrome’s Dawn exploit, FortiClient EMS, and new AI pipeline attacks. Get the full list.

Linux legend Greg Kroah-Hartman reveals how AI is catching bugs in the kernel. Discover why 40 out of 60 AI fixes were "genuinely efficacious" in 2026.

1,740 new vulnerabilities, 147 critical. From F5 crashes to a Trivy supply chain attack, here’s your high-priority triage list for March 2026.

Researchers found two flaws in Spring Framework (CVE-2026-22737 & CVE-2026-22735) allowing path bypasses and stream corruption. Patch your apps today.

A 5-year-old flaw in Linux x86 page fault handling has finally been patched in Kernel 6.19. Discover how engineers fixed this "combinatorial nightmare."

Kaspersky's Q1 2025 report highlights a surge in attacks on aging systems, unpatched flaws, and mismanaged updates, urging vigilance and prompt action.

Ivanti fixes EPMM flaws CVE-2025-4427 and CVE-2025-4428, exploited in the wild for unauthenticated RCE. Update now or apply strict API access controls.
Fortinet warns of a novel persistence exploit using symbolic links in FortiGate SSL-VPNs. Upgrade to patched FortiOS versions to mitigate the threat.