 Do Son
Linux kernel vulnerabilities this week: 129 CVEs, including critical iSCSI flaws CVE-2026-99154 and CVE-2026-99153. Get the kernel security update.
patch management
PHP2Shell affected products list: vendor patch status for CVE-2026-109618 and CVE-2026-109619 across PAN-OS, QNAP, Cisco, Citrix, F5 and more.
Fortinet security updates for FortiOS, FortiManager and FortiAnalyzer fix critical AI-found flaws. Advisories follow November 10. Patch now.
Atlassian's October 2026 security bulletin fixes 176 third-party vulnerabilities, 14 critical, in Jira, Confluence, Crowd and Bitbucket.
Microsoft's September 2026 V2 Exchange Server security updates add CVE-2026-96940 for Exchange SE, 2019 and 2016. Install them now.
 ddos-admin
CVE Alerts turns CVE, KEV, and EPSS data into real-time alerts via email, Slack, Teams, and GitHub Issues. Start your 14-day free trial.
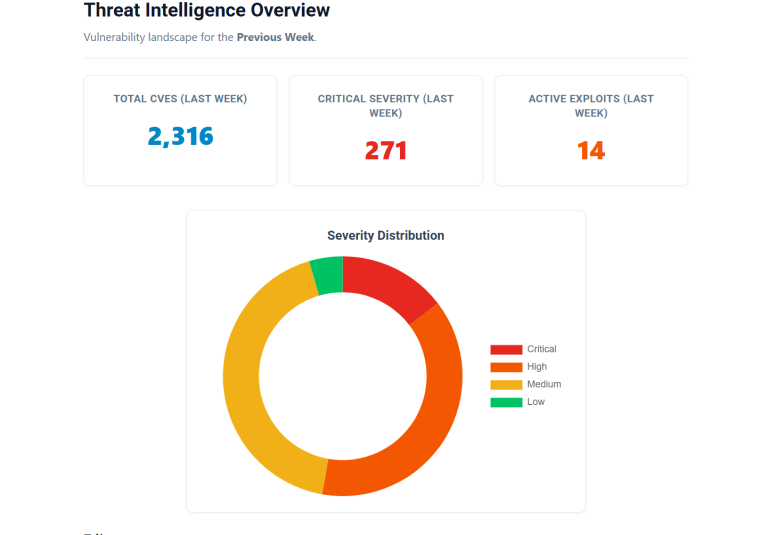
This weekly CVE report covers 10 exploited vulnerabilities added to CISA KEV and 2,316 new CVEs from Aug 31 to Sep 6, 2026. Patch fast.
This weekly CVE report covers 2,488 new CVEs and 11 exploited vulnerabilities added to the CISA KEV catalog for Aug 24-30, 2026. See the priorities.
This CVE weekly report tracks 3,179 new CVEs and 9 exploited vulnerabilities added to CISA KEV, from Ray and MLflow to VMware and Apple.

This weekly CVE report covers 1,877 new CVEs and 6 actively exploited vulnerabilities in CISA KEV, including N-able, TeamCity, and Langflow.

ManageEngine fixed an ADAudit Plus vulnerability, CVE-2026-6516, a CVSS 10 unauthenticated remote code execution flaw. Update to build 8606 now.

Google's Chrome security update fixes four high-severity bugs, including CVE-2026-16807, a Codecs flaw that could enable a sandbox escape. Update now.

Apache Syncope patches an SQL injection (CVE-2026-57308) and a privilege escalation flaw (CVE-2026-62183). Update to 4.0.7 or 4.1.2 to stay safe.

WSUS sync timeouts and failed Windows Update scans stem from mis-published test detectoids. Microsoft has mitigated it and published a cleanup.
7-Zip vulnerability CVE-2026-14266 (CVSS 7.0) allows remote code execution via crafted XZ data. Update to 7-Zip 26.02. No exploitation confirmed.

This weekly CVE report covers 1,909 new vulnerabilities from June 22-28, 2026. CISA flagged six as exploited, including CVE-2026-20230.

New updates patch critical Spring security vulnerabilities, mitigating cross-site scripting and server-side request forgery risks across multiple versions.
Deploy the latest Spring GraphQL security patches to remediate critical unsafe deserialization flaws and cross-site WebSocket hijacking vulnerabilities.
A critical PeopleSoft RCE security bug allows an unauthenticated HTTP exploit to execute code. Learn how to patch CVE-2026-35273 immediately.

New Ivanti EPMM security updates address high-severity flaws that could allow a remote authenticated attacker to achieve remote code execution.

GnuTLS v3.8.13 fixes critical heap overwrites, identity truncation, and OCSP bypasses. Secure your Linux comms and upgrade to the latest version now.

Apache MINA issues emergency patches for two 9.8 CVSS RCE flaws left behind by mistake. Unauthenticated attackers can bypass filters via deserialization.