 Do Son
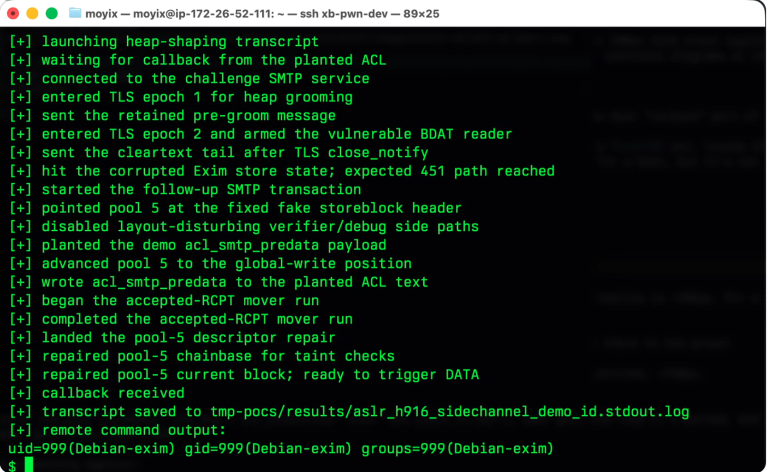
Urgent: Exim fixes a 9.8 severity RCE (CVE-2026-45185) affecting GnuTLS builds. A single-byte heap corruption allows for server takeover. Update to 4.99.3 now!
Patch Now

IBM issues a 9.8 critical alert for API Connect! CVE-2025-13915 allows unauthenticated remote access. Update to v10.0.11 or apply iFixes now.

Symfony patched a High-severity flaw (CVE-2025-64500) in its Request component. Improper PATH_INFO parsing allows attackers to bypass access control rules in vulnerable applications.

Cisco patches a Critical 9.9 zero-day (CVE-2025-20333) in ASA/FTD VPN web servers. Authenticated attackers can exploit the flaw for root-level Remote Code Execution.

GitLab urges immediate upgrade to patch versions 18.4.1+ for high-severity DoS flaws that allowed unauthenticated attackers to crash self-managed instances.

A critical vulnerability was found in Cisco Identity Services Engine (ISE) and Cisco ISE-PIC. Tracked as CVE-2025-20337,...

A critical flaw (CVE-2025-4322) in the WordPress Motors theme allows unauthenticated attackers to reset passwords for full site takeover.

Mitel warns of a critical path traversal flaw (CVSS 9.8) in MiCollab, allowing unauthenticated attackers to access provisioning data and perform admin actions.

A high-severity flaw (CVE-2025-37100) in HPE Aruba Private 5G Core allows unauthorized access to sensitive system files. Update to 1.25.1.1 immediately!

CISA issues critical warning for CyberData SIP Emergency Intercom (Model 011209) with severe vulnerabilities (CVSS 9.8), risking remote access and code execution. Update now.

ISC uncovers security flaws in its Kea DHCP server, including privilege escalation and data leakage. Update to Kea 2.4.2, 2.6.3, or 2.7.9 immediately.

Google Chrome 136.0.7103.113/.114 patches 4 security bugs including CVE-2025-4664, a zero-day exploit found in the wild. Users urged to update immediately.
Node.js Alerts: High-Severity Flaw (CVE-2025-23166) Risks Remote System Crashes! Update Immediately!

Node.js Alerts: High-Severity Flaw (CVE-2025-23166) Risks Remote System Crashes! Update Immediately!
Node.js security patches address high-severity CVE-2025-23166, risking remote crashes, and other flaws. Update your 20.x-24.x lines now!