 Do Son
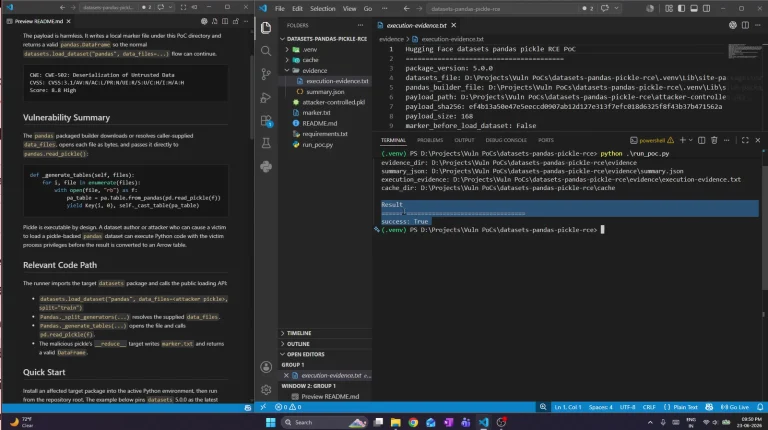
Hugging Face datasets RCE CVE-2026-57845 (CVSS 8.8) has a public proof-of-concept. The library sees 38M monthly downloads, and no fixed release exists.
Pickle Deserialization
CVE-2026-14890 is an unpatched SGLang vulnerability enabling unauthenticated remote code execution through pickle deserialization. Restrict access now.

CERT/CC warns of unpatched critical flaws in SGLang (CVE-2026-7301) exposing AI inference models to unauthenticated RCE. Restrict your ports now!

Critical 9.8 CVSS unpatched RCE flaws in the SGLang AI framework (CVE-2026-3059 & CVE-2026-3060) expose servers via unsafe Python pickle deserialization.