
 Do Son
A new Rapid7 report reveals four critical flaws in Securden's Privileged Access Manager, including authentication bypass and RCE, that could expose passwords and secrets.
Privileged Access
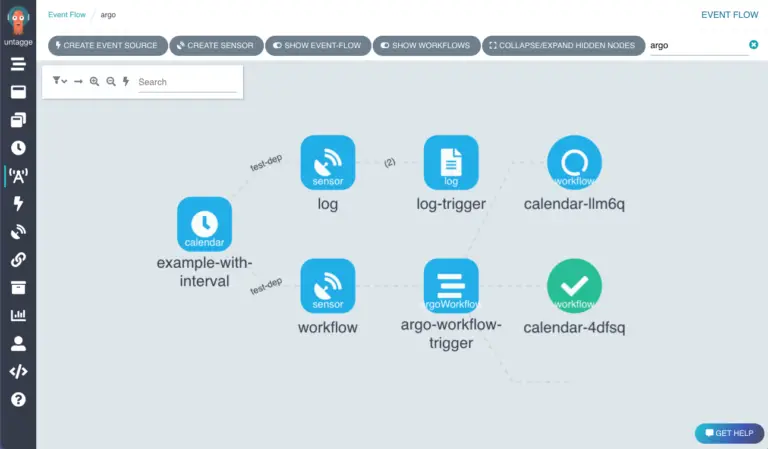
A critical vulnerability (CVE-2025-32445) in Argo Events allows users to gain privileged access to Kubernetes clusters. Upgrade to v1.9.6 to patch.