 Do Son
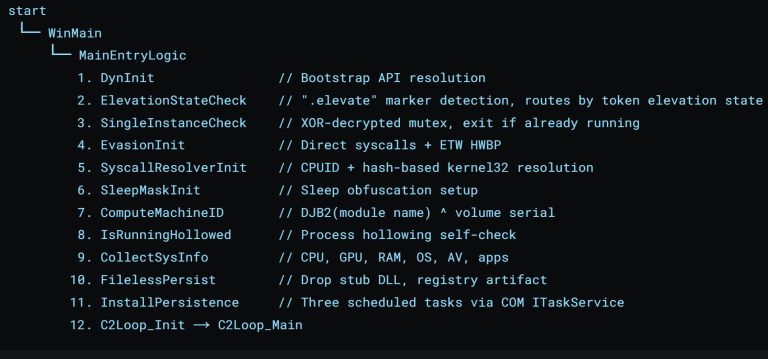
An in-depth PHANTOMPULSE malware analysis reveals a sneaky blockchain C2 channel and AI-assisted coding techniques used by advanced threats.
Process injection

Silver Fox APT targets users with fake LINE installers delivering ValleyRat. New campaign uses rare "PoolParty" injection to evade detection.

SEQRITE exposed Operation DUPEHIKE targeting Russian HR with a malicious LNK bonus lure. The DUPERUNNER implant uses PowerShell and process injection into explorer.exe to deploy the Adaptix C2 Beacon.

G DATA exposed Arkanix, a fast-evolving C++ stealer. Its premium version uses process injection and Chrome Elevator to bypass Chrome App-Bound Encryption (ABE) and steal crypto wallets and Wi-Fi passwords.

K7 Labs exposed a Python malware using multi-layer encoding (Base64/BZ2/Zlib) and a PNG-disguised RAR archive. The payload executes in memory and achieves stealth by injecting into cvtres.exe.

Despite a recent doxxing attempt, Lumma Stealer has resurfaced, integrating browser fingerprinting into its C&C to collect WebGL/Canvas signatures for sandbox evasion and victim assessment.
A new report reveals a multi-stage phishing campaign distributing DarkCloud Stealer. The malware hides its loader in a JPG file and injects code into MSBuild.exe for stealth.

Splunk uncovers XWorm's evolution: a modular RAT now delivering LockBit ransomware. It uses flexible delivery, AMSI/ETW bypasses, and process injection to evade detection.

Discover Waiting Thread Hijacking, a novel process injection technique that bypasses EDR systems. Learn how it stealthily executes code in remote processes.

Beware of cracked software and fake installers. Discover how cybercriminals exploit user trust and spread malicious payloads.

Discover how Kernel Callback Tables can be manipulated for process injection on Windows systems. Learn about the stealthy method employed by high-profile threat actors.