 Do Son
A ProFTPD ACL bypass (CVE-2026-35025, CVSS 8.6) lets logged-in FTP users reach files in restricted directories. No patch is out yet; use DefaultRoot.
ProFTPD
Full Exploit Disclosed: Public PoC and Technical Details Released for Critical ProFTPD SQL Injection
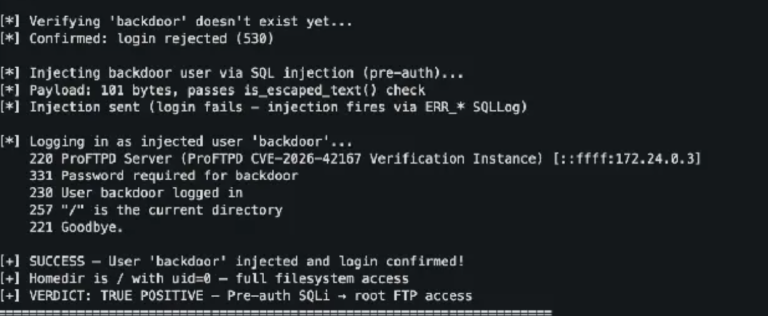
Full Exploit Disclosed: Public PoC and Technical Details Released for Critical ProFTPD SQL Injection
Critical SQLi in ProFTPD's mod_sql allows unauthenticated admin account injection. Full PoC code is public. Upgrade to v1.3.9a to secure your servers.

ProFTPD users beware! Discover the details of CVE-2024-48651, a critical vulnerability that allows attackers to gain root access.
CVE-2023-51713 exposes a dangerous out-of-bounds buffer read issue in ProFTPD's make_ftp_cmd. This flaw affects version before 1.3.8a