 Do Son
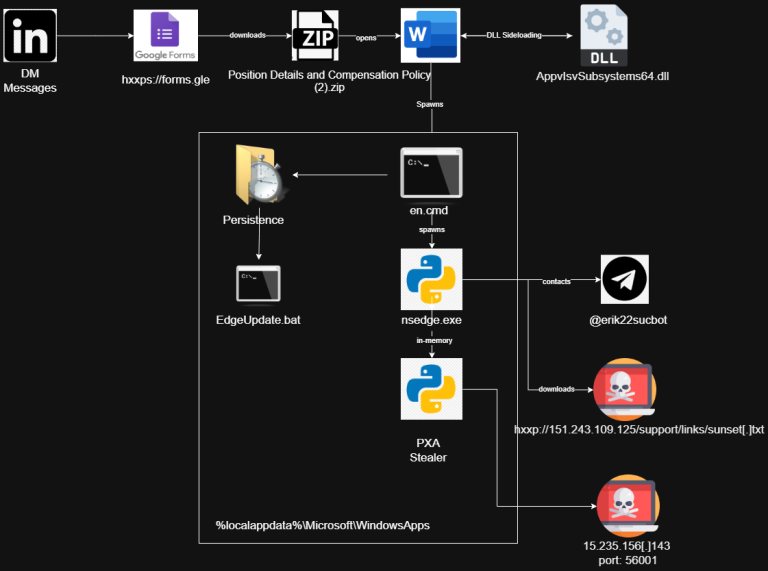
LinkedIn job seekers are being targeted by a sophisticated Vietnam-based group using PXA Stealer. This 100MB malware bypasses MFA and drains crypto wallets.
PXA Stealer
PXA Stealer activity surges in Q1 2026, targeting global finance. Learn how this Python-based malware uses Telegram and LOLBins to hijack crypto and banking data.

Huntress details a multi-stage attack that uses DLL sideloading and obfuscated Python to deliver PureRAT, a commercial-grade remote access trojan linked to PXA Stealer.

The Lone None group uses fake copyright notices to deliver a new stealer malware that focuses on crypto theft via clipboard replacement and utilizes Telegram for C2.

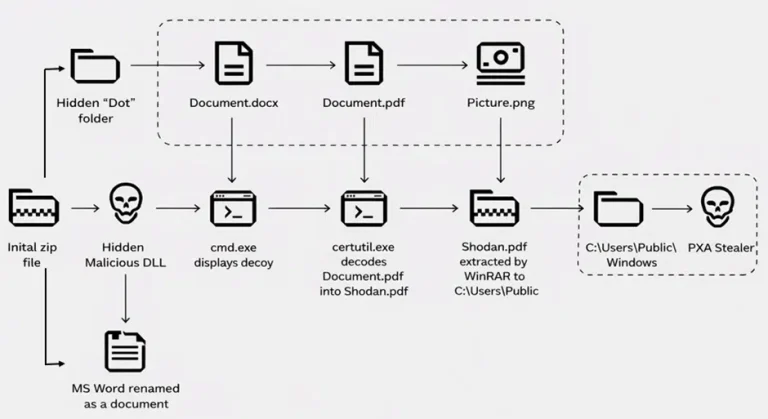
SentinelLABS and Beazley expose PXA Stealer, a Python-based infostealer campaign targeting 62 countries with stealthy DLL sideloading, decoy files, and Telegram-based data exfiltration.

Uncover the details of the sophisticated cyber campaign using the PXA Stealer malware to target government and educational sectors.