 Do Son
Zscaler uncovers an SEO poisoning campaign using fake Chocolatey and Massgrave sites to drop Armorsteal malware and Python Armorsteal malware modules.
Pyarmor

Gen Digital exposes a JDownloader site breach (May 6-7, 2026). Attackers used WDAC policies to kill antivirus and r77 rootkits for total system invisibility.
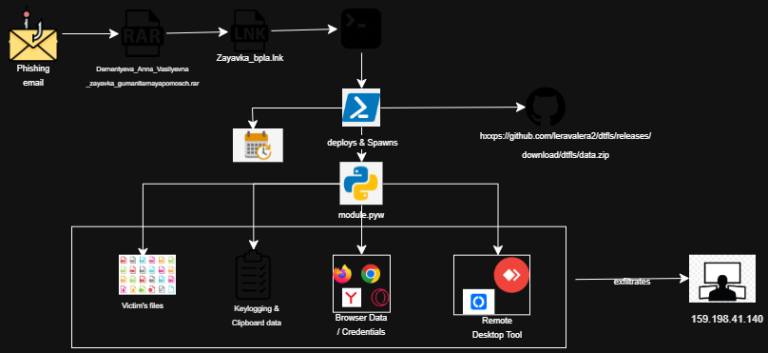
CRIL exposes a cyberespionage campaign using fake humanitarian aid forms to deploy fileless Python malware via GitHub for full-spectrum surveillance.

Unit 42 unmasks VVS Stealer, a Python-based threat using Pyarmor obfuscation to bypass AV, hijack Discord sessions, and steal browser credentials.