 Do Son
QNAP PHP2Shell vulnerabilities CVE-2026-109618 and CVE-2026-109619 affect QTS, QuTS hero and apps. No patch yet, so take NAS devices offline.
QNAP

QNAP QuMagie vulnerabilities let unauthenticated attackers access media files, causing information disclosure. Patch QuMagie and License Center now.
QNAP patched 14 NAS vulnerabilities in QTS, QuTS hero, and QVP, including command injection and credential-theft flaws. Update your QNAP NAS now.

QNAP warns of a critical 9.3 CVSS flaw (CVE-2026-22898) allowing remote attackers to bypass authentication and access QVR Pro surveillance systems. Patch now.
QNAP patches high-severity flaws (CVSS 8.1) in Qfiling and MARS that allow data theft and code injection. Secure your NAS by updating to the latest versions!

QNAP patched 7 zero-day flaws in QTS/QuTS hero and apps (HBS 3, Malware Remover) after being hacked by researchers at Pwn2Own Ireland 2025. Update urgently.
QNAP warns its NetBak PC Agent users to patch a critical ASP.NET Core flaw (CVSS 9.8) that allows attackers to hijack credentials via HTTP request smuggling.

Sekoia details PolarEdge, a Rust-based backdoor using a custom mbedTLS server for C2 on Cisco, QNAP, and Synology devices. The backdoor uses XOR 0x11 for config obfuscation and attempts to delete system utilities to block rivals.

QNAP patches NetBak Replicator and Qsync Central. Flaws include a DLL hijacking risk and critical SQL Injection that allows remote attackers to execute code.

QNAP has patched a critical improper authentication flaw (CVE-2025-52856) in its QVR firmware with a CVSS score of 9.3, allowing remote attackers to bypass security.
QNAP releases urgent patches for high-severity flaws in Qsync Central and File Station 5, enabling RCE and data compromise. Update immediately!
Learn about CVE-2024-50394, a vulnerability affecting QNAP Helpdesk. Update your system to prevent potential security breaches.

Security researcher c411e published a PoC exploit code for a severe vulnerability in QNAP NAS devices, identified as CVE-2024-53691
Discover the latest QNAP QTS vulnerability advisory. Learn about the security vulnerabilities affecting License Center and QTS/QuTS hero operating systems.
Urgent security advisory: Update your QNAP QuRouter network appliance now to address critical CVE-2024-48860 & CVE-2024-48861 vulnerabilities

Learn about the latest zero-day vulnerability, CVE-2024-50389, in QNAP's QuRouter network security appliance and how it was exploited during the Pwn2Own hacking contest.

QNAP swiftly addresses critical zero-day CVE-2024-50388 flaw in HBS 3 Hybrid Backup Sync software, preventing potential security breaches.
CVE-2024-32766 (CVSS 10) is an OS command injection, a technique where attackers can send malicious commands to a vulnerable system
CVE-2024-21899 (CVSS 9.8): An authentication bypass vulnerability that could allow unauthorized remote access to the NAS device
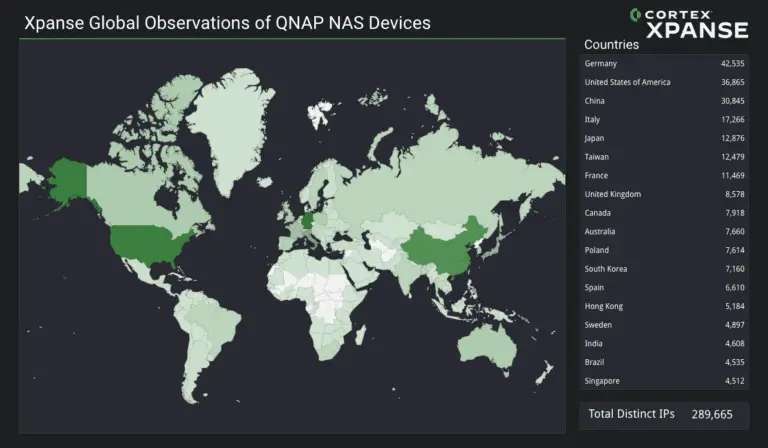
A severe zero-day vulnerability (CVE-2023-50358) has been discovered in QNAP Network Attached Storage (NAS) devices
The technical details and a PoC exploit of CVE-2023-39296 were unveiled by an independent security researcher, DCS

This flaw, identified as CVE-2023-47565 and rated with a concerning CVSS v3 score of 8.0, reveals a significant gap in network security