
 Do Son
A critical RCE flaw in DrayTek Vigor routers can be exploited without authentication via the web interface if EasyVPN is enabled, granting remote root access.
rce

Oracle issued an emergency alert for a Critical RCE flaw (CVE-2025-61882) in E-Business Suite that requires no authentication.
Redis patched a Critical (CVSS 10.0) RCE flaw (CVE-2025-49844) in Lua scripting. An authenticated attacker can exploit a Use-After-Free bug to gain code execution.

Unit 42 disclosed a Critical unauthenticated RCE flaw (CVE-2025-52906) in TOTOLINK X6000R routers, allowing remote attackers to execute arbitrary commands. Update immediately.

CISA warns of a Critical RCE flaw (CVSS 9.8) in Megasys Telenium Online Web Application. The vulnerability allows unauthenticated attackers to execute arbitrary OS commands.

OpenSSL patches three flaws, including CVE-2025-9230 (RCE/DoS risk) and a SM2 timing side-channel (CVE-2025-9231) that could allow private key recovery on ARM64.
Western Digital has patched a critical RCE flaw in its My Cloud NAS. The vulnerability allows remote attackers to execute arbitrary commands via a crafted HTTP request.

Apache Fory has a critical RCE vulnerability (CVE-2025-61622) in its pyfory module. An attacker can exploit an unguarded pickle fallback to execute arbitrary code.

A critical RCE flaw (CVSS 10) in Doxense's Watchdoc print management solution allows unauthenticated attackers to execute code and take control of the print server.

Cisco patches a Critical 9.9 zero-day (CVE-2025-20333) in ASA/FTD VPN web servers. Authenticated attackers can exploit the flaw for root-level Remote Code Execution.
Cisco disclosed a Critical RCE flaw in its Firewall ASA/FTD, IOS, IOS XE, and IOS XR web services. Unauthenticated attackers can gain root access.
A high-severity flaw in the Salesforce CLI installer (CVE-2025-9844) allows for arbitrary code execution and privilege escalation on affected systems.

SolarWinds has released an urgent hotfix for its Web Help Desk software, patching an unauthenticated RCE vulnerability (CVE-2025-26399) that bypasses earlier fixes.

Libraesva has issued an urgent advisory for a command injection flaw in its ESG. The bug, which has been exploited, allows remote command execution via a malicious email.

A critical flaw (CVE-2025-41243) in Spring Cloud Gateway with a CVSS 10.0 score allows unauthenticated RCE via SpEL injection. A PoC has been released.

A new report reveals a CWMP service flaw in TP-Link routers that can be exploited for RCE. Researchers have published a detailed write-up and a PoC on GitHub.

Nokia has issued a security advisory for two high-severity flaws (RCE and authentication bypass) in its CBIS and NCS platforms. Immediate patching is urged.

A critical vulnerability in HubSpot’s Jinjava template engine (CVE-2025-59340) could lead to remote code execution. Patch immediately to secure your site.
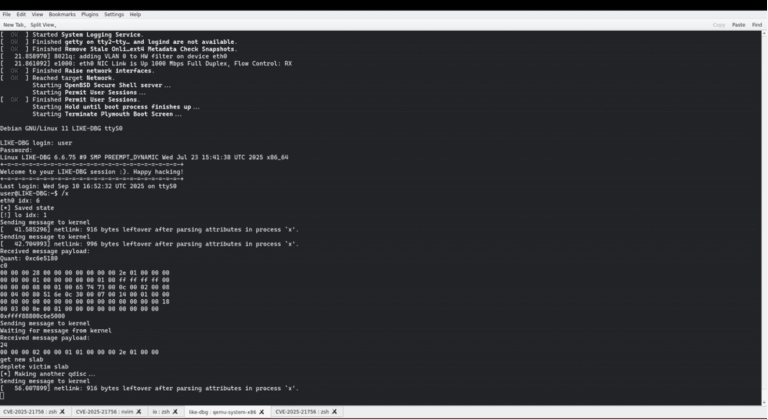
A new Linux kernel vulnerability, CVE-2025-21692, can be exploited to achieve remote code execution by manipulating the ETS qdisc, a simple but critical flaw.

NVIDIA has released a critical security update for its Triton Inference Server, fixing multiple high-severity flaws that could lead to remote code execution and DoS.

A new report details a 0-click RCE exploit chain in the Linux kernel's ksmbd module that allows an authenticated user to gain root access. A PoC has been published.

Samsung has released an emergency patch for a critical zero-day vulnerability (CVE-2025-21043) actively exploited in Android devices. Update now to protect against RCE attacks.