 Do Son
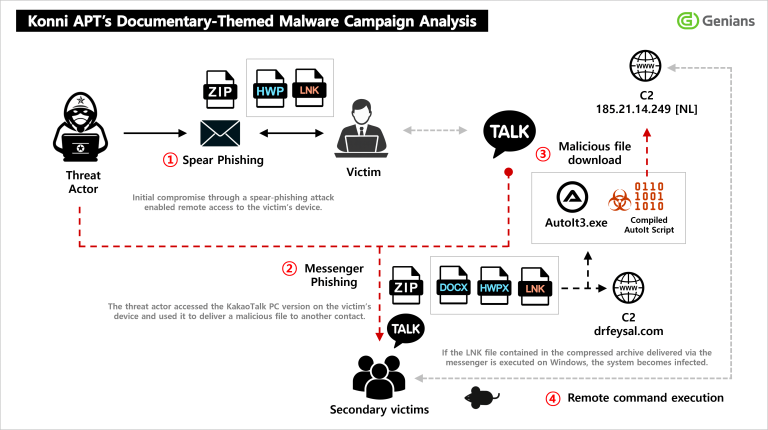
Genians Security Center reveals a new Konni APT campaign hijacking KakaoTalk PC sessions to distribute EndRAT, RftRAT, and RemcosRAT to trusted contacts.
RemcosRAT

Shadow Vector campaign uses malicious SVGs in phishing emails to deliver AsyncRAT & RemcosRAT in Colombia, leveraging advanced DLL sideloading and in-memory execution.

At the heart of the UAC-0050 threat group's arsenal is RemcosRAT, a malware for remote surveillance and control.