 Do Son
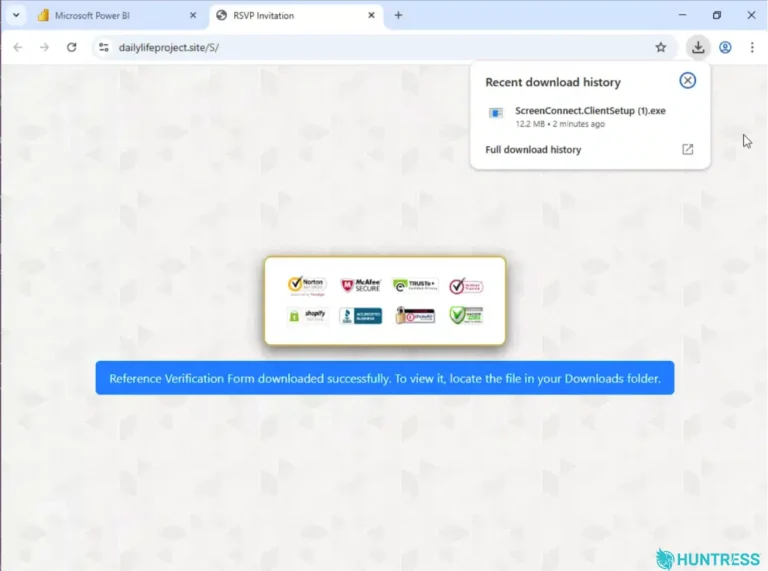
A Power BI phishing campaign uses Microsoft's real domain to install rogue ScreenConnect clients. Learn how it works and how to block it.
Remote Access
SonicWall SMA1000 vulnerability CVE-2026-102255 (CVSS 10) allows pre-auth SSRF. Three more flaws fixed. Upgrade to 12.5.0-03082 now.
Two UltraVNC repeater vulnerabilities enable arbitrary code execution (CVE-2026-7840) plus admin access via a hardcoded password. Update now.
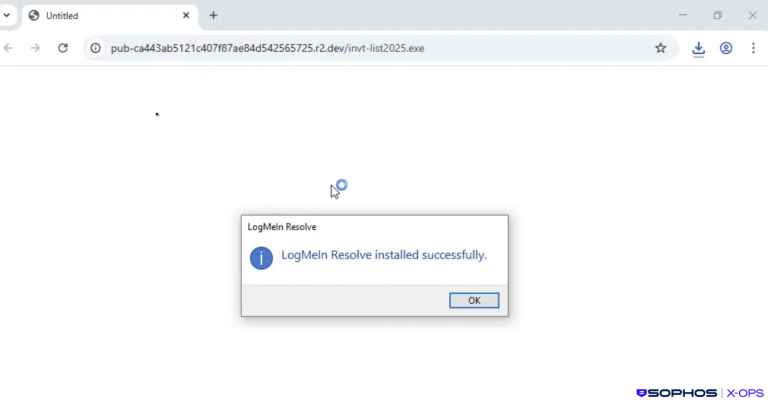
Sophos MDR uncovers STAC6405, a phishing campaign abusing RMM tools like LogMeIn for unattended access. Learn how to spot the "Special Invitation" lure.
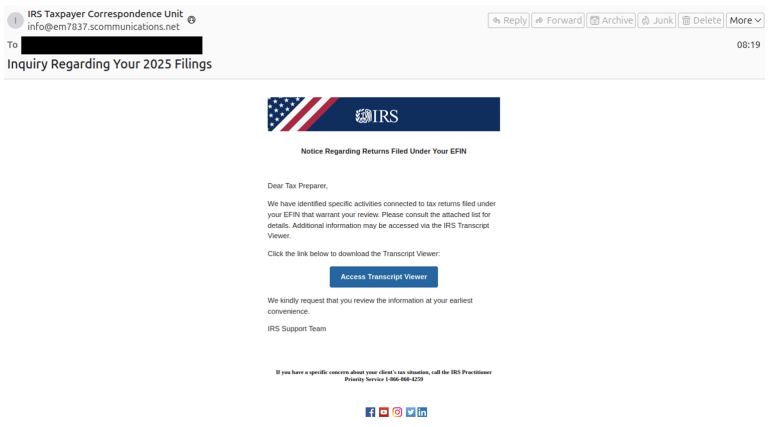
Proofpoint identifies a surge in 2026 tax scams using RMM tools (39%) to bypass security. Learn how TA4922 and TA2730 target your data this filing season.

OpenSSH 10.3 fixes critical gaps, including client-side command execution and scp privilege escalation flaws. Update your remote access stacks immediately.
Industrial connectivity specialist Helmholz GmbH & Co. KG has issued an urgent security advisory regarding multiple vulnerabilities...
A critical 9.0 CVSS vulnerability (CVE-2026-3564) in ConnectWise ScreenConnect exposes server cryptographic keys. On-premise users must update to 26.1 now.

A Critical (CVSS 9.7) DNS rebinding flaw (CVE-2025-59159) in the SillyTavern LLM interface allows remote attackers to seize full control of local AI instances and steal API keys.

The Datzbro Android Trojan is targeting seniors via fake Facebook groups and AI content. The hybrid malware can remotely control devices and steal banking credentials.

Zscaler has uncovered kkRAT, a new malware targeting Chinese-speaking users. The RAT steals crypto, hijacks clipboards, and uses RMM tools for covert, long-term control.

Siemens has disclosed a critical flaw in its SIVaaS platform. A network share is exposed without authentication, allowing unauthenticated attackers to access or alter sensitive data.

A new malware strain is targeting exposed Docker APIs, evolving from a cryptominer into a stealthy botnet that blocks ports to "own" a victim's system for exclusive use.
Siemens has disclosed a critical flaw in its SIVaaS platform. A network share is exposed without authentication, allowing unauthenticated attackers to access or alter sensitive data.

CISA warns of a critical flaw (CVE-2025-9696) in SunPower PVS6 solar inverters. Hardcoded Bluetooth encryption parameters allow attackers to gain full control.
A critical flaw in a Seiko Solutions networking device allows unauthenticated remote attackers to execute commands with root privileges. The issue has a CVSS score of 9.8.

MediaTek's September security bulletin warns of high-severity flaws in its modem that can be exploited by rogue cellular base stations for remote privilege escalation or DoS.

Dell has released a critical security advisory for ThinOS 10, with a CVSS 9.6 flaw that allows unauthenticated remote attackers to bypass protection mechanisms.

A critical flaw (CVE-2025-41702) in Welotec egOS allows unauthenticated attackers to impersonate administrators, gain full control, and disrupt industrial systems.

Cyble uncovers RedHook, a new Android banking trojan targeting Vietnamese users with sophisticated phishing, remote access, screen capture, and keylogging for full device takeover.

eSentire unveils Cyber Stealer, a new infostealer-botnet hybrid offered as a service, fusing data theft, remote control, crypto mining, and DDoS attacks into one scalable toolkit.

SentinelOne uncovers a new macOS.ZuRu variant using a trojanized Termius app. It gains persistence via LaunchDaemon and deploys a Khepri C2 beacon for remote control.