 Do Son
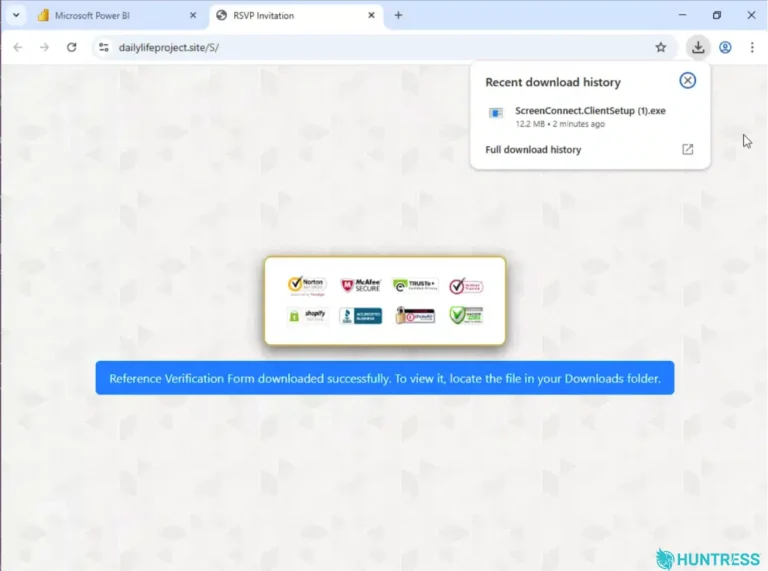
A Power BI phishing campaign uses Microsoft's real domain to install rogue ScreenConnect clients. Learn how it works and how to block it.
RMM Abuse
A new campaign shows how phishing abuses RMM tools for access. See how phishing abuses RMM tools like MSP360 to install ScreenConnect clients.
ReliaQuest found the Gryxa toolkit, AI-built malware that steals crypto credentials and spies on how defenders try to remove it across 324 hosts.
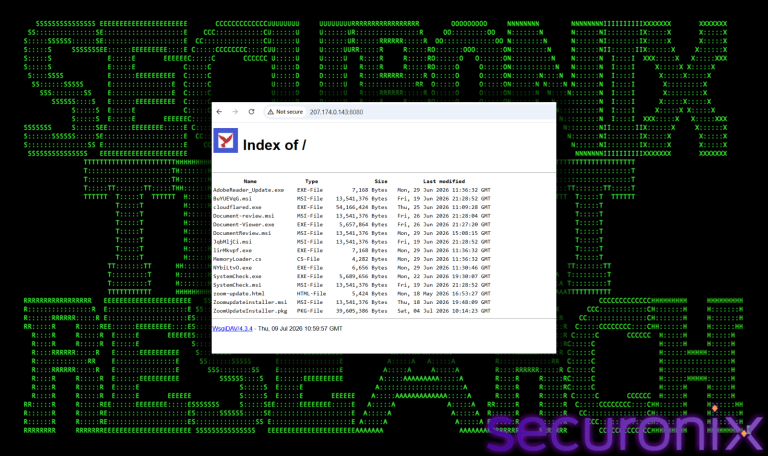
The SMOKE#SCREEN campaign abuses ScreenConnect RMM and Cloudflare tunnels via fake Zoom and Adobe update lures, Securonix reports.
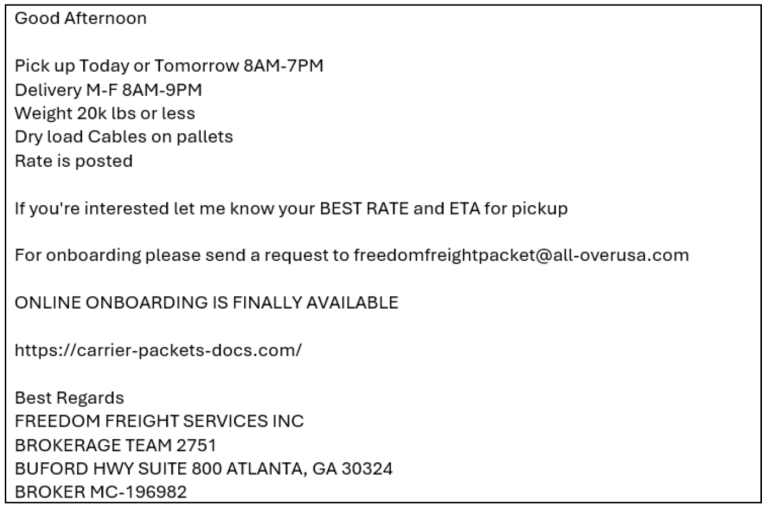
Proofpoint monitors a 30-day supply chain attack using "signing-as-a-service" to bypass Windows security. Protect your load boards and fleet payments now.
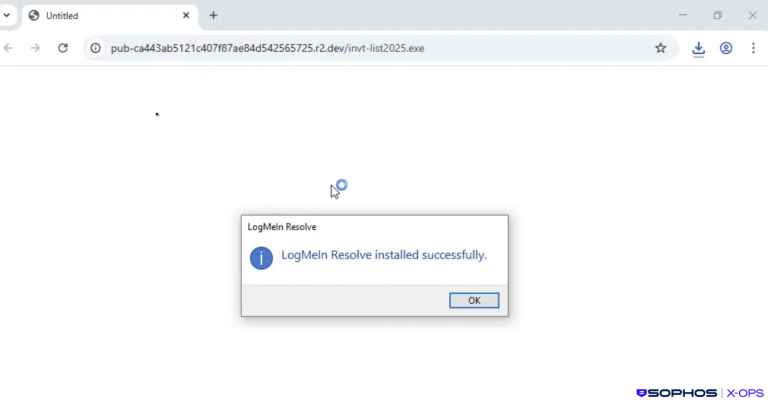
Sophos MDR uncovers STAC6405, a phishing campaign abusing RMM tools like LogMeIn for unattended access. Learn how to spot the "Special Invitation" lure.
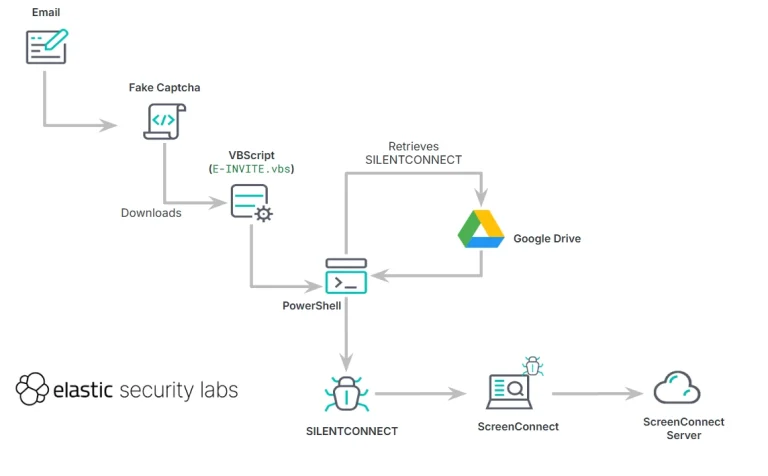
Elastic Security Labs uncovers SILENTCONNECT, a stealthy loader using Cloudflare and Google Drive to deliver RMM tools for "hands-on keyboard" attacks.
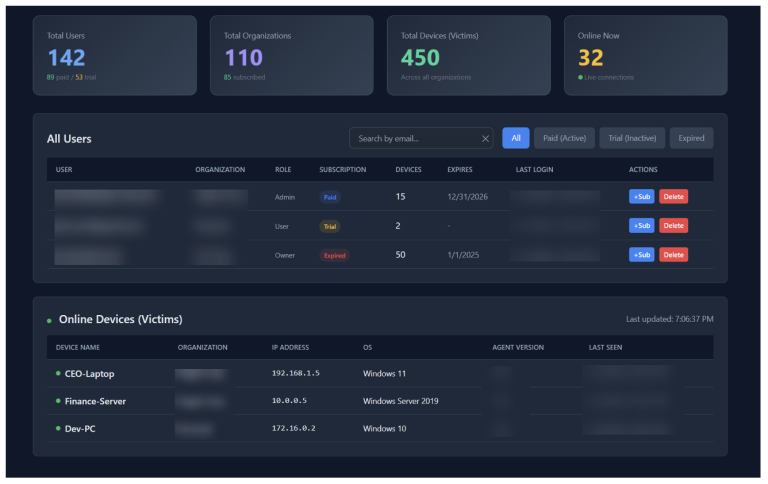
Proofpoint exposes TrustConnect, a new Malware-as-a-Service masquerading as an IT tool. The AI-assisted fake RMM software replaces dismantled threats.

ASEC warns: Hackers abuse Syncro, SuperOps & NinjaOne RMM tools via fake PDF lures. Learn how this phishing campaign installs persistent backdoors.

Cardano users alert: A fake "Eternl Desktop" app uses LogMeIn Resolve to grant hackers remote control. Verify all downloads via official channels!

Broadcom exposed a group deploying multiple RMM tools (ScreenConnect, LogMeIn, Naverisk) weeks apart to achieve redundant persistence. The likely Initial Access Broker (IAB) prepares systems for resale.

ASEC exposed PatoRAT, a Delphi RAT that hijacks LogMeIn Resolve and PDQ Connect RMM tools. Attackers use maliciously configured installers disguised as 7-Zip/Notepad++ to gain full system control.

Proofpoint exposed UNK_SmudgedSerpent, an APT using RMM tools (PDQConnect) and M365 spoofs in targeted phishing campaigns against academics and foreign policy experts with complex Iranian political lures.
Cyber-Enabled Cargo Theft: Hackers Hijack Logistics Firms with RMM Tools to Steal Physical Shipments

Cyber-Enabled Cargo Theft: Hackers Hijack Logistics Firms with RMM Tools to Steal Physical Shipments
Proofpoint exposed cyber-enabled cargo theft where criminals use phishing to deliver RMM tools (ScreenConnect, SimpleHelp). They hijack load boards and dispatch systems to steal physical freight worth millions.
NetSupport RAT Campaign Abuses ClickFix to Infect Hosts; 3 Threat Clusters Use RMM for Covert Access

NetSupport RAT Campaign Abuses ClickFix to Infect Hosts; 3 Threat Clusters Use RMM for Covert Access
eSentire exposed a surge in NetSupport RAT campaigns using the ClickFix social engineering tactic. Three threat clusters leverage a PowerShell loader to bypass AV and gain full remote access via the RMM tool.