
 Do Son
CISA added three bugs to its KEV list. An N-able N-central authentication bypass is exploited in the wild to deploy RMM tools. Patch by August 7.
RMM

Proofpoint identifies a surge in 2026 tax scams using RMM tools (39%) to bypass security. Learn how TA4922 and TA2730 target your data this filing season.

Sekoia TDR reveals Silver Fox's latest tactics. From tax-themed phishing to WhatsApp clones, this China-based group combines espionage with financial theft.
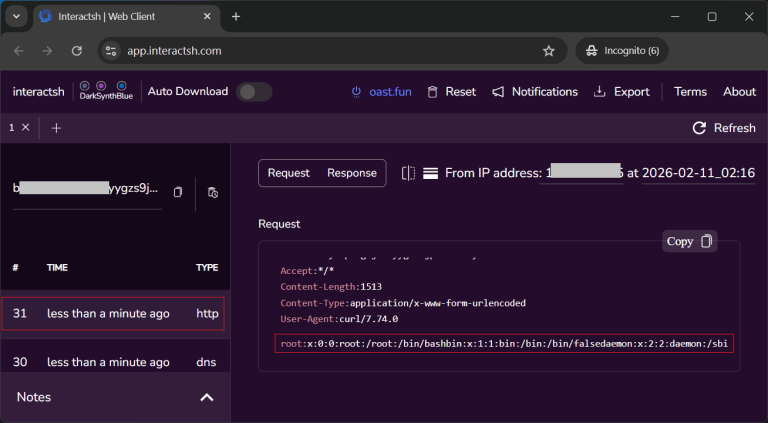
Arctic Wolf warns of CVE-2026-1731, a critical BeyondTrust flaw exploited in the wild. Attackers use it to deploy backdoors. Patch self-hosted instances now.

Medusa & DragonForce RaaS groups weaponize SimpleHelp RMM flaws (CVE-2024-57726/7/8) to gain SYSTEM-level access to customer networks. Immediate patch needed.

ConnectWise patched two high-severity flaws in Automate RMM. CVE-2025-11492 (CVSS 9.6) allows MiTM attack to intercept unencrypted agent communications and inject malicious updates. Update to 2025.9.

WithSecure uncovers a stealthy campaign using legitimate RMM tools embedded in PDFs to target European organizations, bypassing security with zero malware at initial entry.

Attackers compromised an MSP's RMM tool (SimpleHelp) to deploy DragonForce ransomware across customer environments.

Cisco Talos warns of a Brazil-focused spam campaign abusing legitimate remote access tools (N-able, PDQ) to gain full system control. Stay vigilant!