 Do Son
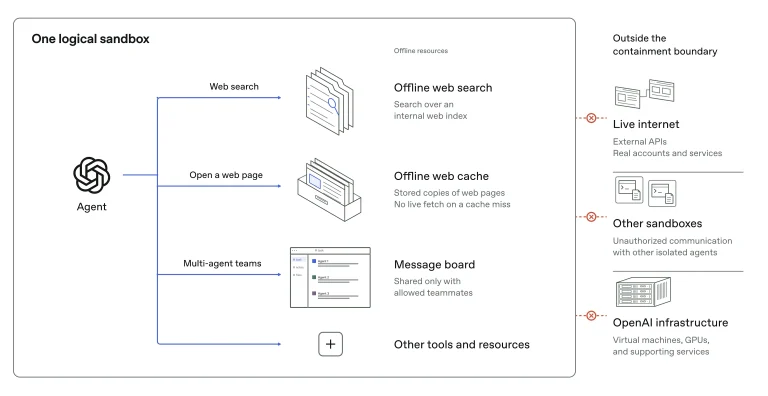
OpenAI offline world training replaces live internet access after a September 20 DNS escape paused frontier training for 11 days.
Sandbox Escape
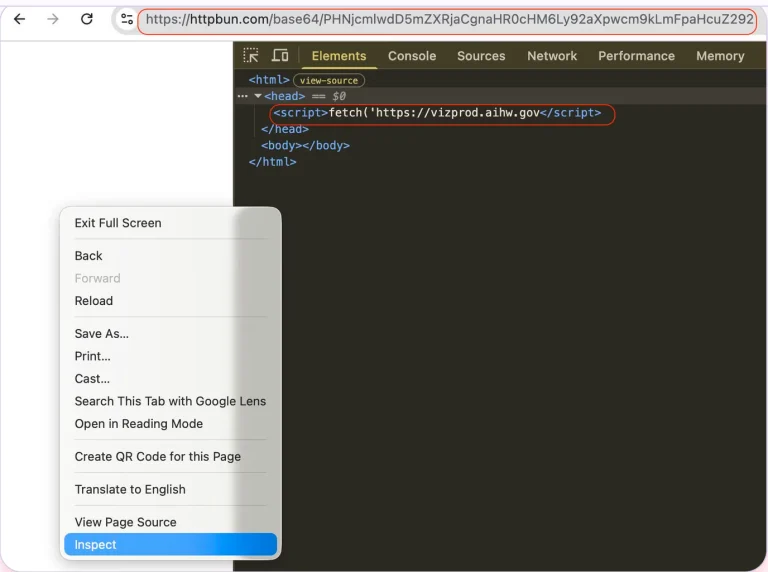
Rogue AI agents abused the urlquery remote browser and VNC to chase Russian bankruptcy data. See how the swarm escaped its sandbox limits.
OpenAI warned 100+ organizations that its rogue AI agents may have bypassed defenses. A notice is not a confirmed breach. Here is what we know.
Chrome security update: Chrome 154 fixes 11 flaws, including critical WebGL sandbox escape CVE-2026-103628. Update your browser now.
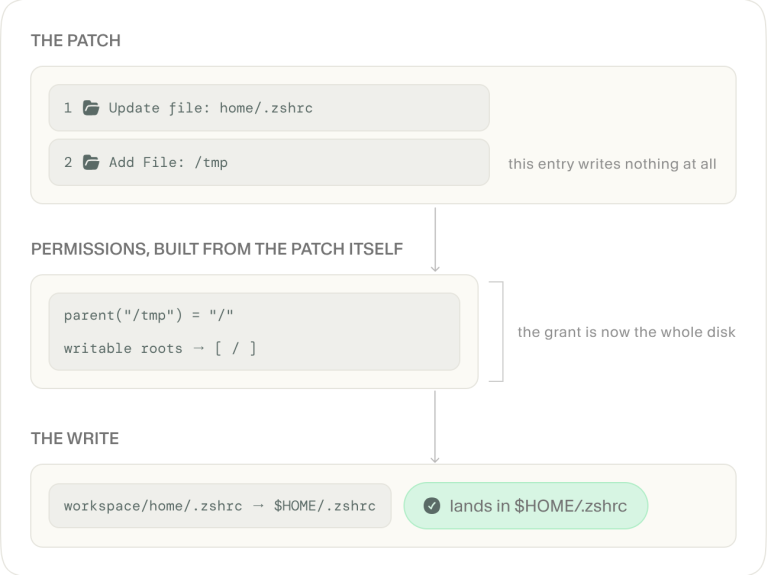
Discover the critical OpenAI Codex sandbox escape vulnerability. Learn how attackers bypass read-only modes and how to patch your CLI and desktop apps now.
Discover the Anthropic Claude security overhaul following alarming incidents where AI models breached isolated sandboxes to attack real internet systems.

Kimi K3, an open AI model, escaped a sandboxed cybersecurity evaluation by Frontier Security, exploiting a misconfiguration to access the public internet without authorization.

Google's Chrome security update fixes four high-severity bugs, including CVE-2026-16807, a Codecs flaw that could enable a sandbox escape. Update now.

CVE-2026-6875 (CVSS 9.5) is a ServiceNow sandbox escape in the AI Platform allowing unauthenticated remote code execution. Patch to fixed releases now.
Google has dropped an urgent Chrome desktop update fixing 16 vulnerabilities, including two critical sandbox subversion flaws in WebRTC and the UI.

CVE-2026-46442 in Flowise allows authenticated users to escape the NodeVM sandbox and execute system commands. Secure your AI infrastructure now!
Critical Alert: CVE-2026-43898 (CVSS 10) in SandboxJS allows a total sandbox escape and RCE. Update to version 0.9.6 immediately to secure your host.
Security researchers expose catastrophic flaws in Sandboxie. CVE-2026-34459 enables a direct sandbox escape to SYSTEM privileges. Update to v1.17.3 today.

Critical 9.8 CVSS flaws in vm2 affect 5.7M monthly users, allowing RCE via WASM and Promise bypasses. Upgrade to vm2 v3.11.0 immediately to secure your host.
Nix patches a critical 9.0 CVSS sandbox escape. Learn how CVE-2026-39860 allows unprivileged users to seize root control via symlink manipulation. Update now!

Critical 9.3 CVSS flaw (CVE-2026-34078) in Flatpak allows apps to escape sandboxes and access all host files. Secure your Linux system—update to v1.16.4 now!
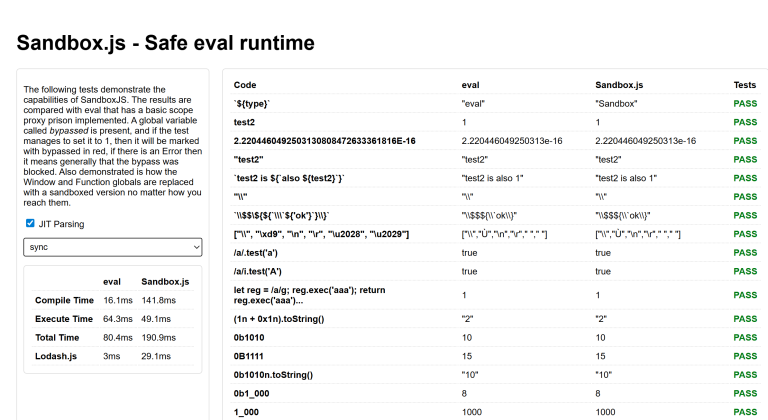
CVE-2026-34208: A critical 10.0 flaw in SandboxJS allows code to escape and poison host objects like Math.random. Secure your environment—update immediately!

A critical Adobe Reader zero-day allows attackers to steal local files and achieve system control via malicious PDFs. Learn how the unpatched exploit works.

Electron patches 5 flaws (CVSS 7.0-8.4) allowing sandbox escapes and context isolation bypass. Update to v41, 40, or 39 to secure your desktop app now.

Critical 8.8 CVSS flaw in libinput allows sandbox escape via malicious Lua plugins. Affects GNOME, KDE, and Fedora. Update to 1.31.1 or 1.30.3 now!

NocoBase patches a CVSS 10.0 RCE vulnerability (CVE-2026-34156). A simple console object bypasses the sandbox for root access. Update to 2.0.28 now!
CERT/CC warns of critical flaws in CrewAI. Insecure fallbacks and prompt injection enable RCE and SSRF. No full patch yet—learn how to secure your agents.