 Do Son
Scriban’s 9.1 CVSS flaw allows sandbox escapes in .NET apps via a cache bypass. Over 40M downloads affected. Update to version 7.0.0 to secure your templates.
Sandbox Escape

1,740 new vulnerabilities, 147 critical. From F5 crashes to a Trivy supply chain attack, here’s your high-priority triage list for March 2026.
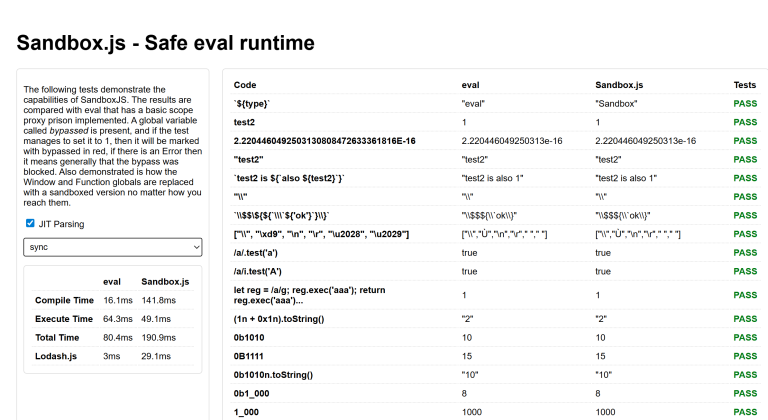
Critical 10.0 CVSS flaw in SandboxJS (CVE-2026-26954) allows attackers to escape the sandbox and achieve Remote Code Execution. Patch to version 0.8.34 now.

n8n patches three critical 9.4 CVSS vulnerabilities (CVE-2026-27497, 27577, 27495) allowing remote code execution via Merge nodes and sandboxes. Update now!

ServiceNow patches a critical 9.2 CVSS RCE vulnerability (CVE-2026-0542) in its AI sandbox. Unauthenticated users could execute code remotely. Patch now!

Google releases Chrome v145.0.7632.116 to patch high-severity flaws in Media, DevTools, and the Tint graphics engine. Update now to prevent memory leaks.

Critical SandboxJS flaw CVE-2026-25881 allows sandbox escape via prototype pollution. Malicious code can modify host logic & execute RCE. Update to v0.8.31.
Critical SandboxJS flaws (CVSS 10.0) allow sandbox escape & host takeover via prototype pollution. Update to v0.8.29 immediately to stop code execution.

Critical Jinjava flaw CVE-2026-25526 (CVSS 9.8) breaks sandbox security. Attackers can execute Java code via template loops. Update to v2.8.3 now.
CVE-2026-24002 (CVSS 9.1) allows RCE in Grist via Pyodide sandbox escape. Update to v1.7.9 now and ensure Deno protection is active.
CVSS 10 flaw CVE-2026-23830 in SandboxJS allows RCE via unpatched Async functions. Attackers bypass all limits. Update to v0.8.26 immediately.
Critical n8n RCE (CVE-2026-1470) lets attackers bypass sandbox defenses via malicious expressions. CVSS 9.9. Check versions 1.123.17 & 2.x now.

CVSS 9.8 vm2 flaw (CVE-2026-22709) affects 3.7 million users, allowing total sandbox escape via async functions. Update to v3.10.2 immediately.

CVE-2025-14026: Attackers can reconstruct a crippled Python runtime in Forcepoint DLP to execute arbitrary code. Update now to remove the vulnerability.

CVE-2025-68668: A critical n8n flaw lets attackers escape the Python sandbox for full RCE. Learn how this bridge failure leads to total system compromise.

Kaspersky found a Chrome zero-day (CVE-2025-2783) and sandbox bypass being exploited by Operation ForumTroll to deploy Memento Labs (Hacking Team) commercial Dante spyware against Russian targets.

Google has paid out its highest-ever Chrome bug bounty of $250,000 for a critical sandbox escape flaw that could bypass multiple security layers.

A critical flaw (CVE-2025-54782, CVSS 9.4) in NestJS's devtools-integration package allows attackers to execute code on a developer's machine via a malicious website.

CISA added four actively exploited vulnerabilities—including zero-days in CrushFTP, Chrome, and SysAid—to its KEV Catalog, urging immediate remediation for critical systems.

Team46 (TaxOff) is exploiting a Google Chrome sandbox escape zero-day (CVE-2025-2783) to deploy the multi-layered Trinper malware via phishing campaigns

PoC exploit for CVE-2025-31258 in macOS RemoteViewServices shows sandbox escape risk. Fixed in Sequoia 15.5. No active exploitation reported yet.

Microsoft uncovers CVE-2025-31191, a macOS sandbox escape exploiting security-scoped bookmarks. Apple patched it in March 2025.