Brazilian Magecart Group Hits Convertr Ecommerce Platform in Plausible Analytics Supply Chain Attack
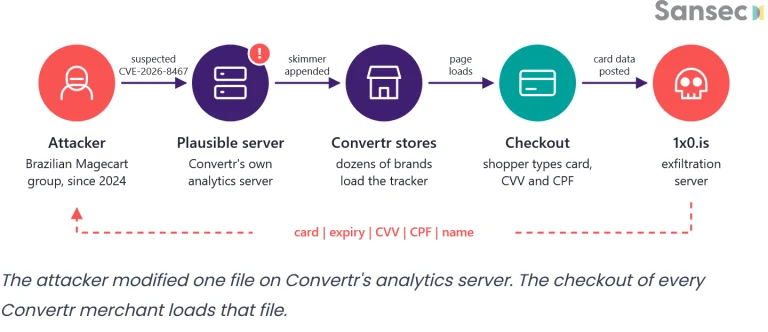
Sansec uncovers a Convertr supply chain attack. See how a Plausible Convertr supply chain attack planted a Magecart card and CPF skimmer on stores.
An Adobe Commerce vulnerability, CVE-2026-75650 (CVSS 10), enables unauthenticated arbitrary code execution and is exploited in the wild. Patch now.
StyleSmuggler, a Magento zero-day, gives unauthenticated remote code execution and is exploited in the wild. No patch yet. Mitigate now.
Attackers exploit CVE-2026-71362, an unauthenticated Adobe Commerce account takeover flaw (CVSS 9.1). Details and PoC are public. Patch now.
PolyShell Exposed: Public PoC and active exploitation disclosed for critical Magento RCE. With no official patch, your storefront is at risk. Secure it now!
A 2026 "technological ascension" in web skimming uses WebRTC to steal credit cards via UDP, bypassing CSP and WAF. Five global billion-dollar firms hit.
Active exploitation alert: The PolyShell flaw in the Magento REST API allows unauthenticated RCE via malicious images. Learn how to protect your store now.
Sansec uncovers a keylogger on a major US bank's employee portal. 200,000 staff at risk of credential theft via hidden "side door" malware.
Adobe has released an emergency patch for a critical Magento flaw, SessionReaper (CVE-2025-54236). The bug could allow automated attacks against thousands of online stores.
A large-scale supply chain attack has injected backdoors into e-commerce software, potentially affecting 500-1,000 stores. Sansec urges immediate checks.