
 Do Son
A High-severity OpenVPN flaw (CVE-2025-10680) in beta versions allows script injection on Unix-like clients (Linux, macOS). Malicious DNS/DHCP arguments can execute arbitrary commands on the client side.
script injection
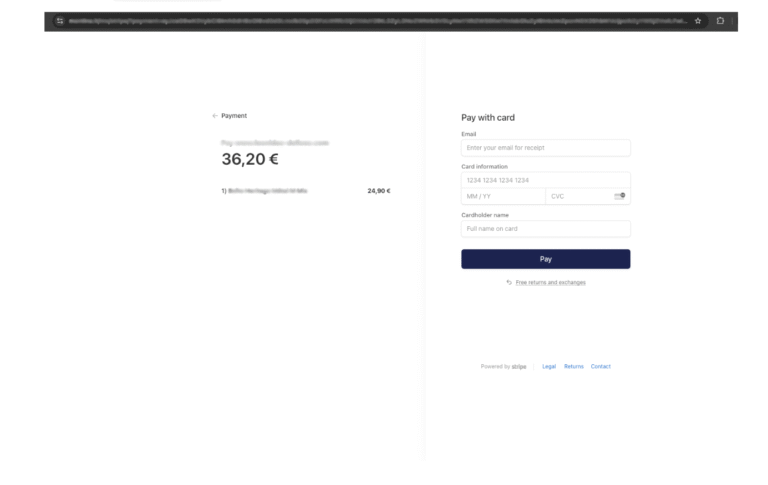
Attackers exploit JSONP flaws in Google APIs to inject malicious scripts into e-commerce sites, silently redirecting users to fake payment pages.

Cisco warns of SD-WAN flaws (CVE-2025-20147, CVE-2025-20221) with available proof-of-concept exploit code, posing risks of XSS and traffic bypass.