
 Do Son
Critical and high-severity flaws in Python's tarfile module allow arbitrary filesystem writes and bypasses. Update to the latest patched version immediately.
security advisory
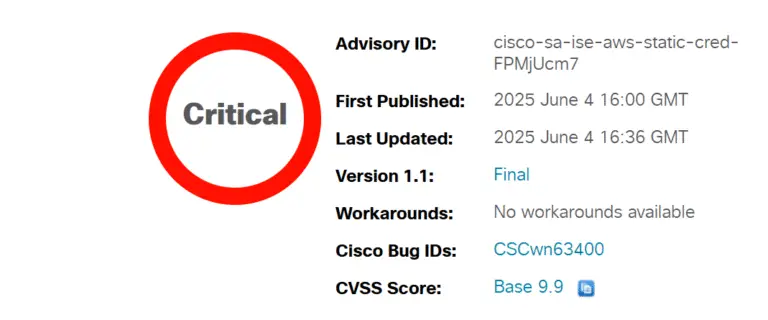
CVSS 9.9 flaw in Cisco ISE cloud deployments with public PoC exploit enables remote attacks on AWS, Azure, and OCI. Patch now.

ABB warns of a critical session fixation vulnerability (CVE-2024-13967) in EIBPORT V3, allowing unauthorized access. Update to firmware 3.9.9 immediately.

Critical CVSS 9.6 vulnerability in IBM QRadar & Cloud Pak for Security exposes systems to RCE & DoS. Patch immediately to secure your platforms.

High-severity flaws (CVE-2025-20298 & CVE-2025-20297) impact Splunk Enterprise & Universal Forwarder. Learn how to protect your data.

A new DoS vulnerability (CVE-2025-48866) found in ModSecurity WAF can crash your web application. Update to 2.9.10 immediately!

ISC uncovers security flaws in its Kea DHCP server, including privilege escalation and data leakage. Update to Kea 2.4.2, 2.6.3, or 2.7.9 immediately.

Ivanti patches CVE-2025-22462, a critical CVSS 9.8 auth bypass flaw in Neurons for ITSM. Risk of full admin access. Patch or restrict IIS access now.

CVE-2024-26809 affects Linux nftables with a double-free bug in nft_pipapo_destroy, enabling kernel-level exploitation and potential root access.

A security flaw in code-server can expose your VS Code sessions. Learn how attackers can steal credentials and what to do.

Two flaws in Mitel SIP phones—CVE-2025-47188 and CVE-2025-47187—enable remote command execution and file uploads, putting enterprise networks at risk.

Critical CVE-2024-11186 in Arista CloudVision Portal allows authenticated users broader network actions. Patch or mitigate now.

Cisco patches CVE-2025-20188, a CVSS 10 flaw in IOS XE WLCs, enabling unauthenticated remote file uploads and root-level command execution.

SonicWall urges urgent updates to SMA 100 Series devices after critical post-auth vulnerabilities expose systems to file deletion and command injection.

Ubiquiti warns of critical RCE flaw in UniFi Protect Cameras (CVE-2025-23123); update firmware and app to prevent potential network compromise.

OpenCTI flaw CVE-2025-24977 allows RCE and secret exposure via webhooks. Patch to v6.4.11 to protect Docker/Kubernetes deployments.

A critical XXE vulnerability (CVE-2025-2905) in WSO2 API Manager allows attackers to read files and cause DoS. Patch WSO2-2016-0151 is the solution.

CVE-2025-0217 flaw in BeyondTrust PRA allows session hijacking via local auth bypass. Upgrade to version 25.1+ to prevent exploitation.

Commvault updates its March advisory after detecting nation-state threat activity in Azure; no data breach confirmed, advanced defenses deployed.

Critical DoS vulnerability (CVE-2025-30194) impacts PowerDNS DNSdist 1.9.0-1.9.8 with DoH. Upgrade to 1.9.9 or use h2o provider.

CERT@VDE reveals CVE-2025-3200 in Wiesemann & Theis devices: outdated TLS protocols expose Com-Server models to interception and man-in-the-middle attacks.

CISA warns of critical vulnerabilities in Planet Technology products, including command injection and hardcoded credentials, allowing attackers to manipulate devices.