
 Do Son
NETSCOUT advisory reveals critical vulnerabilities in nGeniusONE, including hardcoded credentials & XSS. Update to version 6.4.0 b2350 or later immediately.
security advisory

ConnectWise addresses a critical ViewState code injection flaw in ScreenConnect. If machine keys are compromised, RCE is possible. Update immediately!

High-severity Redis vulnerability (CVE-2025-21605) allows unauthenticated users to cause DoS. Upgrade to patched versions or apply mitigations to protect your server.

GitLab releases critical security updates 17.11.1, 17.10.5, 17.9.7 to fix high-severity XSS, account takeover risks. Upgrade now to protect your GitLab instance.

Critical SonicWall flaw (CVE-2025-32818) in SSLVPN can crash firewalls, leading to DoS. Update your Gen7 devices now!

TP-Link WR841N routers are vulnerable to a stored XSS attack. Update firmware and change your password to protect your device from potential admin password theft.

Zyxel releases patches for USG FLEX H firewalls to address critical vulnerabilities. Learn about the security flaws and how to protect your network.

A critical vulnerability (CVE-2025-1976) in Brocade Fabric OS allows a local admin user to execute arbitrary code with root privileges. Update immediately!

Cisco patches CVE-2025-20236, an RCE flaw in Webex App exploitable via crafted links. Users urged to update to avoid command execution risks.
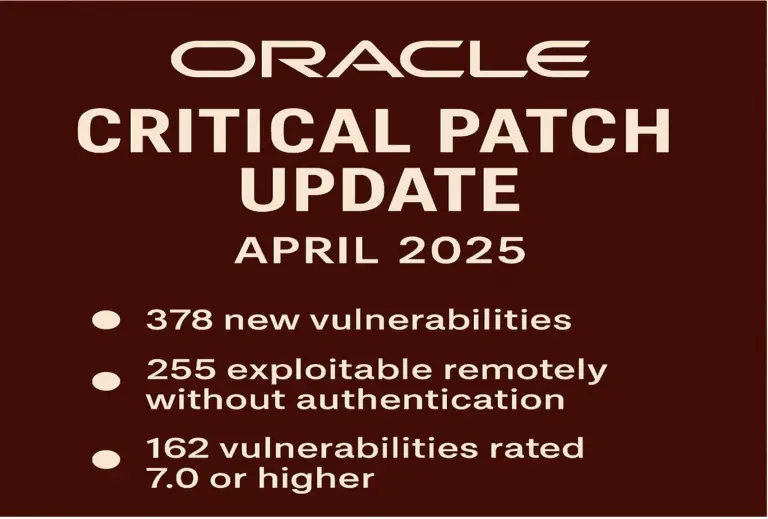
Oracle's April 2025 CPU delivers 378 security patches across its product suite. Learn about critical vulnerabilities and the urgent call to update.

Discover how Windows 11 vulnerabilities CVE-2025-24076 and CVE-2025-24994 allow unprivileged users to gain system privileges via DLL hijacking.

iFAX Solutions discloses a critical remote code execution vulnerability (CVE-2025-1782) affecting HylaFAX and AvantFAX due to improper sanitization

Perl has a heap buffer overflow (CVE-2024-56406) vulnerability in the "tr" operator, potentially causing DoS. Update to Perl 5.40.2 or 5.38.4 to fix

Dell has released a security advisory addressing vulnerabilities in PowerScale OneFS, including potential for takeover of privileged accounts and denial of service. Upgrade information and workarounds are provided.
CISA has added critical vulnerabilities affecting Windows CLFS (CVE-2025-29824) and Gladinet CentreStack (CVE-2025-30406) to its Known Exploited Vulnerabilities Catalog. Learn about the threats and the urgent need to apply patches.Sources and related content

Siemens ProductCERT issued a security advisory detailing critical vulnerabilities in the SENTRON 7KT PAC1260 Data Manager. The flaws could allow remote attackers to execute code, bypass authentication, and more.

A security flaw in Apache's mod_auth_openidc module can expose protected web content to unauthenticated users. Patch or mitigate to secure your server

Fortinet has addressed a critical vulnerability (CVE-2024-48887) in FortiSwitch that allows unauthenticated attackers to change admin passwords. Upgrade to the latest version to secure your devices.

Siemens security advisories detail a critical authentication vulnerability (CVE-2024-54092) in Industrial Edge Devices, allowing for potential impersonation