
 Do Son
SentinelOne discovered how new TraderTraitor macOS backdoors hit IT firms. Learn how TraderTraitor macOS backdoors use weaponized Terraform files.
SentinelOne
Bypassing Terminal Protections: New SHub “Reaper” Variant Abuses AppleScript to Loot macOS Endpoints

Bypassing Terminal Protections: New SHub “Reaper” Variant Abuses AppleScript to Loot macOS Endpoints
SentinelOne exposes the SHub Stealer "Reaper" variant. It bypasses Apple's latest Terminal paste mitigations to hijack crypto wallets and corporate documents.

Iranian group Seedworm infiltrates global firms using automated Node.js scripts and DLL sideloading via trusted binaries. Protect your credentials now!
SEQRITE Labs uncovers Operation IconCat, a campaign by UNG0801 using spoofed SentinelOne and Check Point icons to deploy PYTRIC and RUSTRIC in Israel.

Storm-0249 IAB abuses the SentinelOne EDR process via DLL sideloading to evade detection. The group uses LoLBin tools for fileless execution and sells access to ransomware groups like LockBit.

SentinelLABS and Beazley expose PXA Stealer, a Python-based infostealer campaign targeting 62 countries with stealthy DLL sideloading, decoy files, and Telegram-based data exfiltration.

SentinelOne uncovers a new macOS.ZuRu variant using a trojanized Termius app. It gains persistence via LaunchDaemon and deploys a Khepri C2 beacon for remote control.

SentinelLABS exposes China-nexus APTs (ShadowPad, PurpleHaze) targeting SentinelOne and over 70 organizations in extensive cyber-espionage.
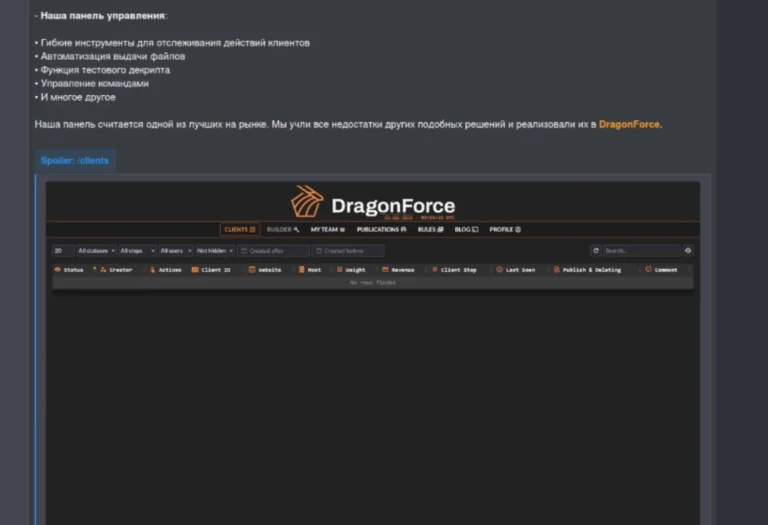
DragonForce ransomware cartel targets UK retailers with Conti-based payloads, RansomBay leaks, and phishing attacks, warns SentinelOne report.

SentinelOne reveals real-world attacks from DPRK, ransomware groups, and Chinese APTs, exposing evolving threats facing cybersecurity vendors in 2025.