 Do Son
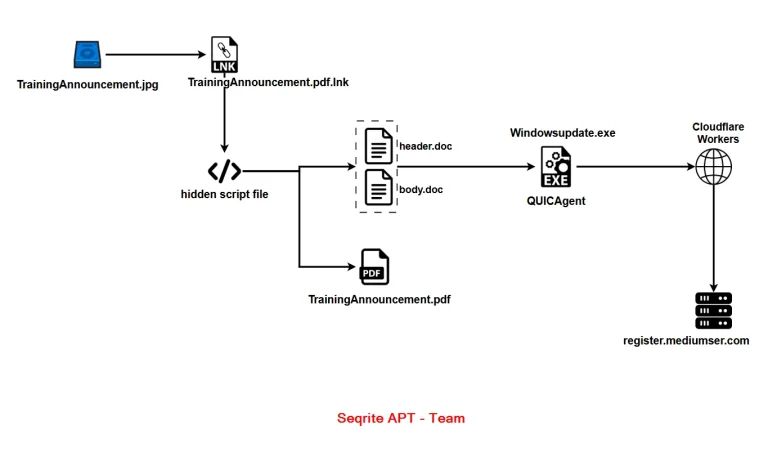
Seqrite links Operation QUICSILVER to a China-nexus actor deploying the QUICAgent Go backdoor against Myanmar government targets via a VHD lure.
Seqrite

Seqrite ties a Rare Werewolf phishing campaign to Russian aerospace firms, using a fake invoice to plant AnyDesk for stealthy remote access.

Threat actors are using RAR archive phishing to deploy Thailand healthcare malware. The campaign targets hospitals to steal credentials and sensitive data.

Seqrite discovered a campaign using SVG smuggling and a fake Colombian court lure to deploy AsyncRAT. The SVG executes JS to stage a malicious HTA file, evading detection.

Ransomware groups are hijacking legitimate RATs like AnyDesk and Splashtop to gain stealthy persistence, spread laterally, and disable antivirus software in enterprise networks.

A new report reveals HijackLoader, a Malware-as-a-Service loader. It uses advanced evasion and anti-analysis techniques to deliver stealers and other payloads.

A new report reveals Noisy Bear, an APT group targeting Kazakhstan’s oil and gas sector with spear-phishing and multi-stage malware, mimicking internal communications.