 Do Son
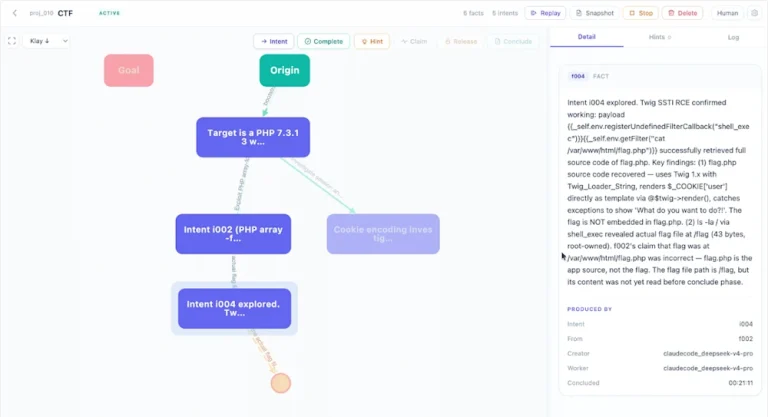
ReliaQuest details an AI agent attack that used one exposed endpoint and the Cairn platform to achieve a full server takeover in under 24 hours.
Server Takeover
Hackers exploit CVE-2026-35029 in the wild. Prevent a LiteLLM vulnerability server takeover and safeguard exposed secrets.

An Oracle WebLogic vulnerability, CVE-2026-60702 (CVSS 9.9), allows full server takeover. Oracle patched nine flaws, five critical. Update now.

Oracle's July 2026 patch fixes 11 Oracle WebLogic Server vulnerabilities. CVE-2026-60206 rates CVSS 9.9 and allows full server takeover. Patch now.

Public PoC code and full details are out for a 9.8 CVSS flaw in Nginx UI (CVE-2026-33032). With no official patch, servers are at risk. Secure yours now!
AVideo faces a security crisis with 5 unpatched critical flaws (CVSS 10.0). Attackers can hijack streams and execute code. Learn how to protect your server.