 Do Son
Apply the latest ServiceNow vulnerabilities patch to fix three flaws, including critical sandbox escape CVE-2026-103093 and password leak CVE-2026-103094.
ServiceNow
ServiceNow has patched five critical ServiceNow vulnerabilities, including an unauthenticated SQL injection flaw. Update your instances to stay secure.
ServiceNow patched CVE-2026-18885, CVE-2026-18886, and CVE-2026-74820, code injection and SQL injection flaws rated CVSS 10, plus a CVSS 8.7 bug.

Attackers are exploiting a ServiceNow sandbox escape RCE in the wild. Public proof-of-concept details for CVE-2026-6875 pre-auth code execution are out.

CVE-2026-6875 (CVSS 9.5) is a ServiceNow sandbox escape in the AI Platform allowing unauthenticated remote code execution. Patch to fixed releases now.

ServiceNow patches a critical 9.2 CVSS RCE vulnerability (CVE-2026-0542) in its AI sandbox. Unauthenticated users could execute code remotely. Patch now!
Critical ServiceNow AI flaw (CVE-2025-12420) allows unauthenticated user impersonation. Self-hosted users: update Now Assist & Virtual Agent immediately.

Zoom's new Custom AI Companion ($12/month) brings agent-like AI to 16 business apps like ServiceNow, Jira, & Asana, offering real-time meeting summaries & task orchestration to boost productivity.
Explore CVE-2025-0337, an authorization bypass vulnerability in ServiceNow that risks sensitive data access within the Now Platform.

ServiceNow, a leading cloud-based enterprise platform, has recently addressed two significant flaws, CVE-2024-8923 and CVE-2024-8924
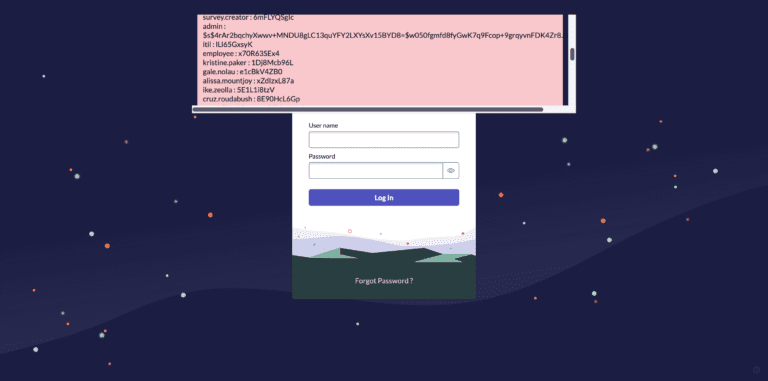
The most alarming of these flaws are CVE-2024-4879 and CVE-2024-5217, both carrying a critical CVSSv4 score of 9.3 and 9.2, respectively

Miessler believes the vulnerability to be an erroneous configuration in a ServiceNow component or widget named 'Simple List'