 Do Son
"SessionReaper" (CVE-2025-54236) targets Magento stores. Attackers use zombie tokens to gain root access. 200+ sites compromised. Patch now.
Session Hijacking
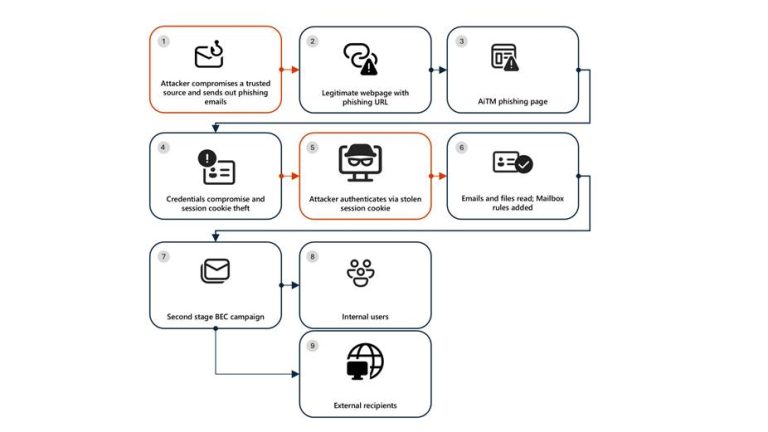
Microsoft warns of an AiTM phishing campaign targeting the energy sector. Hackers steal session cookies and abuse SharePoint to launch internal attacks.

ConnectWise patches critical Stored XSS (CVE-2026-0695) in PSA Time Entry notes. Vulnerability allows session hijacking. Update to version 2026.1 immediately.
Socket discovers 5 malicious Chrome extensions posing as productivity tools. They steal session tokens & block security teams. 2,300+ enterprise users at risk.

Urgent Patch: React Router CVE-2025-61686 (CVSS 9.1) exposes server files via session flaws. Fix XSS & Open Redirect bugs by updating to v7.9.6 now.

Unit 42 unmasks VVS Stealer, a Python-based threat using Pyarmor obfuscation to bypass AV, hijack Discord sessions, and steal browser credentials.

PrestaShop patches a 9.1 critical flaw (CVE-2025-61922) in the Checkout module. Attackers can hijack accounts via email. PoC available.

M-Files patches a high-severity flaw (CVE-2025-13008) that allows insiders to steal session tokens and impersonate users. Update to v25.12.15491.7!

Elastic patches a High-severity XSS flaw (CVE-2025-68385) in Kibana. Attackers can weaponize Vega visualizations to hijack sessions. Update now!

A Critical flaw (CVE-2025-11699) in nopCommerce allows attackers to hijack admin accounts by reusing session cookies that fail to invalidate upon logout. Update to v4.90.3 immediately.

Sophos exposed STAC3150, a campaign using fake "View Once" messages to deploy Astaroth banking trojan. The malware hijacks WhatsApp Web sessions via WPPConnect/Selenium for self-propagation.

Jenkins warned of a Critical SAML Plugin flaw (CVE-2025-64131) that allows session replay/hijacking due to a missing cache. Multiple plugins also expose API tokens in plaintext.
The Envoy Project has patched two new vulnerabilities: a use-after-free bug that can lead to DoS (CVE-2025-54588) and a session-hijacking flaw in its OAuth2 filter.

Multiple critical vulnerabilities (CVSS up to 9.8) in Alcatel-Lucent OmniAccess Stellar WLAN APs enable unauthenticated remote code execution and full device takeover. Patch immediately!

CISA adds critical CitrixBleed 2 (CVE-2025-5777, CVSS 9.2) to KEV, confirming active exploitation. Attackers are extracting session tokens to bypass MFA and hijack sessions on NetScaler ADC/Gateway

Citrix Bleed 2 (CVE-2025-5777, CVSS 9.2) is actively exploited to hijack sessions and bypass MFA on NetScaler ADC/Gateway. Patch immediately to prevent covert access and data theft.

Auth0 Next.js SDK flaw (CVE-2025-48947, CVSS 7.7) could expose session cookies via CDNs. Patch to v4.6.1 immediately to secure your app!

Critical vulnerability (CVSS 9.1) in Auth0-PHP SDK! This flaw threatens applications with over 16 million downloads. Update now to avoid brute force attacks.

SonicWall warns of active attacks on SMA 100 devices via CVE-2023-44221 and CVE-2024-38475. Users urged to update firmware immediately.

Dor Segal has revealed a critical vulnerability in FIDO2, the popular passwordless authentication standard