 Do Son
Two Apache Jackrabbit vulnerabilities, including critical session hijack flaw CVE-2026-92414 (CVSS 9.3), are fixed. Upgrade to 2.23.6 now.
Session Hijacking
Unit 42 exposes the new Gremlin stealer. It uses memory-resident techniques to hijack active browser session tokens and completely bypass MFA.
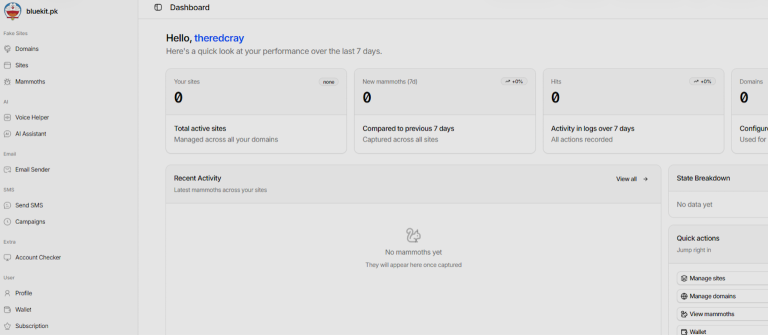
Varonis uncovers Bluekit, a new phishing-as-a-service kit using AI and 40+ templates to automate session hijacking and credential theft. See how it works.
Unauthenticated attackers can hijack mailcow admin sessions via a critical CVSS 9.3 Stored XSS in Autodiscover logs. Patch to version 2026-03b immediately.
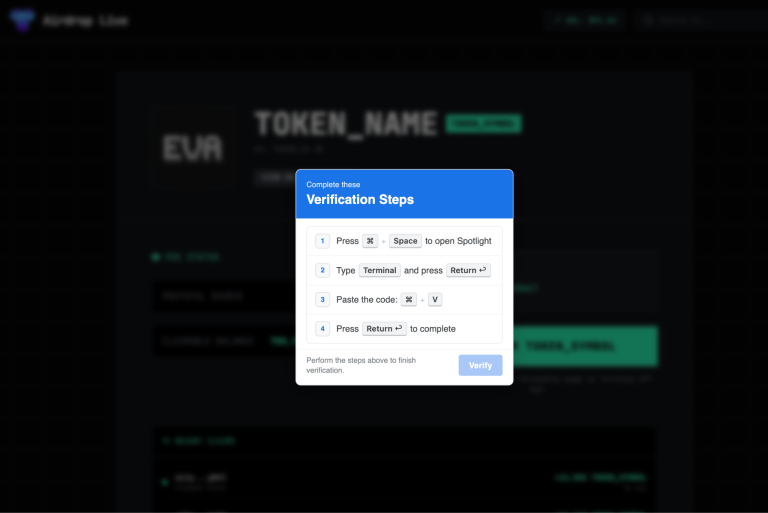
Netskope uncovers a ClickFix macOS campaign that holds the UI hostage to steal system passwords, Keychains, and 200+ browser extensions.

GitLab fixes high-severity GraphQL CSRF and Web IDE vulnerabilities in versions 18.11.1, 18.10.4, and 18.9.6. Protect your sessions and projects—patch now!
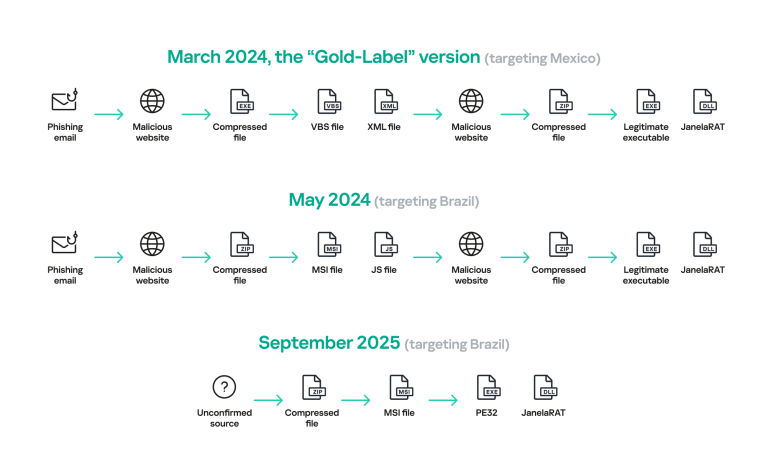
JanelaRAT targets banking users in Brazil and Mexico using window monitoring and fake updates. Learn how this 2026 threat bypasses MFA to hijack sessions.
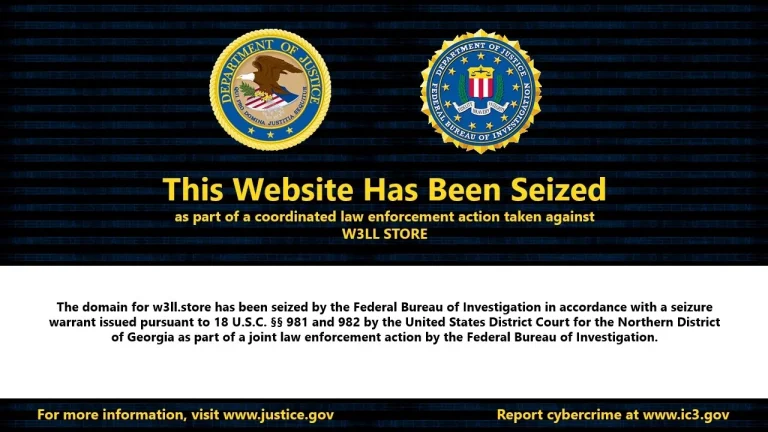
The FBI and Indonesia dismantle W3LL, a $20M phishing kit that bypassed MFA and hijacked live sessions. Learn about the takedown of this MaaS powerhouse.
Socket identifies 108 malicious Chrome extensions stealing Telegram sessions and Google IDs. 20,000 installs hit—audit your browser extensions immediately!
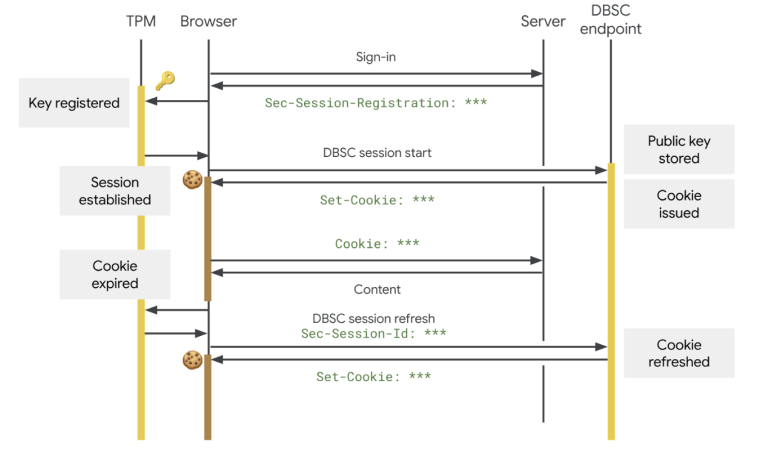
Google launches DBSC in Chrome 146, binding session cookies to hardware like TPM. Neutralize infostealers and stop session hijacking with this new standard.
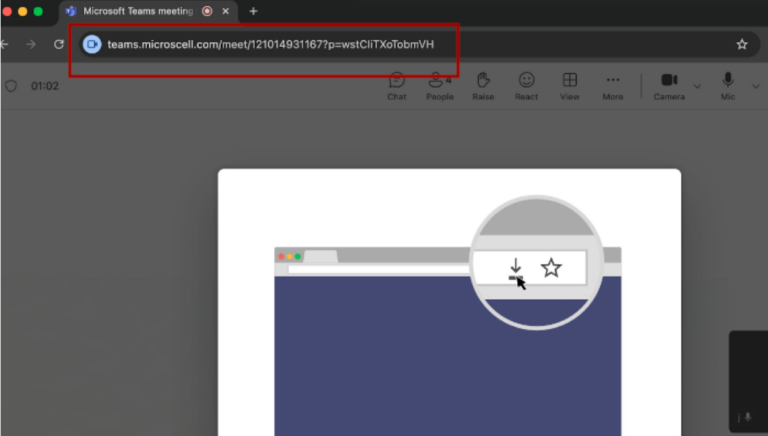
North Korean group UNC1069 (BlueNoroff) targets Web3 with fake Zoom/Teams links. 164 domains blocked. Secure your crypto assets and browser extensions now!
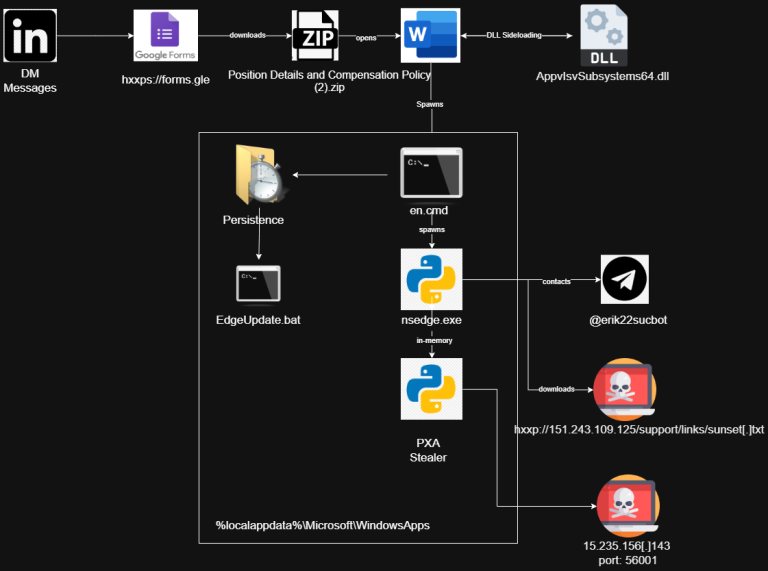
LinkedIn job seekers are being targeted by a sophisticated Vietnam-based group using PXA Stealer. This 100MB malware bypasses MFA and drains crypto wallets.
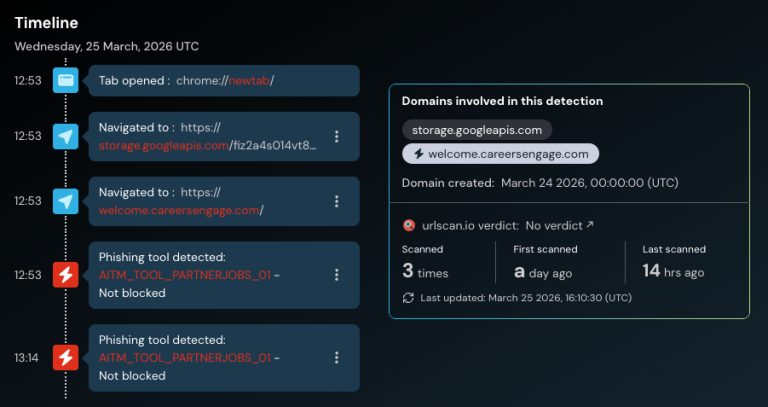
Researchers uncover a novel AiTM campaign targeting TikTok for Business. Attackers bypass MFA to steal Google SSO tokens and hijack corporate ad accounts.
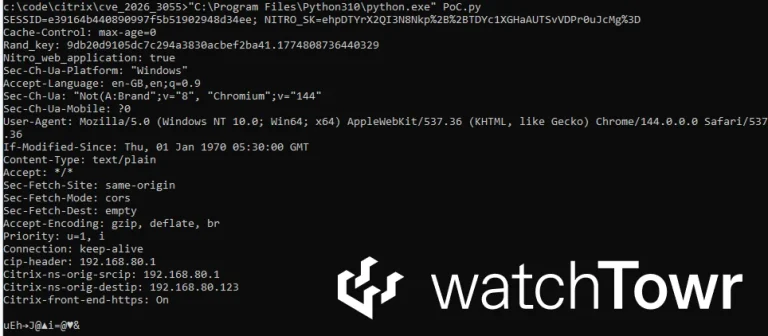
CISA adds Citrix NetScaler CVE-2026-3055 to KEV. This 9.3 CVSS flaw "bleeds" admin sessions via SAML. Federal agencies must patch by April 2, 2026.
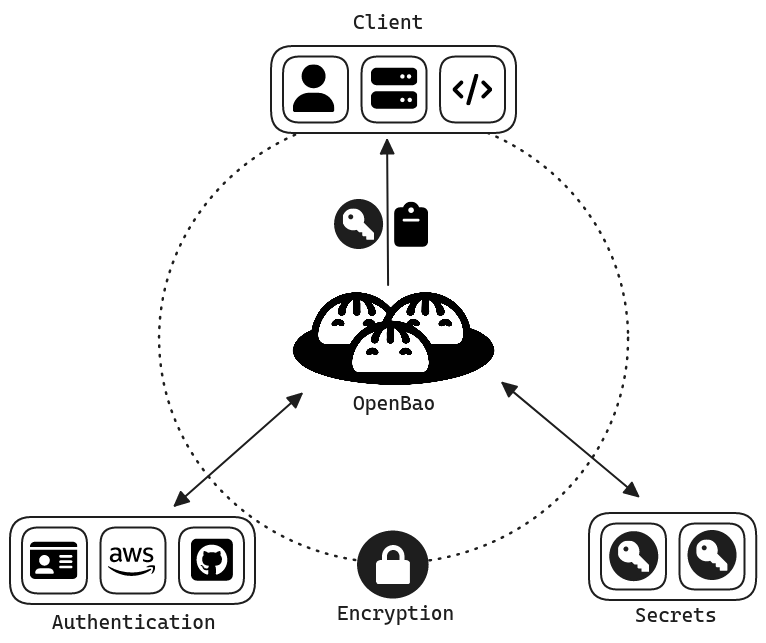
OpenBao patches critical 9.6 and 9.4 CVSS flaws in OIDC flows. Learn how "direct mode" enables session hijacking and XSS token theft. Update to 2.5.2 now.

Zabbix patches a high-severity blind SQL injection (CVE-2026-23921) in its API. Attackers can hijack sessions and steal data. Update to 7.4.6 or later today!
A 2026 audit of Perplexity Computer revealed exposed Claude Code tokens in config files. Learn how session-bound API keys could lead to massive billing debts.

Critical authentication flaws (CVE-2026-26288) in Everon's OCPP backend allowed hackers to hijack EV chargers, forcing a complete platform shutdown.
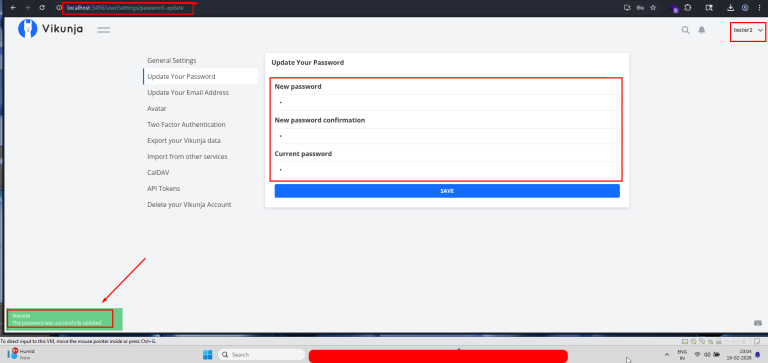
Vikunja v2.0.1 patches critical flaws (CVE-2026-27575 & 28268) where "immortal" reset tokens and persistent sessions allow attackers to hijack accounts forever.

Critical Undertow HTTP server flaw CVE-2025-12543 (CVSS 9.6) impacts HPE Telco Service Activator, allowing cache poisoning and session hijacking. Patch now.

Critical Fiber framework vulnerability CVE-2025-66630 (CVSS 9.2) causes silent UUID failures, leading to session hijacking. Update to v2.52.11 now.

Apache patches XSS (CVE-2026-23794) & XXE flaws in Syncope. Vulnerability allows session hijacking via login page. Update to v3.0.16 or v4.0.4 now.