 Do Son
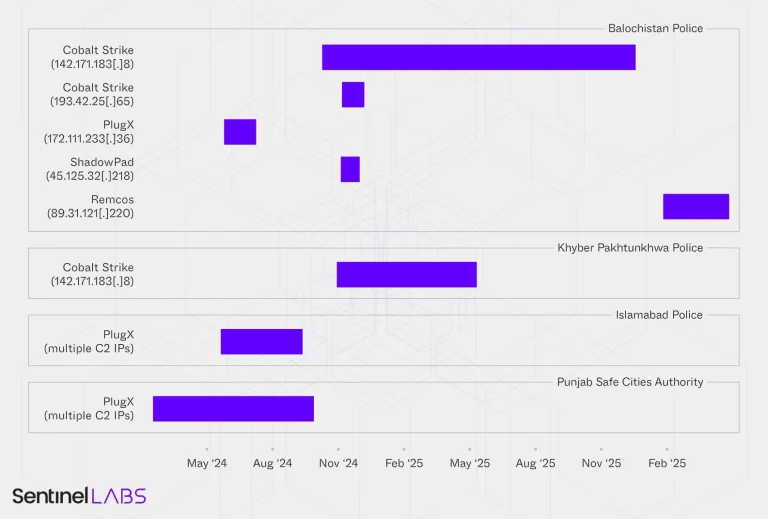
SentinelLABS found Chinese cyberespionage and India-nexus actors converging on Pakistani law enforcement, hitting Balochistan Police records and citizens.
ShadowPad
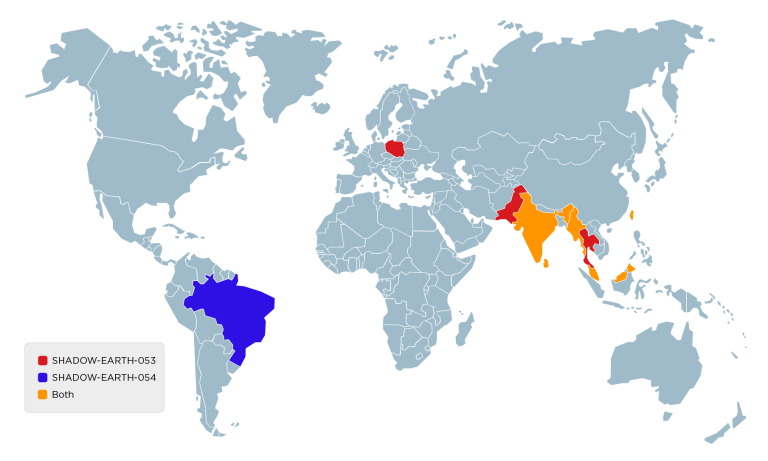
SHADOW-EARTH-053 is breaching governments and NATO using old ProxyLogon flaws and ShadowPad. Learn how this China-aligned group stays hidden via registry loading.

Cisco Talos exposes DKnife, a router malware that inspects traffic and swaps legitimate downloads for ShadowPad backdoors. Active since 2019.

Ink Dragon is weaponizing government servers in Europe using a relay-centric mesh. By hijacking IIS servers, they mask C2 traffic across global networks.

Threat actors are actively exploiting a new WSUS RCE flaw (CVE-2025-59287) to gain SYSTEM shells and deploy the dangerous ShadowPad backdoor. Patch immediately!

Trend exposed "Premier Pass-as-a-Service," a model where Earth Estries (access broker) and Earth Naga (APT36) share compromised network access to deploy ShadowPad in a coordinated espionage campaign.
Symantec Exposes Chinese APT Overlap: Zingdoor, ShadowPad, and KrustyLoader Used in Global Espionage

Symantec Exposes Chinese APT Overlap: Zingdoor, ShadowPad, and KrustyLoader Used in Global Espionage
Symantec exposed a complex Chinese APT network (Glowworm/UNC5221) deploying Zingdoor and ShadowPad across US/South American targets. The groups abuse DLL sideloading and PetitPotam for credential theft.

SentinelLABS exposes China-nexus APTs (ShadowPad, PurpleHaze) targeting SentinelOne and over 70 organizations in extensive cyber-espionage.

Explore the evolving threat of ShadowPad malware, now facilitating ransomware attacks linked to Chinese threat actors.

Discover ScatterBrain, a powerful obfuscating compiler employed by APT41. Understand its role in protecting the advanced modular backdoor POISONPLUG.SHADOW.

Discover the latest tactic employed by the Chinese APT group Stately Taurus. Learn how they abuse Visual Studio Code to gain unauthorized access to sensitive networks.

Discover the details of a recent cyberattack targeting a Taiwanese research institute, believed to be carried out by the Chinese state-sponsored group APT41