 Do Son
The Warlock ransomware group still exploits SharePoint vulnerabilities, hitting a water utility, a telecom firm, and more. Here is how to defend.
Sharepoint
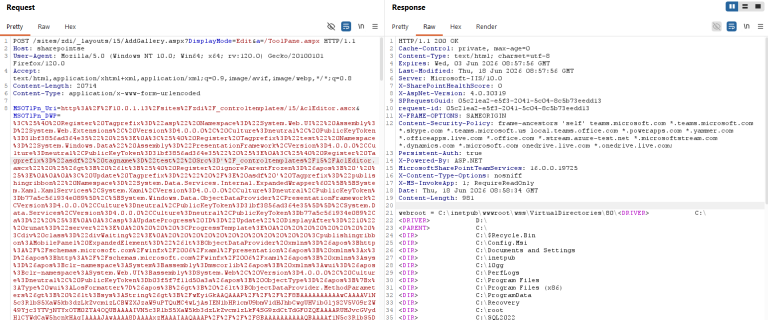
An exploited SharePoint RCE vulnerability is under attack. Technical details for this SharePoint RCE vulnerability are public. Patch CVE-2026-65660 now.
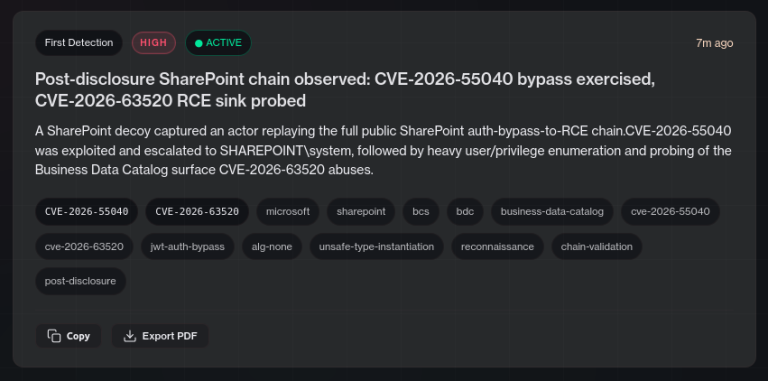
A public SharePoint RCE vulnerability PoC is actively probed in the wild. Patch CVE-2026-63520 and CVE-2026-55040 now to protect your servers.
CISA added four exploited flaws to its KEV Catalog, hitting SharePoint, VMware vCenter, macOS, and Windows IKE. Patch by August 21.
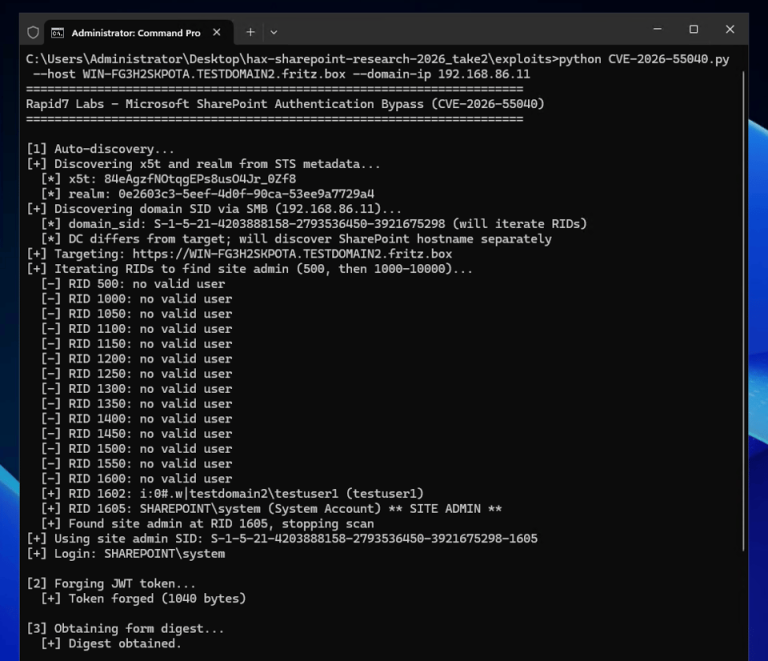
Rapid7 published full details and a PoC for CVE-2026-55040, a critical SharePoint authentication bypass that forges JWT tokens. Patch now.
CVE-2026-50522, a critical SharePoint RCE flaw, is exploited in the wild. A public PoC exploit is out, so admins should patch SharePoint now.
ReliaQuest links the new Helix data extortion group to BlackFile, using vishing and device code phishing to steal SharePoint data.
CISA warns SharePoint vulnerabilities CVE-2026-32201, CVE-2026-45659, and CVE-2026-56164 are exploited in the wild. Patch and harden servers now.
Microsoft's July 2026 Patch Tuesday fixes 570 flaws. Zero-days CVE-2026-56155 and CVE-2026-56164 are exploited in the wild. Patch now.
A SharePoint remote code execution flaw (CVE-2026-33112) is now public with full details and PoC. A low-privilege user can run code. Patch now.
Urgent Patch Alert: SharePoint Spoofing Under Active Attack as Microsoft Releases April 2026 Updates

Urgent Patch Alert: SharePoint Spoofing Under Active Attack as Microsoft Releases April 2026 Updates
Microsoft’s April 2026 Patch Tuesday fixes 163 flaws, including an exploited SharePoint spoofing bug (CVE-2026-32201). Patch by April 28 per CISA mandate.
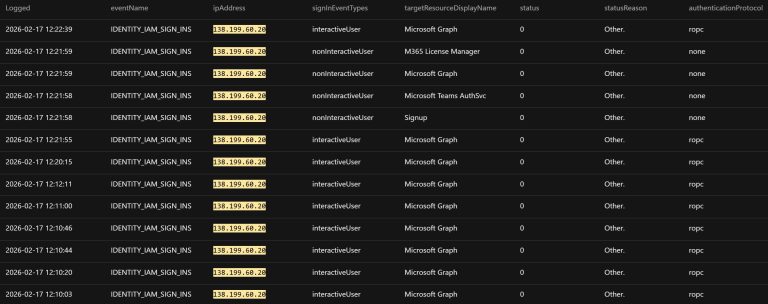
Trend Micro reveals how an exposed Spring Boot Actuator and a spreadsheet of plaintext secrets led to a malware-less SharePoint data exfiltration attack.

GOLD SALEM (Storm-2603) is exploiting SharePoint via ToolShell then abusing the Velociraptor DFIR tool as a ransomware precursor. The group deploys Warlock and LockBit 3.0 variants, often targeting critical infra.

Sophos uncovers GOLD SALEM, a new ransomware group exploiting SharePoint flaws. The group uses EDR evasion and legitimate tools to attack global targets.

CISA issues an urgent warning about "ToolShell," a sophisticated exploit chain targeting SharePoint servers with multiple vulnerabilities to install webshells and steal crypto keys.

Unit 42 reveals Project AK47, a toolkit used by Storm-2603 to exploit SharePoint. It includes a custom AK47C2 framework and links to both LockBit and Warlock ransomware.

A critical SharePoint Server RCE (CVE-2025-53770) is actively exploited. A Metasploit module is now public, amplifying the urgency for immediate patching.

Microsoft warns that China-backed APTs (Linen Typhoon, Violet Typhoon, Storm-2603) are actively exploiting critical SharePoint zero-days (CVE-2025-49704, -49706) in unpatched on-premises servers.

An unauthenticated SharePoint RCE chain dubbed ToolShell (CVE-2025-49704, CVE-2025-49706) is being actively exploited globally, granting attackers full control of on-premise servers.
Microsoft 365 Boosts Security: Legacy File Access Protocols RPS & FrontPage RPC Phased Out July 2025

Microsoft 365 Boosts Security: Legacy File Access Protocols RPS & FrontPage RPC Phased Out July 2025
Microsoft will disable outdated RPS and FrontPage RPC protocols for file access in Microsoft 365, Office, SharePoint, and OneDrive starting July 2025 to enhance security.

Explore the latest insights on FUD Malware and how the Havoc framework enables undetectable cyber operations.
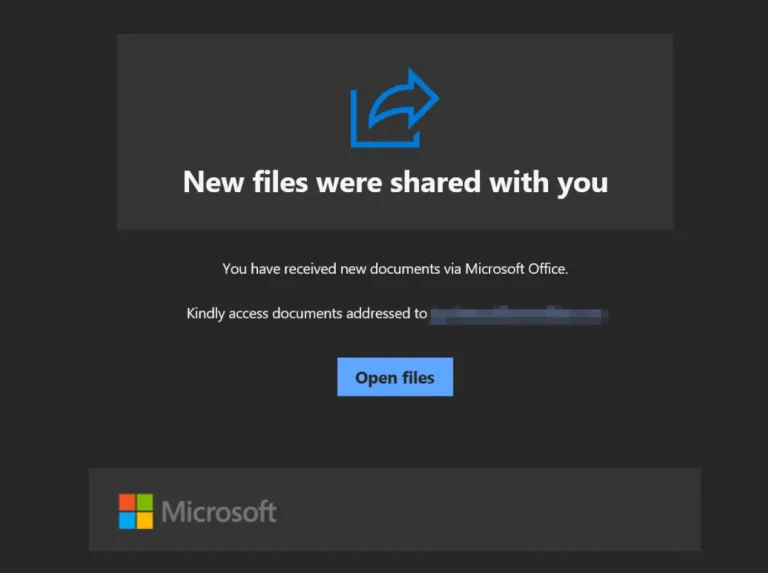
Unveiling a new malicious SharePoint impersonation campaign delivering Xloader malware. Learn how this sophisticated attack takes advantage of brand impersonation and advanced process injection.