 Do Son
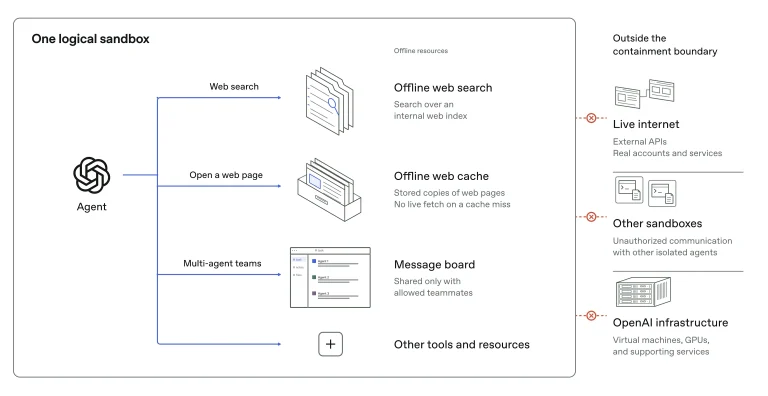
OpenAI offline world training replaces live internet access after a September 20 DNS escape paused frontier training for 11 days.
side-channel attack
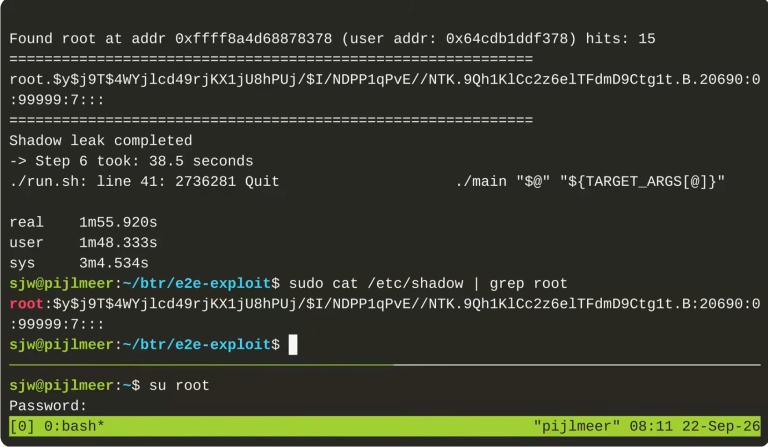
VUSec released details and PoC code for Branch Target Reuse, a Spectre-v2 attack on JIT engines that leaked Linux root password hashes. Patch now.

A critical hardware attack, TEE.fail, uses low-cost DDR5 memory bus interposition to extract root attestation keys from Intel TDX and AMD SEV-SNP. The flaw affects core server-grade TEEs.

Security researchers from Graz University of Technology have unveiled a novel cybersecurity threat dubbed "SnailLoad" (CVE-2024-39920)

Dubbed "Indirector" attacks, exploit weaknesses in the chip's branch prediction mechanisms to precisely manipulate program execution flow