 Do Son
The SideCopy APT campaign deploys custom RATs. Learn how the SideCopy APT campaign malware exploits mshta to target academic and government networks.
SideCopy

DRAT V2, a new Delphi-compiled RAT from TAG-140 (SideCopy/Transparent Tribe), is targeting Indian government entities with expanded post-exploitation and refined C2 techniques.

The SideCopy APT group is evolving its tactics, using new methods like MSI packages and custom malware to target critical Indian sectors, including railways and oil & gas
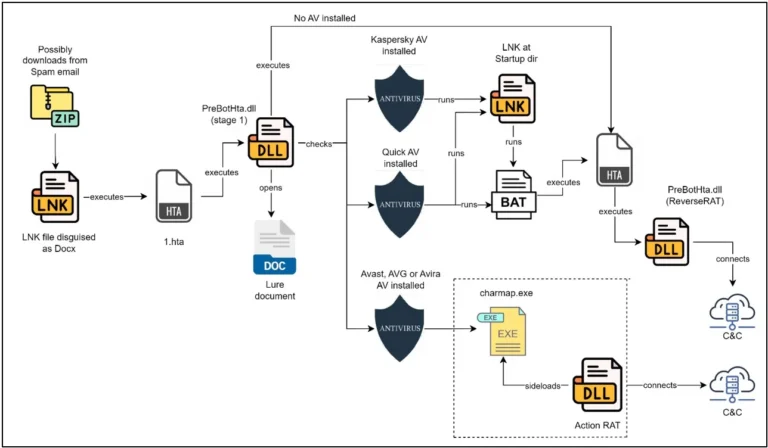
Upon further investigation, CRIL uncovered the use of malicious LNK files in the SideCopy malware campaign. These files, once executed

The report highlights a coordinated campaign waged by the notorious SideCopy and Transparent Tribe (APT36) groups