 Do Son
Silent Push uncovered a North Korean IT worker scam recruiting proxies. Learn how a North Korean IT worker uses Discord to bypass corporate hiring filters.
Silent Push
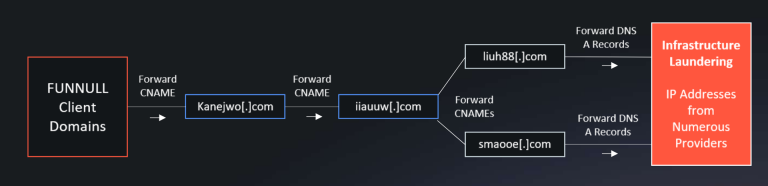
Triad Nexus has built a $300M fraud engine using "Infrastructure Laundering" on AWS and Google. See how they use geo-fencing and CNAME chains to evade the law.

Silent Push's Traffic Origin technology strips away VPN masks to reveal the true location of threat actors. Detect North Korean & Russian proxies now.

Silent Push reveals a massive SystemBC botnet with 10,000+ infected IPs. The SOCKS5 proxy malware hit government domains and uses bulletproof hosting.

New Magecart campaign mimics Stripe forms to skim credit cards. Malware hides from admins & tricks users with fake errors. Active since 2022.

Silent Push details how cybercriminals and APTs are misusing DDNS services for stealthy C2 servers, phishing, and malware delivery. Dozens of high-profile groups are involved.

A new malware loader, CountLoader, is linked to Russian ransomware groups. The malware uses phishing lures impersonating the Ukrainian National Police to deliver payloads.

A new report uncovers 45 previously unknown domains linked to the Chinese APT group Salt Typhoon. The findings reveal a long-term, multi-year espionage infrastructure.

A global e-commerce fraud campaign uses thousands of fake retail websites mimicking Apple, Nordstrom, and more, to steal credit card data, with roots tied to Chinese developers.

Silent Push uncovers "GhostVendors," a massive online fraud operation using 4,000+ fake domains and Facebook ads to impersonate brands and scam consumers.

Silent Push uncovers crypto scam using Twitter ad loophole to spoof CNN and Apple, luring users into buying fake iTokens via misleading redirects.
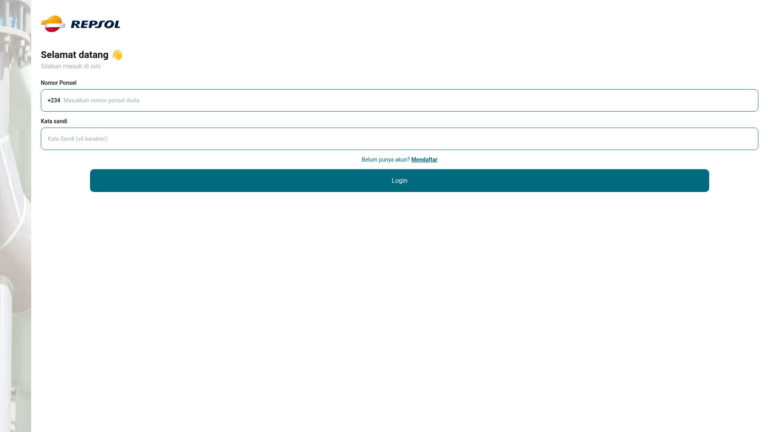
Power Parasites targets users with job and investment scams using fake domains mimicking Siemens, Repsol, Netflix, and more, Silent Push reports.