 Do Son
Security researchers uncovered the new PAPERMILL cybercrime cluster. Learn how the PAPERMILL cybercrime cluster uses tax lures to deploy VenomRAT.
Silver Fox

Silver Fox fake software installers impersonate Razer and Edge to disable Windows Defender and deploy malware. See how the campaign works.
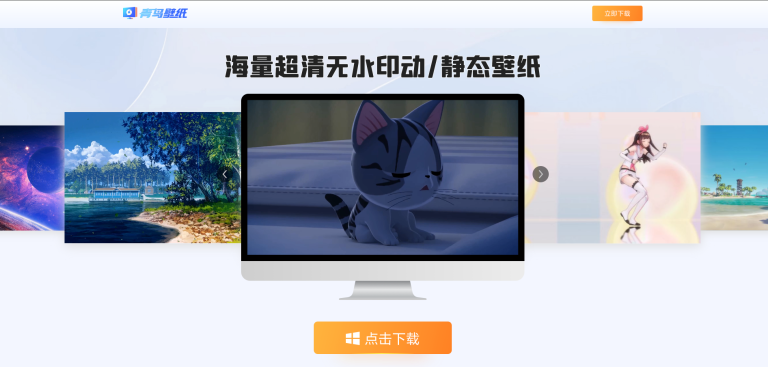
Kaspersky uncovered a ValleyRAT backdoor adware campaign using signed wallpaper apps to drop malware. Learn how to protect your systems.

Silver Fox's Ghost distributor delivers MODBEACON, a modular Rust trojan, to picked targets in Operation Phnom Penh, per Qianxin. Here's what to know.
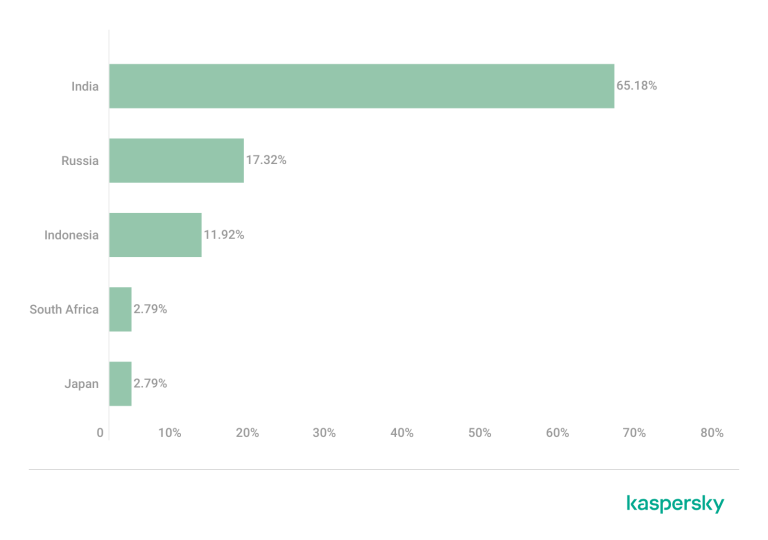
Silver Fox targets India and Russia with tax-themed phishing and the new ABCDoor backdoor. Learn how this Python-based threat hijacks screens and data.

Sekoia TDR reveals Silver Fox's latest tactics. From tax-themed phishing to WhatsApp clones, this China-based group combines espionage with financial theft.

Chinese APT Silver Fox is using a Cyrillic false flag in an SEO poisoning campaign impersonating Microsoft Teams. The attack installs ValleyRAT for espionage and financial fraud.

A new report reveals the Silver Fox APT group is abusing a Microsoft-signed vulnerable driver to disable endpoint security and deploy the ValleyRAT backdoor.

Netskope uncovers Sainbox RAT (Gh0stRAT variant) and Hidden rootkit delivered via fake software installers to Chinese users, leveraging DLL sideloading and sRDI for stealth.

Silver Fox APT is conducting a multi-stage espionage campaign, leveraging backdoored medical software like Philips DICOM viewers to infect healthcare organizations

Discover the ValleyRAT malware and how the Silver Fox APT group utilizes the PNGPlug loader to execute their cyber-espionage attacks.