 Do Son
Operation Endgame disrupts the SocGholish malware network, seizing EUR 41M in crypto and 326 servers. WordPress site owners must act now.
SocGholish

Arctic Wolf Labs reveals Russian GRU Unit 29155 using SocGholish to deploy RomCom malware against a US firm with ties to Ukraine.

Silent Push exposes SocGholish as a MaaS platform for Initial Access Brokers. The malware, disguised as fake updates, fuels top-tier Russian ransomware groups like Evil Corp.
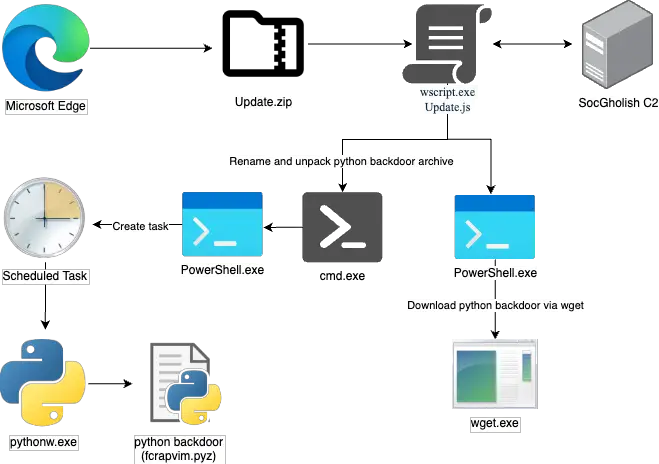
eSentire TRU discovers a campaign combining SocGholish malware with RansomHub affiliates, using fake updates and Python backdoors to compromise networks.
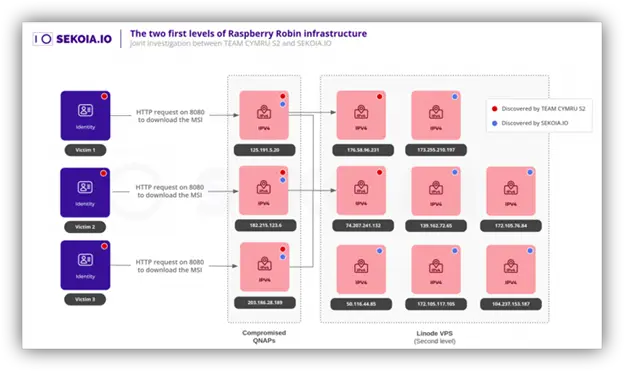
Explore the evolution of Copy Shop Worm into a sophisticated threat linked to cybercriminals and state-sponsored actors.

Explore the SocGholish MaaS framework and its role in malware distribution. Learn about its techniques and impact on cybersecurity.

Explore the activities of TA2726 and TA2727 as they utilize fake browser updates to spread malware and deceive users.

Uncover the TAG-124 traffic distribution system used by cybercriminals to spread malware, phishing pages, and fake browser updates.

Learn about a sophisticated attack campaign targeting WordPress websites and delivering SocGholish Windows malware to unsuspecting users.

Huntress has recently uncovered a new wave of malicious activities involving the well-known SocGholish or FakeUpdates malware.

eSentire's Threat Response Unit (TRU) has detailed a sophisticated intrusion campaign by the SocGholish cyber threat group