 Do Son
A new malicious PyPI package wave highlights evolving supply chain attacks. Learn how to protect your CI/CD pipelines from credential theft.
Socket Threat Research

Urgent: 84 TanStack npm packages hijacked to harvest GitHub Actions secrets. Over 12M weekly downloads impacted. Audit your CI/CD pipelines and rotate tokens.

Socket uncovers a Packagist supply chain attack targeting Vietnamese OphimCMS streaming sites with trojanized themes linked to sanctioned entity FUNNULL.
Socket researchers uncover "ImToken Chromophore," a malicious Chrome extension using fake branding and homoglyphs to steal crypto wallet seed phrases.

Socket researchers uncover a Packagist supply chain attack where fake Laravel utility packages secretly install a persistent Remote Access Trojan (RAT).
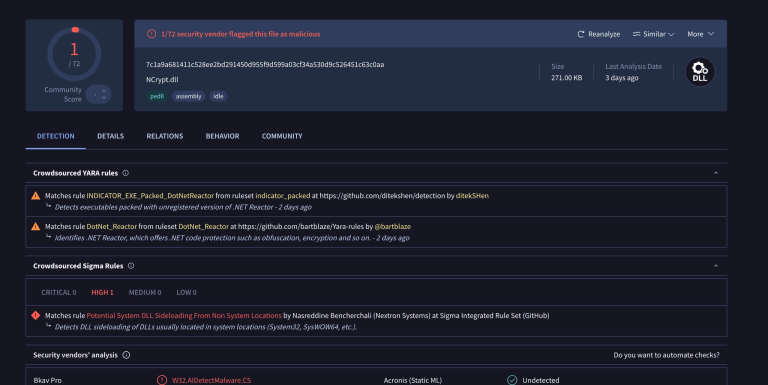
Socket researchers uncover a NuGet supply chain attack using "NCryptYo" to hijack ASP.NET apps. Attackers inject backdoors into production authorization layers.
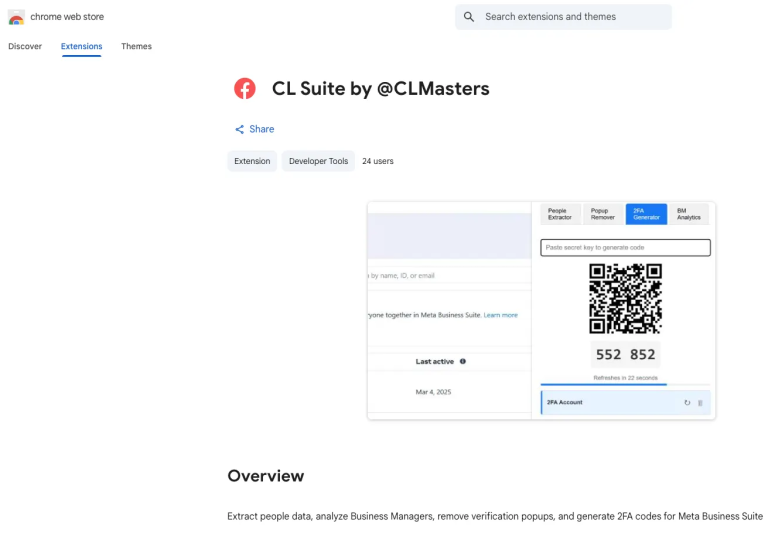
"CL Suite" Chrome extension steals Meta Business 2FA seeds & data. Attackers bypass security even after uninstall. Reset 2FA immediately.

Malicious PyPI package "sympy-dev" impersonates SymPy to install XMRig miners via fileless execution. Check your dependencies immediately.
Socket discovers 5 malicious Chrome extensions posing as productivity tools. They steal session tokens & block security teams. 2,300+ enterprise users at risk.

Malicious Chrome extension "MEXC API Automator" hijacks API keys to drain crypto wallets. Russian-linked malware hides withdrawal permissions. Remove now.