
 Do Son
A SonicWall security incident exposed firewall configuration backups from some MySonicWall accounts. The company is warning users to check for exposure and apply remediation.
SonicWall

Australian authorities issue an urgent alert on a critical SonicWall SSL VPN flaw actively exploited by Akira ransomware, urging immediate patching.
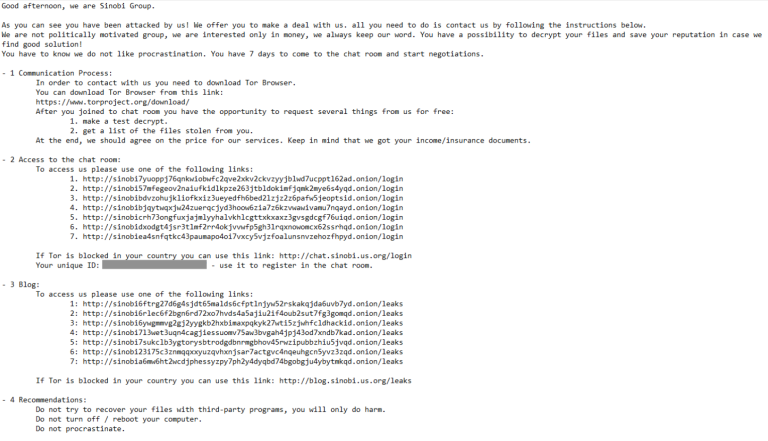
A new report links Sinobi Group ransomware to Lynx, a potential rebrand. The group is using strong encryption and targeting compromised SonicWall VPN credentials to gain access.

Huntress and other firms warn of a likely zero-day vulnerability in SonicWall VPNs. Attackers are bypassing MFA and deploying Akira ransomware within hours of initial access.

SonicWall discloses CVE-2025-40600, a critical format string vulnerability in SonicOS SSL VPN, allowing unauthenticated remote DoS attacks on Gen7 firewalls. Update to 7.3.0-7012 or later.

SonicWall SMA 100 series has buffer overflow and XSS flaws (CVSS 6.3-7.3) exploitable by unauthenticated attackers via the web interface. Update to 10.2.2.1-90sv immediately!

SonicWall warns of CVE-2025-40599 in SMA 100 series, allowing authenticated admins to upload arbitrary files, potentially leading to RCE.

Microsoft and eSentire expose SilentRoute, a backdoored SonicWall SSL VPN NetExtender client distributed via SEO poisoning, stealing credentials and breaching networks.

Google's GTIG uncovers UNC6148 using stolen credentials and a new rootkit, OVERSTEP, to gain persistent access to end-of-life SonicWall SMA 100 series appliances.

SonicWall and Microsoft uncover a campaign distributing a trojanized NetExtender VPN client that steals credentials by bypassing certificate validation.
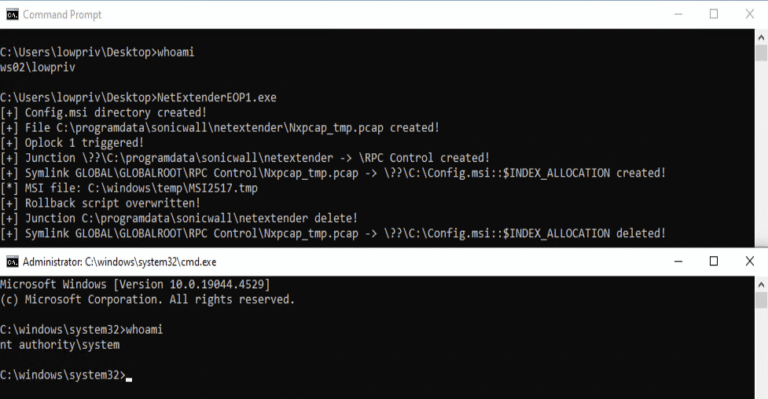
High-risk LPE vulnerabilities in SonicWall NetExtender for Windows (CVE-2025-23009, CVE-2025-23010) allow SYSTEM access or DoS. Patch immediately to version 10.3.2.

SonicWall fixes CVE-2025-40595, a high-severity SSRF flaw in SMA1000 appliances. Patch now to block remote encoded URL exploitation.

SonicWall urges urgent updates to SMA 100 Series devices after critical post-auth vulnerabilities expose systems to file deletion and command injection.

CVE-2024-38475 and CVE-2023-44221 form an exploit chain targeting SonicWall SMA appliances, enabling remote admin hijack and code execution.

SonicWall fixes CVE-2025-2170, an SSRF flaw in SMA1000 appliances. Users urged to update to platform-hotfix 12.4.3-02925 or later to stay secure.

SonicWall warns of active attacks on SMA 100 devices via CVE-2023-44221 and CVE-2024-38475. Users urged to update firmware immediately.

Critical SonicWall flaw (CVE-2025-32818) in SSLVPN can crash firewalls, leading to DoS. Update your Gen7 devices now!

CISA issues urgent alert on actively exploited SonicWall SMA100 vulnerability (CVE-2021-20035). Federal agencies must mitigate by May 7, 2025
SonicWall has patched three vulnerabilities (CVE-2025-23008, CVE-2025-23009, CVE-2025-23010) in its NetExtender VPN client. Update to version 10.3.2 or later to prevent privilege escalation and unauthorized access.

Learn about the CVE-2024-53704 vulnerability in SonicWall firewalls and its severe impact on network security and data protection.

To extract the victim's session, researchers release a Ruby proof-of-concept (PoC) exploit code for CVE-2024-53704 , which is available here.
SonicWall warns of critical vulnerability CVE-2025-23006 in SMA1000 AMC and CMC. Attackers can exploit this pre-authentication remote command execution flaw.