 Do Son
GoSerpent backdoor drives a patient cyber espionage campaign against Southeast Asian governments, stealing files and credentials since at least 2021.
Southeast Asia
Chinese-speaking actors deploy TinyRCT backdoor attacks against Southeast Asian government and energy sectors. Discover the CL-STA-1062 cyber espionage tactics.
The Triple-Headed Dragon: Inside the Three-Cluster Chinese Cyberespionage Campaign Targeting SE Asia

The Triple-Headed Dragon: Inside the Three-Cluster Chinese Cyberespionage Campaign Targeting SE Asia
Unit 42 uncovers a massive 3-cluster cyberespionage campaign by China-aligned actors in SE Asia using USBFect, Hypnosis loaders, and stealthy RATs.

Check Point reveals "TrueChaos," an espionage campaign exploiting a TrueConf zero-day (CVE-2026-3502) to drop malware via fake updates. Patch to 8.5.3 now.
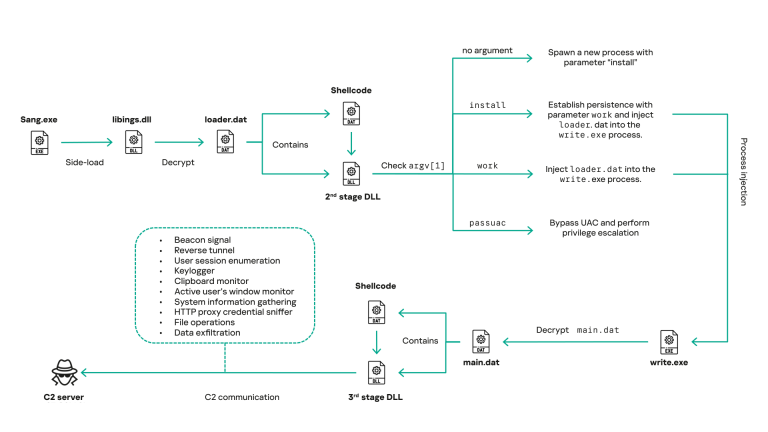
HoneyMyte (Mustang Panda) shifts to real-time surveillance using updated CoolClient. New 2025 campaign uses Pixeldrain for stealthy exfiltration.

New Osiris ransomware hits Southeast Asia, linking to Inc & Medusa groups. It uses BYOVD tactics to disable defenses. Unrelated to the 2016 variant.

Kaspersky unmasks HoneyMyte's 2025 campaign, using the ProjectConfiguration.sys kernel rootkit to deploy ToneShell backdoors with elite stealth.

CyberArmor exposed Autumn Dragon, a China-nexus APT using a WinRAR path traversal flaw (CVE-2025-8088) and DLL sideloading to deploy a Telegram C2 backdoor for espionage in Southeast Asia.

Cyfirma exposed Android/BankBot-YNRK, a Trojan cloning Indonesia’s Digital ID app to steal credentials and crypto assets. It uses anti-emulation checks and JobScheduler for persistent device takeover.

LAB52 uncovers a sophisticated phishing campaign delivering DeedRAT, a modular backdoor by Chinese APTs, targeting Southeast Asian governments via vulnerable AV software.

Earth Kurma APT campaign targets Southeast Asian governments and telecoms using rootkits, loaders, and cloud services to steal sensitive data.

The Billbug group targeted Southeast Asian organizations using advanced tools & DLL sideloading. This report details their sophisticated espionage campaign.